growth in organizations actively running AI workloads in Kong AI Gateway over roughly one year.

AI is appearing across your business faster than security can keep up.
AI adoption is outrunning control
The AI footprint is expanding faster than governance can catch up.
Production AI is scaling now. The control gap is already visible.
did not have AI-specific governance controls in place across the organizations studied.
Third-party agentic attacks
External AI can touch your systems before your team sees it.
SAMI identifies unknown AI and agent interactions, understands what they are trying to access, and protects the systems and data behind them.
External AI
AIThird-Party Agent
↗Autonomous Service
APIAI-Driven Request
SAMIINBOUND AIIdentify • Evaluate • Protect
Protected enterprise
◎Websites & Apps
APIAPIs, MCP & Tools
▦Systems & Data
SAMI identifies Rogue/Malicious Agentic Attacks on your systems and protects you
Brands We Work With
Why familiar controls are not enough
You can block an AI website.
You cannot block AI from appearing everywhere else.
Most organizations already have useful controls. The problem is that AI now crosses browsers, applications, APIs, data, tools and business workflows. SAMI is designed to add the missing AI context and enforcement layer, not replace the security stack that already works.
“We block.”
That blocks one destination. Users can move to AI search, embedded SaaS AI, browser tools, desktop copilots, APIs and thousands of other AI-enabled services. Domain blocking is not AI governance.
“We only allow approved AI.”
Approved AI can still receive customer data, source code, credentials or regulated information that your policy says should never be submitted. Approval is not control of every interaction.
“We already have DLP and IAM.”
They remain important. But AI risk increasingly depends on intent and action: what the model or agent is trying to accomplish, which tool it is calling and whether this specific action should be allowed.
“We are not using AI.”
You can still have an AI security problem. Third-party autonomous agents can probe and interact with websites, APIs, applications, MCP endpoints and digital services whether or not you deploy your own models or agents.
One continuous operating model
Security should move with the AI.
SAMI connects discovery, policy, inline protection, workflow intelligence, testing and continuous reassessment into one control loop.
01
DISCOVER
Find approved and Shadow AI.
02
UNDERSTAND
Identify model, user, data, tools and context.
03
GOVERN
Apply security, privacy and corporate policy.
04
ATTACH
Place the right protection inline.
05
CONTROL
Allow, modify, hold, approve or block.
06
OBSERVE
Reconstruct the full AI workflow.
07
TEST
Continuously validate the attack surface.
08
ADAPT
Reassess when AI or policy changes.
The SAMI ASDR architecture
Three systems working as one control layer.
Customers should not have to stitch together one product for Shadow AI, another for guardrails, another for agents, another for MCP and another for audit. SAMI connects the intelligence and enforcement around the full AI interaction.
Sensors + Sensor Policy Engine
See AI. Understand it. Govern it.
Continuously discover AI across browsers, endpoints, applications, network/API and cloud. Correlate identity, application, model, data, RAG, MCP, tools and agents, then determine which corporate policies and controls should apply.
Approved + Shadow AI
AI identity & context
Governance policies
Dynamic attachment
Security Engine
Protect AI from attack. Control what AI can do.
Apply security to prompts, responses, sensitive data, RAG, MCP and agent actions and defend enterprise systems from incoming third-party agents. SAMI can evaluate the interaction before it reaches the model, tool, application, database or business system.
Prompt + response
Data privacy
RAG Defender
MCP + agentic security
Workflow Intelligence
Understand what the AI actually did.
A single event rarely tells the whole story. SAMI follows the journey across users, models, RAG, MCP, tools, APIs, applications and downstream actions,so security and audit teams can understand intent, decisions and outcome.
Day-in-the-life view
Full execution path
Policy decisions
Outcome evidence
Enterprise alignment +
proof
proof
Built for live AI.
Aligned for enterprise control.
SAMI is designed to secure live AI interactions with measurable decision speed, broad attack coverage, privacy controls and mapped governance support.
OWASP LLM Top 10
MITRE ATLAS
EU AI Act
NIST AI RMF
ISO 42001
ISO 27001
SOC 2 Type II
Zero Trust
99%
Prompt-attack detection efficacy
~30ms
Low-latency detection target
300+
AI attack techniques tracked to protect live workflows
300+
Privacy elements monitored to protect AI data use
65+
Compliance controls mapped for AI governance alignment
70%
of live MCPs showed exposed risk paths in SAMI testing
* Validation and coverage figures shown are Autnhive results. Publish methodology and production benchmarks with customer-facing evidence packages.
AI risk runs in three directions
Protect your AI. Control your AI.
Defend against everyone else's AI.
AI can be attacked. Your own AI can drift or take an unsafe action. And third-party autonomous agents can probe, call, access or act against your digital systems even when you do not deploy AI internally.
Protect AI from attack
Secure the AI interaction itself against attacks designed for models, retrieval systems and agentic workflows.
Prompt injectionJailbreaksData extractionRAG poisoningMCP abuseAgent hijacking
Protect the enterprise from AI going rogue
An AI does not need malicious intent to create risk. SAMI evaluates what an AI or agent is trying to do before it becomes a business action.
Unsafe tool callsExcess permissionsBad instructionsSensitive dataUnintended actions
Defend against third-party agent attacks
External and third-party agents can probe websites, call APIs, invoke MCP tools and attempt actions against enterprise systems. SAMI's Inbound AI Sensor identifies the AI/agent context and routes the interaction through policy and security before it reaches the protected resource.
WebsitesApplicationsAPIsMCPToolsDatabasesBusiness systemsThird-party agents
Autonomous security & governance
AI changes too fast to secure one ticket at a time.
A new model appears. A SaaS application adds AI. An MCP server exposes another tool. An agent receives new permissions. SAMI is designed to detect the change, determine the required controls, attach protection and keep watching.
The operating idea: security moves with the AI environment instead of waiting for the next assessment.
Workflow Intelligence
A log tells you an event happened.
Workflow Intelligence tells you what the AI accomplished.
An agent may retrieve data, call a model, use an MCP tool, invoke an API and then change a business record. Each step can look legitimate by itself. SAMI correlates the entire chain so security, compliance and business owners can understand what led to the outcome.
See Workflow Intelligence →Agent workflow · Customer record update
LIVE TRACE
User initiates requestAuthorized employee asks an AI assistant to update a customer account.
VERIFIEDModel interprets intentSAMI correlates the model, application, user and policy context.
OBSERVEDRAG retrieves customer contextSource access and retrieved data are recorded and evaluated.
ALLOWEDMCP tool requests a write actionAgent attempts to modify a protected field in the CRM.
APPROVALFinal outcome recordedApprover, policy decision, tool result and resulting business change are linked.
EVIDENCEAI Exposure · Prioritized
CONTINUOUS
External-facing AI · prompt manipulation pathValidated through attack simulation
FIX NOWMCP server · high-impact tool overexposedAgent can reach action outside intended scope
FIX NOWRAG source · untrusted content pathPotential retrieval poisoning path
SCHEDULEApproved model · controls validatedPolicy and security coverage confirmed
MONITORAI CTEM + Vulnerability Judge + attack simulation
Do not just protect AI.
Continuously test whether it can be broken.
SAMI AI CTEM extends the operating model from runtime protection into continuous exposure management, discovering AI assets and attack paths, validating weaknesses through simulation, prioritizing what matters to the business and re-testing after remediation.
LLMsMCPAgentsExternal-facing AIAI infrastructure
Explore AI CTEM →
Outcomes
One view of your AI environment.
One place to understand and control it.
See where AI exists, how it is used, what it can reach, what it did and where exposure remains.
See AI activity in context, stop attacks and unsafe actions, and move high-risk decisions into the SOC.
Deploy AI with controls that follow models, agents, RAG, MCP and workflow changes instead of slowing every release.
Turn policy into runtime enforcement and retain evidence of what data, policy and controls were involved.
Understand the AI footprint, business-impacting exposure and what the organization is doing to reduce it.
Straight answers
What SAMI ASDR is designed to do.
Clear answers to the questions buyers ask most often.
What is SAMI ASDR?
SAMI ASDR (AI Systems Detection & Response) is Autnhive's AI security, governance and control layer. It is designed to discover AI across the enterprise, understand its context, apply organizational policy, attach appropriate security controls, govern AI and agent actions, reconstruct workflows and continuously reassess exposure.
Can SAMI discover both approved AI and Shadow AI?
Yes. SAMI's sensor architecture is designed to identify AI activity across browser, endpoint, applications, network/API and cloud, then correlate the AI service or model with users, data, RAG, MCP, tools and agents.
Can SAMI govern approved AI, not just block unapproved tools?
Yes. An organization can allow an approved AI service while still enforcing rules around sensitive data, permitted users, allowed models, tool access, agent actions, geographic or privacy requirements and approval workflows.
How does SAMI protect AI from attack?
SAMI's security engine is designed to apply controls across prompts, responses, data, RAG, MCP and agent activity, including threats such as prompt injection, jailbreaks, sensitive-data extraction, RAG poisoning, MCP abuse and agent hijacking.
How does SAMI protect the enterprise from AI going rogue?
SAMI evaluates AI and agent actions in context before they reach underlying tools, applications, APIs, databases or business systems. Depending on policy and risk, the interaction can be allowed, modified, redacted, held, routed for approval or blocked.
Can SAMI protect an organization from third-party AI agents?
Yes. The SAMI Inbound AI Sensor is designed to identify and evaluate autonomous systems interacting with enterprise resources, including websites, applications, APIs, MCP servers, tools and business systems, even when the organization is not using AI internally.
What is SAMI Workflow Intelligence?
Workflow Intelligence correlates the full execution path of an AI interaction across users, applications, models, retrieved data, RAG, MCP, tools, agent actions, policies and outcomes. It helps answer not only what event occurred, but what the AI workflow actually did.
How does SAMI automate AI security and governance?
SAMI is designed to detect changes in the AI environment, classify the AI context, determine which security and governance policies apply, attach the appropriate control, enforce the decision, observe behavior and reassess as the environment changes.
Organizations & ecosystems Autnhive works with
Do you know everywhere AI is touching your business?
See what AI exists, what it can access, what it can do, where it is exposed and whether your policies are actually being enforced, before the next AI interaction becomes a business incident.
AI Discovery & Control
See every AI.
Control every interaction.
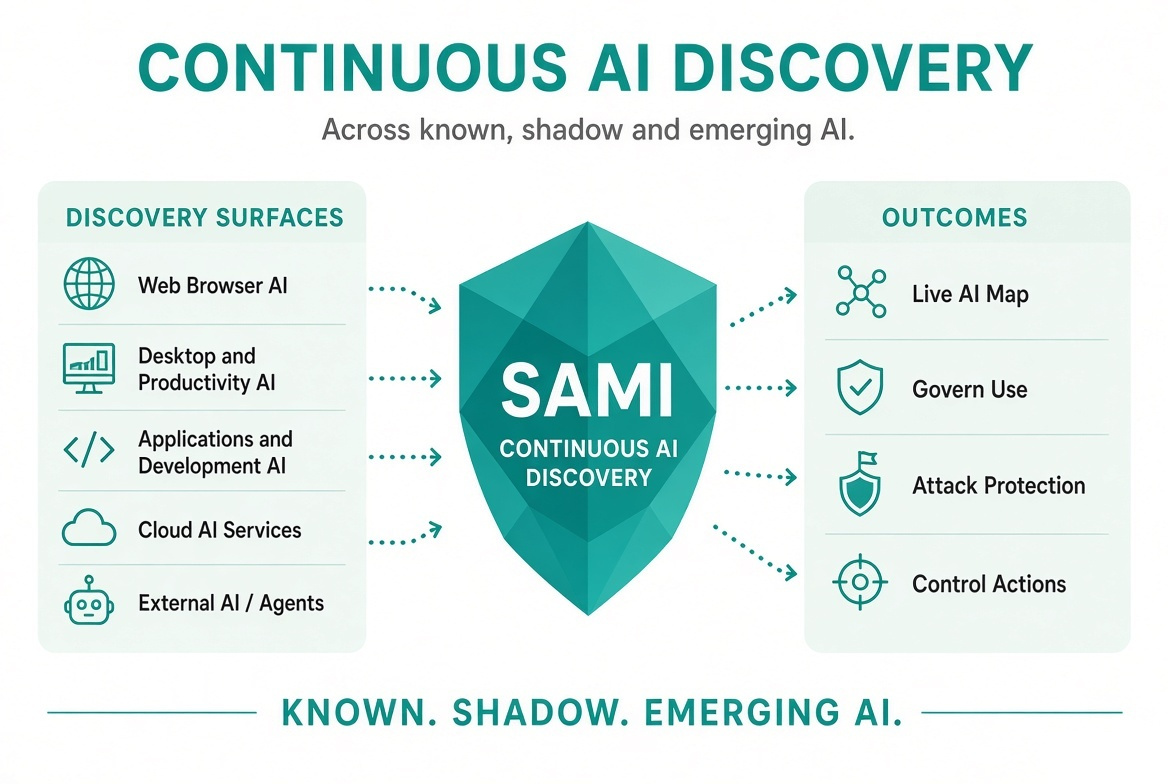
AI no longer arrives through one doorway. SAMI uses multiple sensors to discover AI across browsers, endpoints, applications, network/API traffic and cloud environments, then correlates the model, user, data, RAG, MCP, tools, agent permissions and actions. It also watches the other direction: external AI agents and autonomous systems coming into your business.
AI discovery & control
AI is already in the business. You need to see it as it appears.
Employees use it. Applications add it. Developers connect to it. Agents reach into data and tools. External AI can hit from outside. SAMI turns that changing footprint into control.
Sensor Fabric
Browser Sensor
Endpoint Sensor
Application / SDK Sensor
SAMIAI Map
One continuously updated view of AI across the enterprise.
Network / API Sensor
Cloud Sensor
Inbound AI Sensor
What SAMI delivers
See approved and Shadow AIFind browser AI, SaaS AI, developer AI, models, RAG, MCP and agents as they appear.
Understand the contextSee who is using the AI, what data it touches and what it is trying to do.
Apply policy to usageApproval is not enough. Govern how the AI is used and what it can access.
Select the right controlsMatch the AI path to the right prompt, privacy, RAG, MCP, agentic, inbound or CTEM controls.
Source: Kong, The State of AI Governance (2026), based on anonymized production traffic from Kong AI Gateway.
The SAMI sensor fabric
AI can appear almost anywhere.
Your visibility has to follow it.
SAMI combines complementary sensors so discovery is not tied to one browser domain, one application or one network path. The goal is a living AI map: what exists, who or what is using it, what it is connected to and what it is capable of doing.
Browser Sensor
Detect AI reached through websites, AI search, embedded SaaS assistants and browser-delivered experiences. Add policy around prompts, forms, uploads, downloads and other browser interactions where enforcement is required.
Chat AIAI SearchEmbedded SaaS AIUploads
Endpoint Sensor
Identify AI activity originating from desktop applications, developer tools, IDEs, CLIs, local models and agents. Correlate traffic with the process or workload responsible for the AI interaction.
Desktop AIIDEsCLILocal ModelsAgents
Application / SDK Sensor
Bring application and workload context into the AI map when AI is embedded inside approved software or custom applications. Connect application identity, workflow and AI calls to policy decisions.
SaaS AICustom AppsSDKWorkloads
Network / API Sensor
Identify model endpoints, gateways, SDK/API calls and AI traffic patterns across network paths. Correlate the connection with the calling process or application and route supported interactions through the appropriate control.
Model APIsGatewaysSDK CallsTraffic Attribution
Cloud Sensor
Discover AI services and workloads across cloud environments, including models, agents, RAG architectures, MCP services and customer-built AI applications. Continuously reassess as cloud resources change.
OCIAWSAzureGCPAI Workloads
AI Context Engine
Correlate findings from all sensors including the Inbound AI Sensor and turn separate sensor events into an understandable relationship: user or workload → application → model → data/RAG → MCP/tools → agent → action. That context is what makes policy enforceable.
UserModelDataToolsAction
INBOUND AI SENSOR
AI can come at your business even if your business is not using AI.
External autonomous agents, partner agents, customer agents and AI-powered systems can interact with your websites, applications, APIs, MCP endpoints, tools and business services. SAMI Inbound AI Sensor is designed to recognize the AI/agent context, understand the attempted action and place policy in front of the underlying enterprise system.
External AgentsAPIsWeb AppsMCPToolsBusiness Systems
External AI Agent
Partner / Customer Agent
Autonomous Service
SAMIINBOUND AI SENSOR
Application / API
MCP / Tool
Database / Business System
Sensor Policy Engine
Approval is not the policy.
How AI is used is the policy.
An approved model can still receive the wrong data. An approved agent can still attempt the wrong action. SAMI evaluates the AI interaction in context and applies your security, privacy, corporate governance and compliance rules at runtime.
Live policy decisionINLINE
AI serviceApproved enterprise GPTAPPROVED
UserCustomer Support · authorizedVERIFIED
Prompt dataContains customer PIIREDACT
Agent actionUpdate protected CRM fieldAPPROVAL
OutcomeAI stays usable. Policy stays enforced.CONTROLLED
The result
A living map of AI and a control point around how it interacts with your business.
Know where AI is, who or what is using it, what model is involved, what data and tools it can reach, what actions it can take, what external AI is coming in and what policy applies. When the environment changes, SAMI can reassess the control.
Proof + Compliance
Workflow Intelligence shows what happened.
Proof Ledger proves it.
AI governance cannot end with a policy document or an alert. SAMI connects the AI workflow, the policy decision, the security action and the resulting business outcome into evidence that security, compliance, audit and leadership can actually use.
AI evidence receiptVERIFIABLE
ActorAgent: support-resolution-07LINKED
DataCustomer record · PII redactedPROTECTED
Tool callCRM update · protected fieldAPPROVED
PolicyAI-CRM-Change-Control v4.2APPLIED
EvidenceTimestamp + workflow + decision + resultPROVED
FROM AI ACTION TO AUDITABLE EVIDENCEWorkflow → Decision → Proof → Compliance
63%
of breached organizations in IBM's 2025 study lacked an AI governance policy or were still developing one.
34%
of organizations with AI governance policies performed regular audits for unsanctioned AI.
Source: IBM Cost of a Data Breach Report 2025 / IBM Newsroom. Figures apply to the breach-study population described by IBM.
Workflow intelligence & proof
When someone asks what the AI did, you need a clear answer.
Workflow Intelligence shows the full AI journey. Proof Ledger preserves the policy, decision and outcome.
Day-in-the-life workflow
User / AppOrigin of the request
ModelAI service engaged
Data & RAGContext retrieved
MCP / ToolCapabilities requested
Business SystemTarget system touched
ActionOutcome recorded
Why it matters: the customer can understand which AI acted, what data it touched, what tool call it made, what policy applied and what happened next.
Evidence chain
InteractionPrompt, response, retrieval, tool request or action attempt begins the event.
DecisionSAMI records the context, risk evaluation, policy and control selected.
EnforcementAllow, modify, redact, hold, require approval or block is captured as part of the evidence.
ProofProof Ledger preserves the verifiable output for audit, compliance, forensics and accountability.
What the organization can prove
From “we have a policy” to “here is the evidence.”
AI interactions
Prompts, responses, model calls, security decisions, redactions and enforcement outcomes tied to the workflow.
Data & RAG
Which sources were accessed, what entered model context, what was protected and how data policy was applied.
Agents & MCP
Agent intent, tool requests, approvals, blocks, credentials, side effects and final business actions.
AI CTEM
Findings, attack validation, remediation, re-testing and evidence that exposure was reduced.
One evidence layer across the AI lifecycle
Security, privacy, governance and compliance finally share the same facts.
The same runtime evidence that helps security investigate an event can support privacy review, governance oversight, compliance mapping, customer due diligence and board reporting. The organization does not have to reconstruct the story from disconnected logs after the fact.
Security
What happened?
Trace the event, policy decision, attack path and enforcement outcome.
Privacy
What data moved?
Show what data was accessed, redacted, tokenized, blocked or permitted.
GRC / Audit
What control applied?
Connect policy and runtime evidence to the required governance framework.
Leadership
Is the risk reducing?
Connect exposure, remediation and control evidence to business impact.
Do not just log AI. Understand what it actually did.
User → application → model → RAG → agent → MCP → tool/API → database → business action.
Turn the workflow into proof →User → application → model → RAG → agent → MCP → tool/API → database → business action.
Workflow Intelligence
Every agent. Every database. Every row.
Every AI request, fully visible.
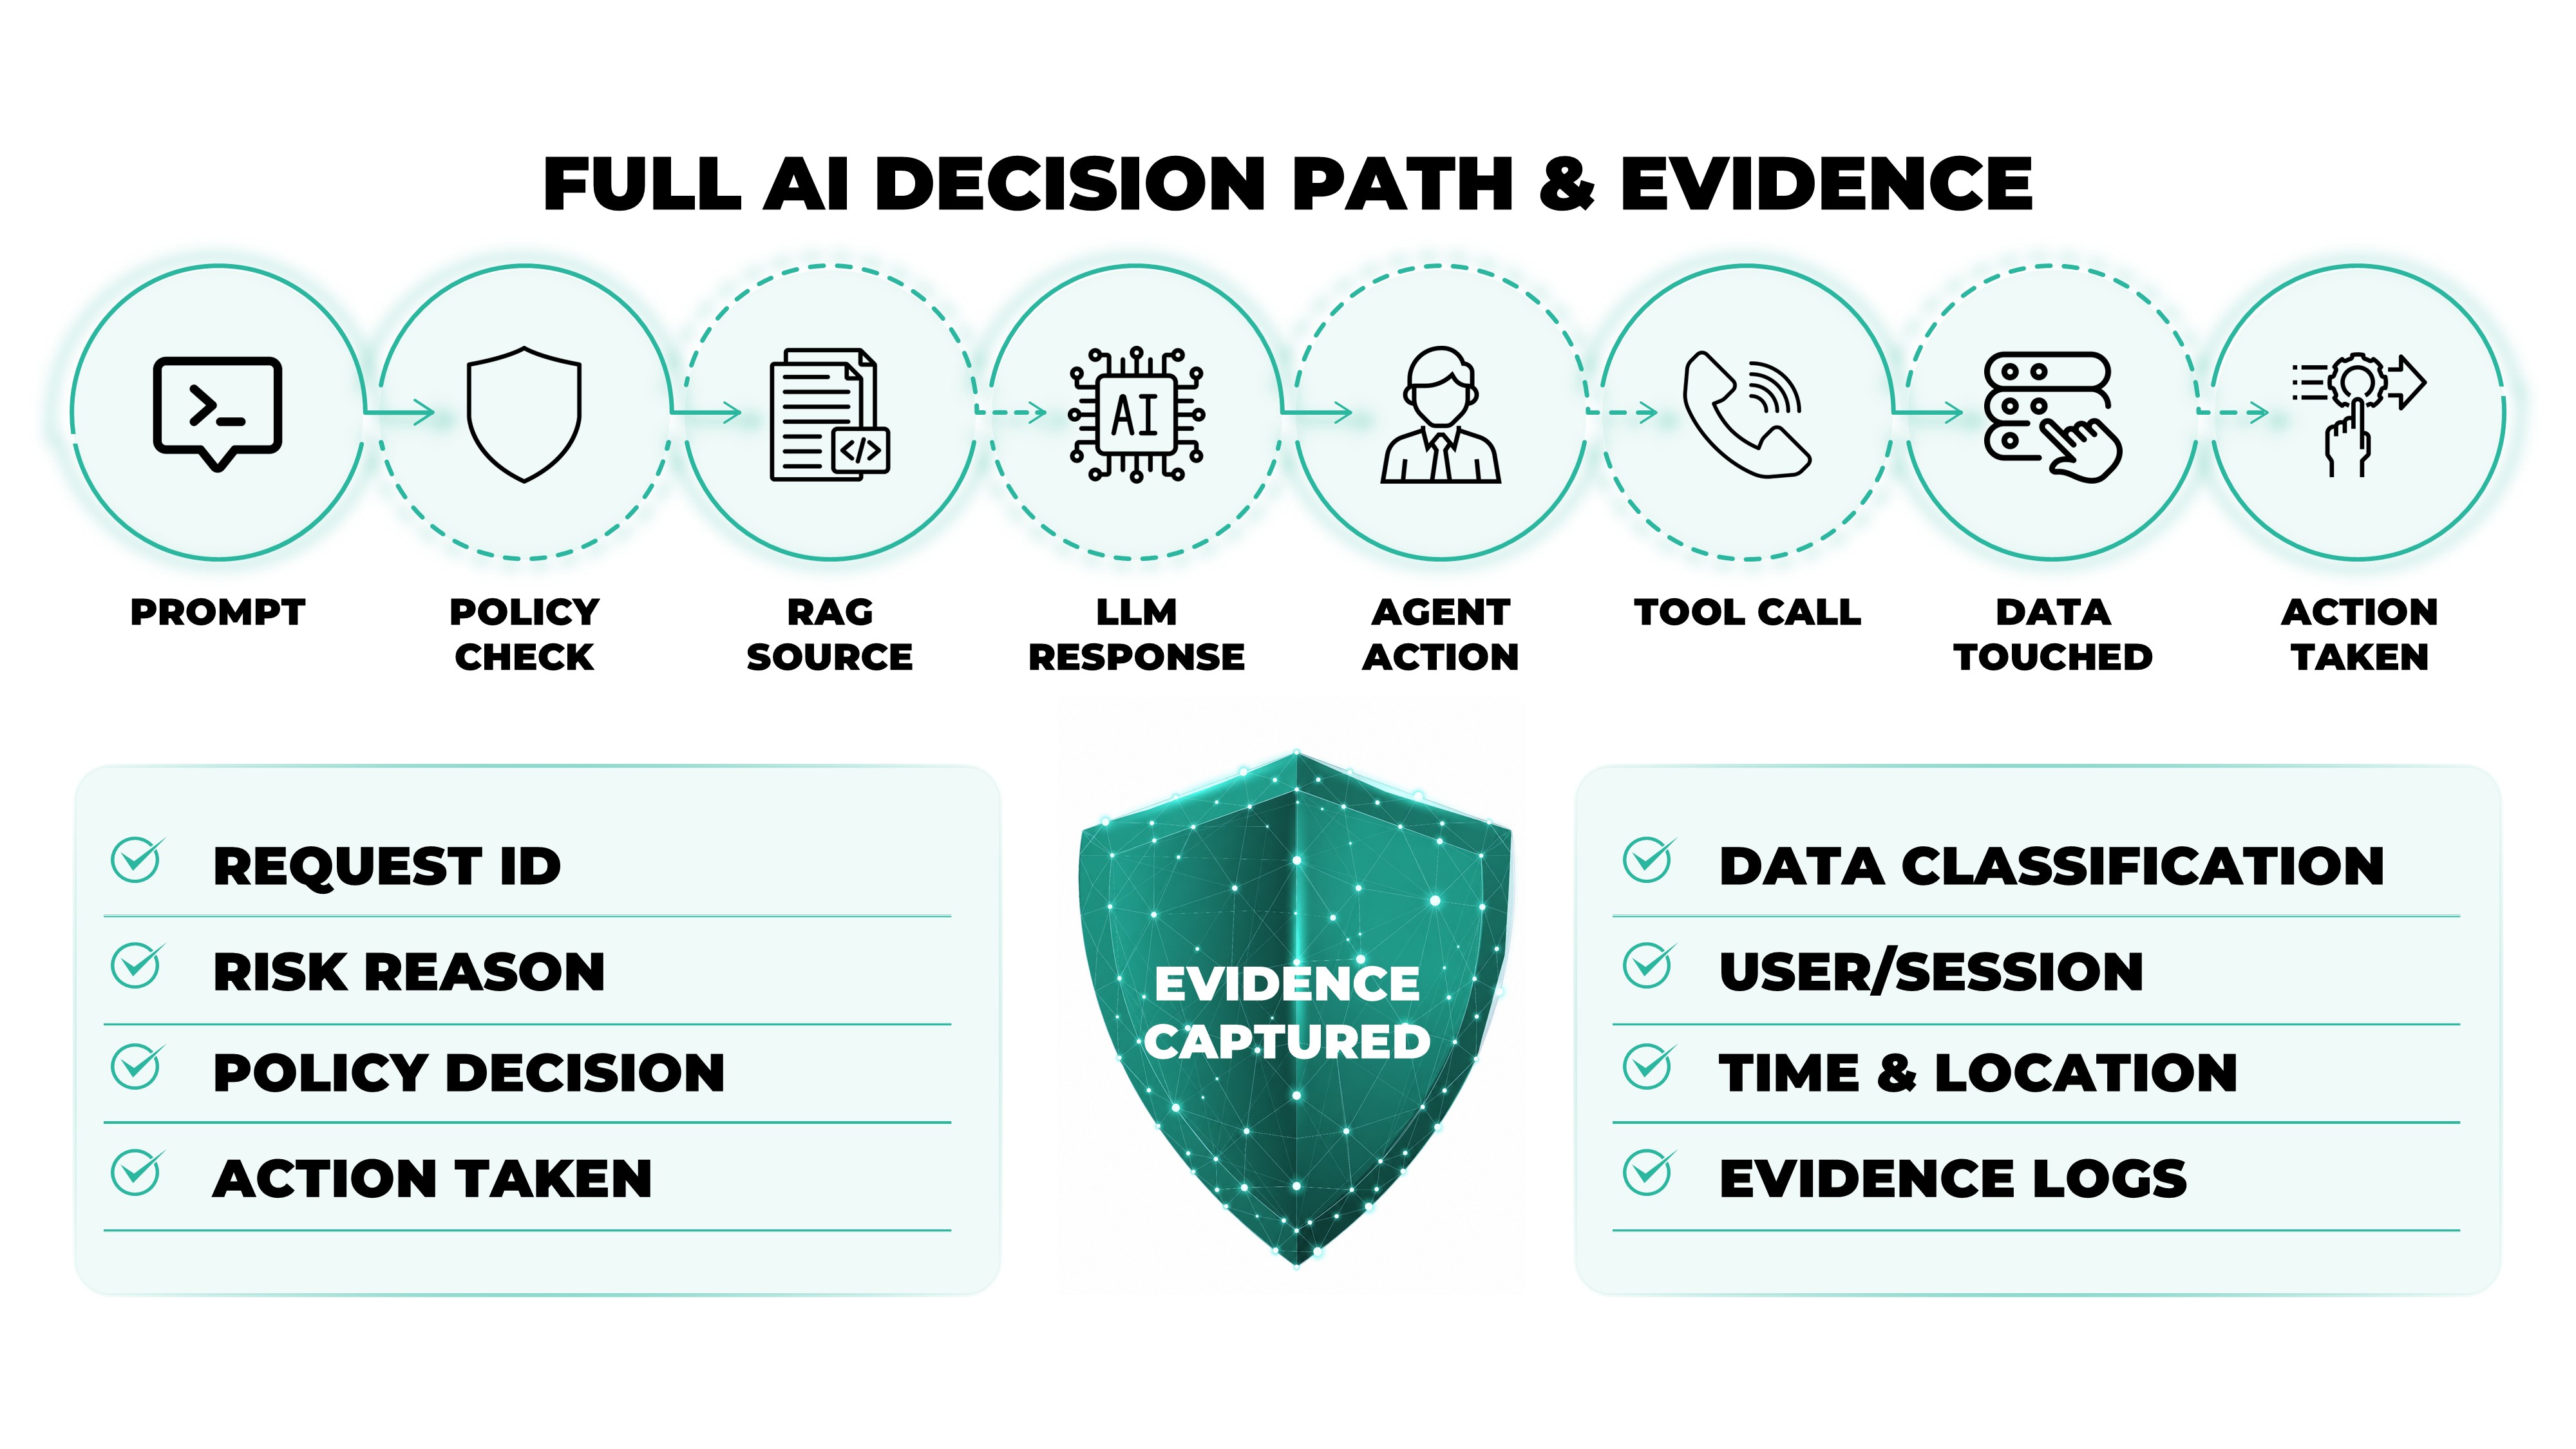
A log tells you an event happened. SAMI Workflow Intelligence shows what the AI actually accomplished by mapping the complete execution path in real time not just what went in and came out, but everything that happened in between.
Full Call Tree
The complete execution path for every request: entry → AI Firewall → Guardrails → Orchestrators → Sub-orchestrators → Parallel agent swarms → RAG pipelines → LLM refinement passes → Output Firewall → Response. Every node, every branch, every decision point.
When a breach investigation asks "what did our AI do?", this is the answer. Not a summary. The full trace.
Data Provenance per Prompt
Every database accessed, name, rows read, sensitivity classification (LOW/MEDIUM/HIGH), and whether it was within the declared session policy. Every RAG index searched, every chunk retrieved, similarity scores, what made it into model context. Every file read.
Your model said X. It said it because it retrieved Y from contracts_db (503 rows, HIGH sensitivity, out of scope). That's the data lineage EU AI Act requires.
Violation Propagation Tracing
Violations detected at the point of occurrence and tracked through every downstream step. When agent A07 accesses an out-of-scope database, that flag propagates through the merger, through two LLM refinement passes, and is caught again at the output firewall with the full propagation chain documented.
Without propagation tracing, you know something was flagged. With it, you know exactly how far it travelled before it was stopped and what it touched.
What SAMI Workflow Intelligence documents for every request
The system provides end-to-end AI workflow observability and governance by tracking source identity, AI firewall decisions, guardrail validations, orchestration plans, agent executions, database access, RAG pipeline activity, MCP/tool calls, LLM invocations, output firewall enforcement, workflow vitals, and exportable audit records.
For your CISO
"Show me every AI interaction that accessed sensitive data outside declared scope in the last 30 days." SAMI answers that in seconds, not weeks of log forensics.
For your regulator
EU AI Act Article 9 requires documented continuous risk management. Workflow Intelligence generates that documentation automatically, not a periodic report, a live audit trail for every single request.
For your legal team
"Our AI accessed contract data it shouldn't have. Here is the exact request ID, the exact agent, the exact rows, the exact timestamp, and the violation flag that was raised and escalated." That's a defense. "We don't know" is not.
THE EVIDENCE GAP
Policies are not enough if you cannot reconstruct what the AI actually did.
63%
of breached organizations in IBM's 2025 study lacked an AI governance policy or were still developing one.
34%
of organizations that had AI governance policies performed regular audits for unsanctioned AI.
Source: IBM Cost of a Data Breach Report 2025 / IBM Newsroom. Figures apply to the breach-study population described by IBM.
Workflow Intelligence: Complete AI Interaction Audit Trail
SAMI sees every step
of every AI interaction.
For every single AI request, SAMI's Workflow Intelligence maps the entire execution path from entry through firewall, guardrails, orchestrators, parallel agent swarms, RAG pipelines, and LLM refinement passes, to the output firewall and final response. Every agent, every database, every row count, every MCP tool call, every violation, visible, traceable, and documented.
When your regulator asks what your AI system did and under EU AI Act Article 9, they will, this is the record that answers it. When a data breach investigation asks "how did agent A07 pull 503 rows of contract data that was never in the declared session policy?", this is what shows you exactly how it happened, where it propagated, and what it touched on the way out.
↑ Click any checkpoint to see what SAMI captures in the audit trail
Most organizations can't answer the question: "What did your AI model do at 09:14 on Tuesday?" SAMI can. Every checkpoint in this flow produces a tamper-evident audit entry, who, what, which data, which decision, how long. That record is your EU AI Act compliance evidence, your insurer's proof of monitoring, and your legal defense if something goes wrong.
Prompt Source
Who sent this? From where? SAMI knows before the model does.
Every interaction starts with identity capture. Without it, you can't answer the first question a regulator or insurer asks: who initiated this? SAMI records the full source context before the prompt touches anything, so you always know.
Audit trail: source capture
User identityemployee@company.com · Entra ID verified
Source IP192.168.1.44 · Internal VPN
Timestamp2025-03-14 09:14:22 UTC
ApplicationCustomer support portal · v2.4.1
Session IDsess_a3f9b2c1 · 4 prior turns
Layer 01: AI Firewall
Reads intent, not just syntax.
4 directions. 5 hard decisions.
The AI Firewall inspects the prompt before the model sees it, but also inspects what the model returns, what the RAG pipeline retrieves, and what any agent tool call attempts. All 4 directions, simultaneously. Five hard outcomes: ALLOW · QUARANTINE · REDACT · TOKENIZE · BLOCK. No probability scores. No ambiguity.
When the Firewall fires QUARANTINE, three things happen at once: the content is held, a SOC incident is created in your SIEM, and the interaction is flagged in the audit trail. Your security team sees it. The regulator's evidence trail is updated. And the model never touched the threat.
Audit trail: AI Firewall decision
DirectionInbound prompt
Semantic scanPrompt injection intent detected, instruction override pattern
DecisionQUARANTINE held for SOC review
SOC incidentAI-INC-2025-0314-001 raised in SIEM
Response time38ms
Layer 02: Dynamic Guardrails (TrustGuard)
Policy-as-runtime. Session memory.
Auto-tightens when bypass is detected.
Guardrails check the prompt against your current policy configuration, hard allow/block/transform decisions, not probability scores. Session memory reviews the last 20+ turns for multi-step erosion patterns.
Here's what matters: a sophisticated attacker doesn't try one obvious injection. They probe across 10 or 20 messages, slowly shifting the conversation. By message 15, your static guardrail has no idea it's being manipulated. SAMI's session memory catches the pattern. When bypass is detected, guardrails auto-tighten and a SOC alert fires simultaneously, while the attack is still in progress, not after it succeeded.
Audit trail Guardrail decision
Policy versioncustomer-support-v3.2 · updated 2025-03-01
Session turns4 prior turns reviewed
Erosion patternNone detected single-turn prompt
Policy matchALLOW prompt within customer support scope
Guardrail statusStable, no auto-tighten triggered
Layer 03: Data Privacy & Tokenization
PII stripped before model contact.
The model never sees the sensitive data.
Before the prompt reaches the LLM, SAMI tokenizes PII, PHI, and proprietary data locally. The model processes tokens only it never sees a customer name, account number, or medical record. SAMI rehydrates real values in the output on the way back.
Why this matters: Samsung's 2023 ChatGPT leak engineers pasted source code and internal data into a public LLM happened because nothing stopped the data at the point of model contact. SAMI's tokenization means the model never sees the sensitive data in the first place. Supports GDPR Article 25 privacy-by-design by tokenizing sensitive data before model contact.
Audit trail: Tokenization
PII detectedCustomer name · Account number · Email address
ActionTokenized locally, TKN_7f2a, TKN_8c1d, TKN_3e9b
Sent to LLMTokens only, no PII in model context
RehydrationApplied on output, user sees real values
TelemetryZero-audit log local only
LLM: Language Model
The model sees only
what SAMI allows it to see.
By the time the prompt reaches the LLM, it has passed the AI Firewall, cleared guardrail policy, and had PII stripped and tokenized. The model processes the sanitized, tokenized request. SAMI continues to inspect the outbound response gets the same treatment on the way back out through L01 and L05.
Audit trail: LLM invocation
ModelGPT-4o · customer-support deployment
Input tokens342 (sanitized) · 0 PII in context
Prompt hashsha256:a3f9b2c1... (tamper-evident)
ResponseGenerated · passing to L01 outbound check
Layer 04: RAG Defender
Which folder. Which documents. What was retrieved.
Complete RAG provenance.
When the LLM invokes a RAG call, SAMI intercepts at both the query (before it hits the knowledge base) and the retrieval (before returned content reaches the model). Logs exactly which knowledge base, which folders, which documents, what was retrieved.
This matters for two reasons. First, RAG poisoning where an attacker plants malicious instructions inside documents your AI retrieves is stopped here before model contact. Second, you now have a complete data lineage record for every AI response: your model said X because it retrieved Y from folder Z. That's the provenance your legal team needs when an AI-generated response causes a problem.
Audit trail: RAG retrieval
KB queriedcustomer-support-kb · v2024-Q4
Folders accessedpolicies/ · products/pricing/
Docs retrieved3 documents · policy-v4.pdf, pricing-Q4.pdf, faq-returns.md
Poisoning scanClean, no injection patterns detected
DecisionALLOW content passed to model context
Layer 05: Agentic & MCP Security
Every tool call validated
before it executes.
When the LLM invokes an agent or MCP tool call, SAMI validates it against your approved policy scope before the action executes. The database is never queried. The email is never sent. The file is never written, unless policy says so.
Without this, your AI agent is executing actions on your behalf with no governance layer. It's the equivalent of giving a contractor building access with no supervision and no keycard log. Every tool invocation, every scope check, logged, so you know exactly what your agents did and when.
Audit trail: MCP tool call
Tool invokedcustomer-db.lookup(account_id)
Policy scopeRead · customer-support · approved
DecisionALLOW within approved scope
Data returnedAccount status · support tier · open tickets
Write attemptNone detected
Audit Trail Complete
Every step. Every decision.
Always ready for inspection.
SAMI generates a tamper-evident audit record for every AI interaction, from source identity to final response.
EU AI Act Article 9 requires documented lifecycle risk management for high-risk AI systems, not a one-time assessment, continuous proof. Cyber insurers are adding AI monitoring clauses to renewals. Courts are establishing the standard of care for AI negligence. This audit trail is what separates "we had controls in place" from "we had no idea what our AI was doing." One is a defense. The other is liability.
Complete interaction record
Interaction IDAI-INT-2025-031400142
Total latency312ms including all SAMI layers
Layers checkedL01 · L02 · L03 · L04 · L05: all PASS
EU AI ActArt.9 evidence record updated
ExportableJSON · PDF · SIEM event
Your AI environment is live.
SAMI is watching it.
Free external scan. Or book a proof of value, we deploy in your environment, show you everything we find, and produce the board and compliance report before we leave.
SAMI: AI Security Platform
You deployed AI.
Now it needs to be
secured end to end.
AI is no longer one model behind one app. It is a live workflow across prompts, responses, RAG pipelines, agents, MCP tool calls, sensitive data, and downstream actions. Every part of that workflow is an attack surface.
SAMI is the only platform built to protect all of it before launch, in production, and continuously as AI changes. One platform. Defense in depth. No gaps.
OWASP LLM Top 10
MITRE ATLAS
EU AI Act
NIST AI RMF
ISO 42001
Zero Trust
The state of AI security right now
92%
of organizations with AI guardrails have already leaked data. World Economic Forum, 2024
40%
of enterprises will demote or decommission AI agents because governance gaps are found after production incidents. Gartner, 2026
Article 9
EU AI Act requires continuous lifecycle risk evidence for high-risk AI systems. Enforcement is active. Penalties are material.
70%
of live MCP deployments showed exposed risk paths in SAMI testing.
Every feature. Every competitor.
One table.
Click to view SAMI AI Security comparisons
Why this is hard
AI deployment creates new compounding
security problems.
AI is not just another application. It is a new operating layer where prompts, data, models, agents, tools, and business decisions all interact in real time.
Traditional security tools were built to detect malicious code, malware, network anomalies, and suspicious API behavior. AI risk does not always look like that. A prompt injection looks like a normal request. A poisoned RAG document looks like trusted content. An agent hijack looks like an approved workflow. A data leak looks like a helpful answer.
That is why AI security requires more than point controls. Organizations need visibility, runtime protection, privacy enforcement, policy control, vulnerability management, and full observability across every AI system.
The platform at a glance
10 layers of protection.
Every one solves something the others cannot.
Each layer below links to its own detail page. This is the summary one line per layer, what it does, why it exists.
Click to see 10 Layers of protectionWhat each team gets
One platform.
Answers for every team that touches AI.
Security & SOC
Turn AI attacks into incidents your SOC can act on.
✓300+ AI attack vectors covered out of the box, with ability for further customization
✓Structured AI incidents in your existing SIEM queue
✓Full call-tree evidence for every incident, including privacy assessment for data accessed
✓Policy tightens automatically when bypass is detected
✓Allow, block, redact, tokenize, alert, or escalate actions
✓No code changes to your existing AI stack
Risk & Compliance
Keep AI operating inside your policies, regulations, and control framework.
✓Map AI activity to corporate policies, privacy rules, and compliance frameworks
✓Enforce approved data privacy rules at runtime
✓Use preset policy packs or customize rules to match your organization
✓Track every prompt, response, tool call, policy decision, and exception
✓Generate audit-ready evidence showing what happened, what was allowed, what was blocked, and why
AI & Engineering
Ship AI faster without creating security debt.
✓Deploy controls without slowing AI teams
✓Test prompts, responses, agents, RAG, MCP, and tools before production
✓Enforce approved policies from development into runtime
✓Detect risky behavior before it becomes an incident
✓Keep controls aligned as models, data, tools, and workflows change
AI Vulnerability Management
Prioritize AI risk by business impact and fix what matters first.
✓Check AI systems exposed to the internet, LLM, RAG, MCP etc. for vulnerabilities continously both before and after deployment.
✓Business impact assessment for every AI finding
✓Remediation modeling to show which fixes reduce the most risk
✓Remediation orchestration across owners, teams, and workflows
✓Continuous gap assessment against policies and compliance frameworks
✓Evidence-ready reporting for audits, reviews, and leadership
From AI guardrails to
AI control evidence
Guardrails can help decide whether an interaction should continue. But enterprise AI security needs more: visibility into every workflow, control over every agent action, validation of every exposure, business impact for every risk, and evidence for every remediation.
SAMI combines runtime AI security with CTEM for AI so security, AI, risk, and compliance teams can protect AI in production and prove it.
Deployment modes
SaaS or on-premises.
Same features. Your choice.
Most AI security tools require cloud connectivity. SAMI works fully on-premises with zero telemetry, full GDPR compliance by architecture, and air-gap available from day one.
SaaS
Cloud-hosted · Managed · Deploy in hours
SAMI hosted and managed by Autnhive. Automatic updates, zero infrastructure overhead. Connect your AI environment in hours.
On-Premises
Your infrastructure · Full data sovereignty · GDPR by architecture
SAMI runs entirely in your environment. No data leaves your perimeter. Zero vendor telemetry. Air-gap available. GDPR Article 25 privacy-by-design. Full feature parity with SaaS.
The only question that matters
The question is not
whether to secure your AI.
It is whether you discover
the need before or after an incident.
Every organization in the incident list above had time to act before it happened. The vulnerability existed. The attack surface was there. The question was simply whether anyone looked. SAMI's free AI Security Assessment looks. It shows you exactly what is exploitable in your AI environment right now the same things an attacker would find.
SAMI Security Engine
Protect every AI interaction.
From prompt to business action.
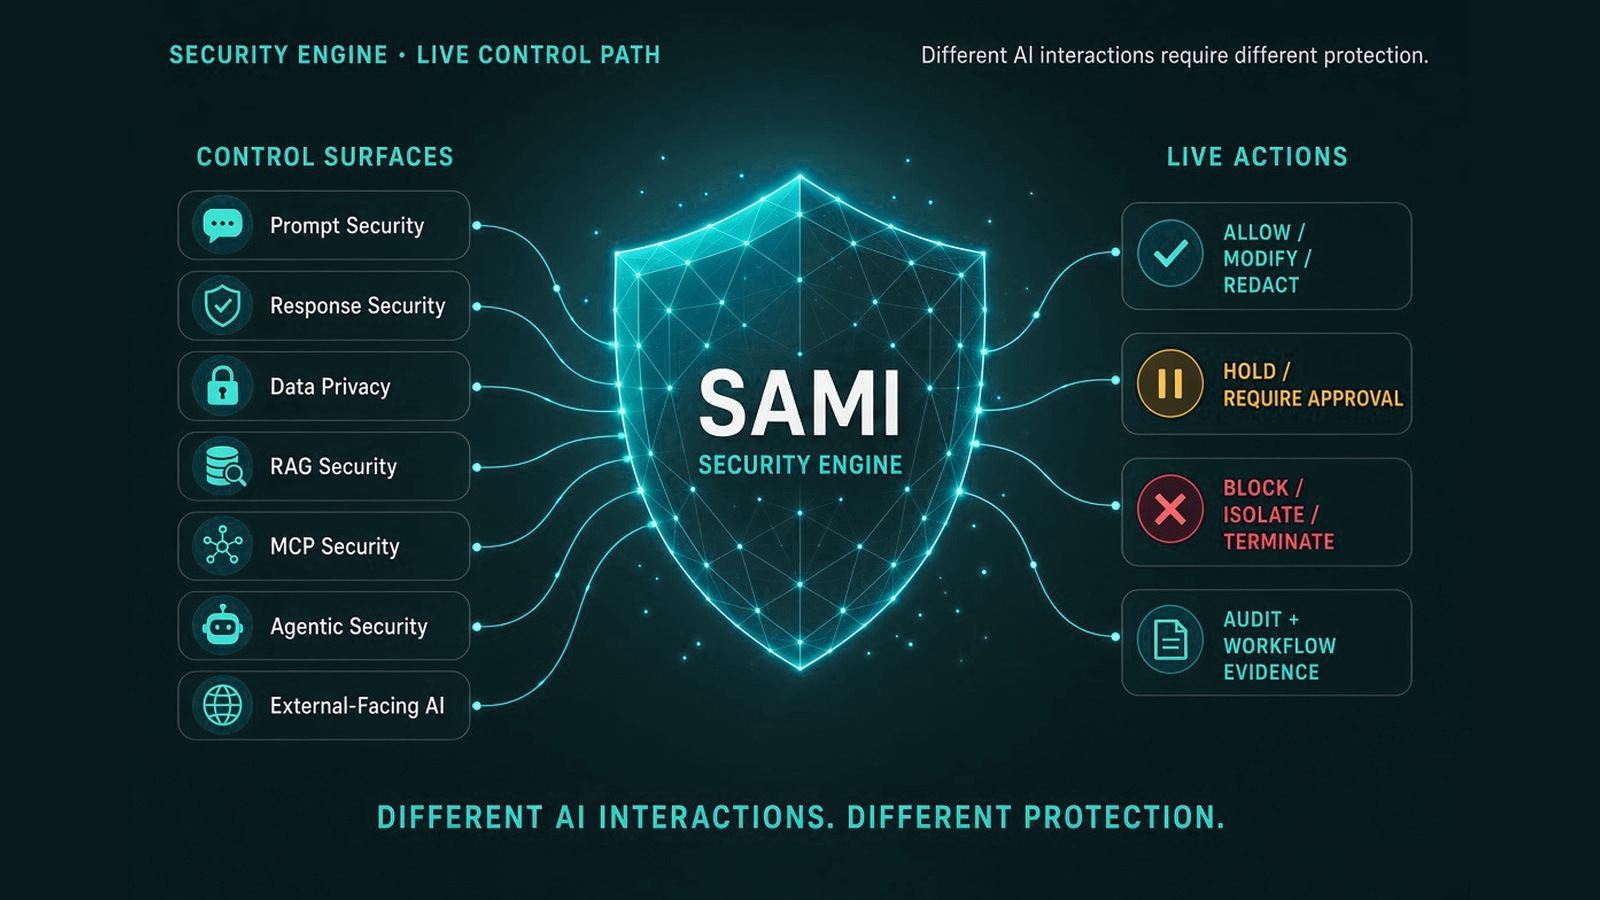
The SAMI Security Engine protects the complete AI execution path not just the prompt. It can autonomously attach the right protection across prompts, responses, sensitive data, RAG, MCP and agents, continuously track agent behavior, stop unsafe or rogue actions before execution, defend enterprise systems from external AI agents, and continuously test LLM, MCP and agent exposure.
ALLOWMODIFYREDACTHOLDREQUIRE APPROVALBLOCKTERMINATE AGENT
Real-time control
Built for live AI. Proven for real-time control.
SAMI stays inline while decisions are made across prompts, responses, data, MCP and agent actions.
Prompts
Responses
Data
MCP
Agents
99.8%
Security decision accuracy in Autnhive validated testing
ms-level
Inline security decisions designed for live AI traffic
Continuous
Agent behavior tracking, drift detection and reassessment
Pre-execution
MCP tool and agent action control before the business action occurs
Inline
Prompt, response, data, MCP and agent decisions stay in the live control path
Adaptive
Security reassesses as AI workflows, policy and permissions change
* Performance figures shown are Autnhive validation results. Accuracy and latency vary by policy set, workload, model, deployment mode and inspection path; publish the supporting methodology with production benchmarks.
97%
of organizations in IBM's 2025 breach study that reported an AI-related security incident lacked proper AI access controls.
60%
of AI-related security incidents in that study resulted in compromised data.
31%
resulted in operational disruption.
Source: IBM Cost of a Data Breach Report 2025 / IBM Newsroom. Population: 600 organizations that experienced data breaches between March 2024 and February 2025.
01 · INPUT
Prompt Security
Inspect what enters the AI before model contact. Detect manipulation, jailbreaks, unsafe instructions, prohibited requests and policy violations.
PROMPT INJECTION · JAILBREAKS · POLICY · SENSITIVE INPUT
02 · OUTPUT
Response Security
Inspect what the AI returns before it reaches the user or downstream system. Redact, modify, hold or block unsafe, sensitive or policy-violating output.
OUTPUT CONTROL · DATA LEAKAGE · POLICY · DOWNSTREAM SAFETY
03 · DATA
Data Privacy
Detect and protect sensitive information used by AI. Apply redaction, tokenization, masking or blocking based on your organization's privacy rules.
PII · PHI · CREDENTIALS · IP · REGULATED DATA
04 · RETRIEVAL
RAG Security
Protect both sides of RAG: screen knowledge at ingestion, then inspect the query, retrieved chunks and model context at runtime. Stop poisoning and preserve source provenance.
INGESTION GATE · QUERY-TIME GATE · POISONING · PROVENANCE · DATA ACCESS
05 · TOOLS
MCP Security
Discover MCP servers and tools, validate trust and permissions, then sit inline with the tool call so risky actions can be allowed, held for approval or blocked before execution.
MCP DISCOVERY · SERVER TRUST · TOOL SCOPE · PRE-EXECUTION · APPROVALS
06 · ACTIONS
Agentic Security
Autonomously discover agents, attach security, track behavior and detect drift, compromise or rogue action. Block the action, isolate the agent or terminate it when policy requires.
AUTO-DISCOVERY · ATTACH · BEHAVIOR · DRIFT · ROGUE ACTION · BLOCK · TERMINATE
07 · TWO-WAY DEFENSE
External AI Defense
Protect public-facing AI from attack and protect enterprise applications, APIs, MCP endpoints, tools and systems from external AI agents attempting to interact or take action.
EXTERNAL AGENTS · INBOUND AI SENSOR · AI APPS · API / MCP · ATTACK SIMULATION · VJ
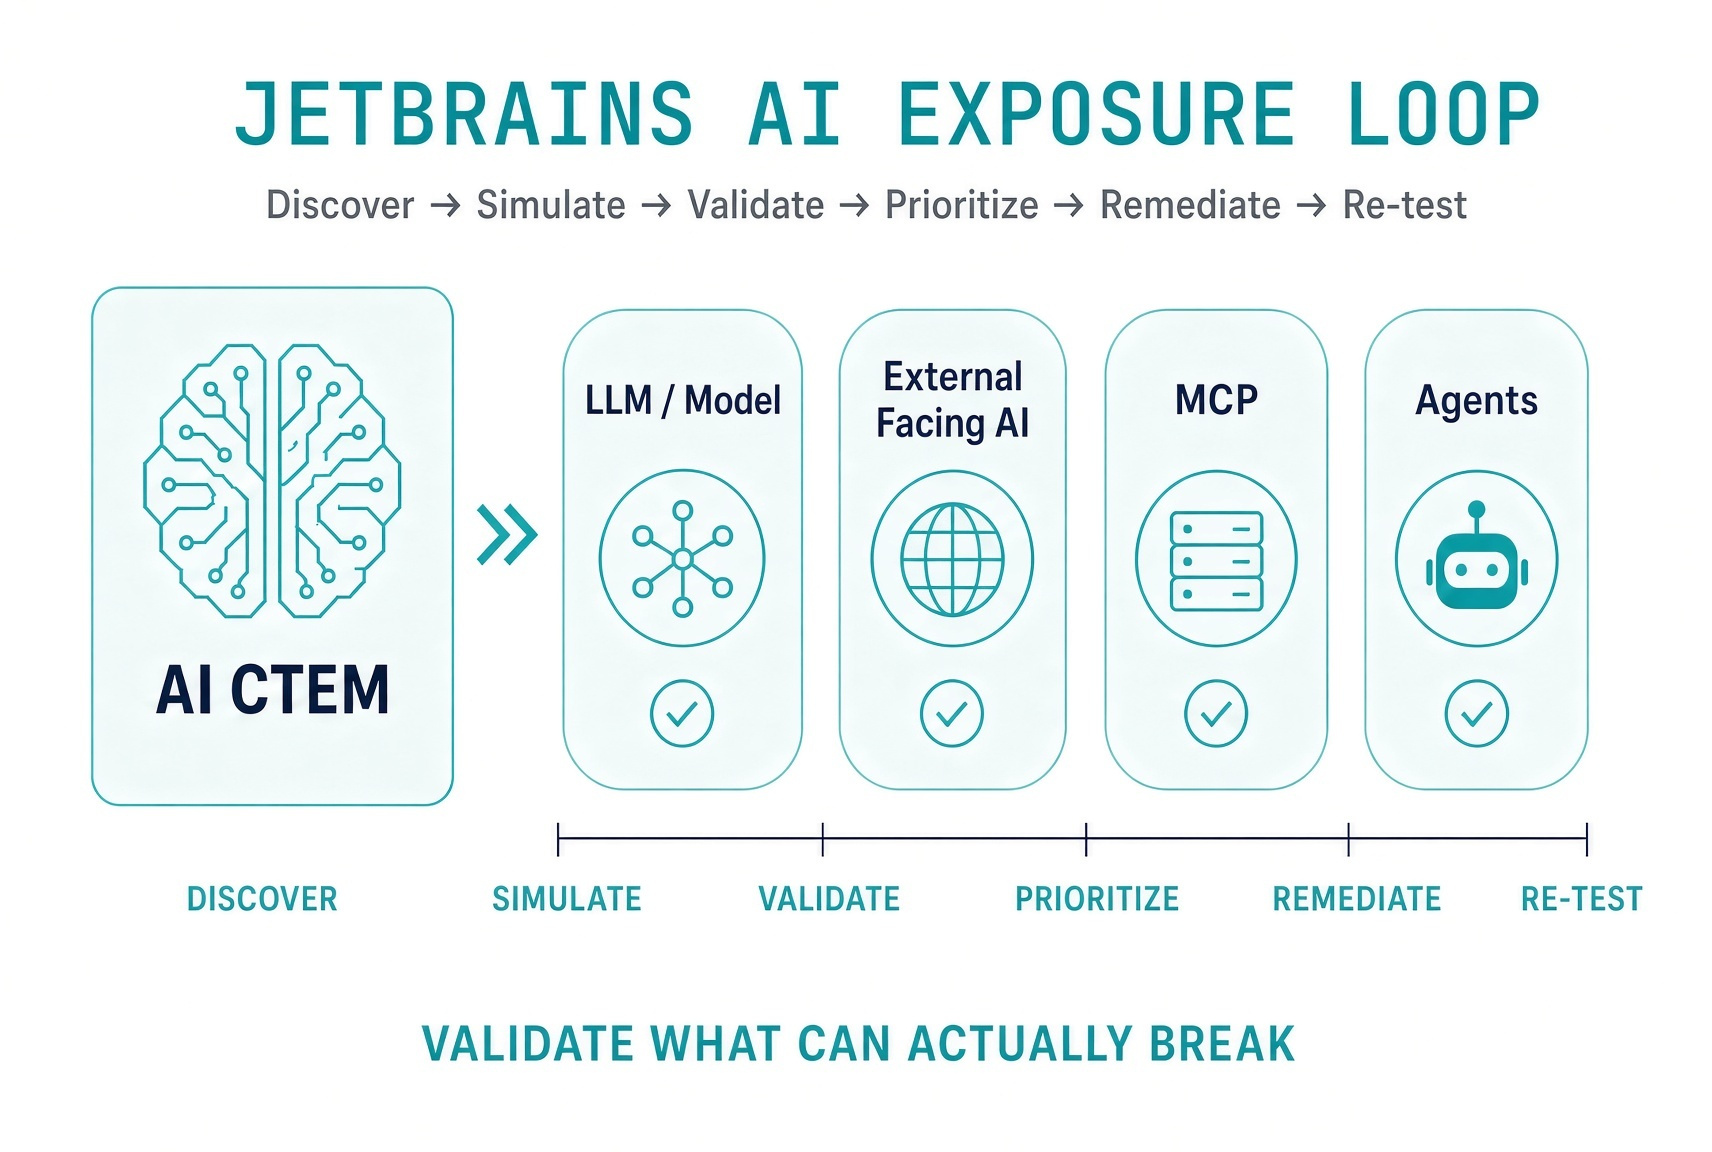
CONTINUOUS
AI CTEM
Continuously identify, test and prioritize exposure across LLMs, MCP and agents then re-test as the environment changes.
DISCOVER · SIMULATE · VALIDATE · PRIORITIZE · REMEDIATE · RE-TEST
ONE SECURITY ENGINE · MULTIPLE AI CONTROL SURFACES
SAMI selects the appropriate security control based on the AI interaction and context. A prompt does not need the same protection as an MCP tool call, an agent action or an externally exposed AI application.
Security Engine
Guardrails matter. They are not enough on their own.
Security has to follow the full AI path across prompt, response, data, RAG, MCP, agents, external AI and continuous testing.
One engine. Every AI control surface.
Prompt SecurityStop injection, jailbreaks and unsafe instructions before they reach the model.
Response SecurityInspect output for unsafe, manipulative or policy-breaking responses.
Data PrivacyRedact or transform sensitive data before it reaches the model or leaves the enterprise boundary.
RAG SecurityProtect ingestion and retrieval so poisoned or over-broad context does not become trusted AI input.
MCP SecuritySit in the tool call and validate what the AI is trying to execute before it touches a system.
Agentic SecurityTrack agents, detect drift or rogue behavior, and hold, block or kill unsafe autonomous action.
External AI DefenseProtect the enterprise from inbound AI and third-party agent interactions.
AI CTEMContinuously test LLM, RAG, MCP and agent exposure so new attack paths are found early.
Why it matters now
AI appears faster than manual integration cycles.By the time a team connects one point solution, new AI surfaces may already be in use elsewhere.
Different AI paths create different security needs.RAG, MCP and autonomous agents introduce attack and action paths a prompt guardrail alone cannot cover.
The enterprise must also be protected from AI.The problem is not only someone attacking the AI. It is also the AI taking an unsafe action against the business.
Protect both directions
Protect AI from attack.
Protect the enterprise from AI.
AI security has two directions. Attackers can manipulate the AI. The AI can also create enterprise risk through unsafe output, excessive permissions, compromised context or an unintended action. SAMI creates a decision point between AI intent and business action.
Attack → SAMI → AI
Prompt injection · jailbreaks · data extraction · RAG poisoning · MCP abuse · agent hijacking · workflow manipulation.
AI → SAMI → Enterprise
Unsafe responses · sensitive-data exposure · excessive permissions · wrong tool calls · unauthorized agent actions · compromised workflows.
External AI Agent → SAMI → Enterprise
Identify and govern external autonomous systems interacting with applications, APIs, MCP endpoints, tools, databases and business services.
Agentic Security · Autonomous Control
Find the agent. Track it. Stop it before it becomes the incident.
Agents are different from chatbots: they can call tools, change records, move data and trigger business processes. SAMI is designed to autonomously discover agents, attach the Agentic Security module, establish context for the agent's normal scope, and continuously evaluate what it is trying to do.
01
Autonomous discovery + attachment. When an agent is identified, SAMI can attach the appropriate security control without waiting for a new application integration.
02
Behavior and drift monitoring. Track tools, permissions, data, destinations and actions over time to identify behavior that moves outside the expected operating scope.
03
Pre-action enforcement. Evaluate the requested action before it reaches the target application, API, MCP tool, database or business system.
04
Stop the agent. SAMI can block the action, isolate the agent, revoke/disable the path or terminate the agent when policy and the connected control plane permit it.
AUTO-DISCOVERATTACHTRACKDRIFTBLOCKTERMINATE
AGENT LIFECYCLE CONTROLLIVE
AGENT
DISCOVERED
DISCOVERED
→
SAMI
ATTACHES
ATTACHES
→
BASELINE
CONTEXT
CONTEXT
→
TRACK
BEHAVIOR
BEHAVIOR
Every material action is evaluated before execution
INTENT
→
PERMISSION
→
TOOL / DATA
→
DRIFT / ROGUE?
ALLOW
MODIFY
HOLD / APPROVE
BLOCK ACTION
ISOLATE
TERMINATE AGENT
43–46%
Agent API call CAGRAgent traffic is scaling far faster than human-initiated API traffic, which the same report puts at 3.1%.
Source: Kong, The State of AI Governance (2026). The report frames agents as an increasingly urgent governance surface.
RAG SECURITY · TWO INDEPENDENT CHECKPOINTSPROTECTED
CHECKPOINT 01 · INGESTION
Protect what enters the knowledge base.
Screen documents, feeds and content for malicious instructions, untrusted sources, policy violations and poisoning before they become something the AI can retrieve.
CHECKPOINT 02 · RETRIEVAL
Protect what reaches model context.
Inspect the query, retrieved chunks and returned context at runtime. Enforce data scope, detect poisoning and record exactly which sources influenced the answer.
SOURCE
→
SAMI INGESTION GATE
→
RAG / VECTOR DB
QUERY
→
SAMI RETRIEVAL GATE
→
MODEL CONTEXT
RAG Security · Dual-Layer Protection
If an attacker poisons what your AI trusts, prompt security is already too late.
SAMI protects the knowledge path itself. It can screen content before ingestion and independently inspect retrieval before returned content enters model context. That gives the organization two chances to stop poisoned or unauthorized knowledge from shaping the AI's decision.
01
RAG poisoning defense. Detect malicious instructions or manipulated content embedded inside trusted-looking documents.
02
Retrieval authorization. Govern what knowledge the user, model or agent is permitted to retrieve for the specific task.
03
Source provenance. Preserve which knowledge base, folder, document and chunk influenced the AI response for workflow intelligence and evidence.
MCP Security · Pre-Execution Control
Do not just inventory MCP. Sit in the tool call.
MCP gives AI access to tools and business systems. SAMI is designed to discover MCP servers and tools, evaluate their trust and policy scope, and intercept the requested tool call before execution. The decision is made before the business system changes not after the incident lands in a log.
01
Discover MCP servers and tools. Build a live inventory of MCP relationships, available actions and agent dependencies.
02
Trust + permission validation. Check server trust, tool entitlement, requested scope, identity, data and workflow context.
03
Pre-execution action gate. Allow safe reads, require approval for high-risk changes and block unauthorized or dangerous tool calls.
MCP TOOL-CALL CONTROLPRE-EXECUTION
AGENT
→
MCP SERVER
→
SAMI MCP JUDGE
→
TOOL / SYSTEM
Example policy decisions
READ RECORD · ALLOW
MODIFY PAYMENT · APPROVAL
EXPORT DATABASE · BLOCK
UNKNOWN SERVER · HOLD
OUT-OF-SCOPE TOOL · BLOCK
AUDIT · RECORD
PROMPT + RESPONSE + ADAPTIVE GUARDRAILSTWO-WAY
USER / APP
→
PROMPT SECURITY
→
MODEL
→
RESPONSE SECURITY
→
USER / SYSTEM
Adaptive policy context
IDENTITY
DATA
MODEL
SESSION
RISK
WORKFLOW
Prompt + Response Security · Dynamic Guardrails
Guardrails that understand context, session and action.
SAMI inspects the interaction in both directions. Prompt Security protects what enters the AI; Response Security controls what leaves it. Dynamic guardrails can use identity, data sensitivity, model, session history, workflow and action context to make the runtime decision.
01
Prompt protection. Detect prompt injection, jailbreaks, unsafe instructions, sensitive data and policy violations before model contact.
02
Response protection. Redact or block sensitive, unsafe, manipulated or policy-violating responses before they reach the user or downstream application.
03
Session-aware enforcement. Detect multi-step behavior and cumulative policy erosion that can be invisible when each message is evaluated alone.
Performance: Autnhive reports approximately 99.8% security decision accuracy in validated testing with millisecond-level inline enforcement. Production latency depends on the inspection path and deployment mode.
External AI Defense · Inbound AI Sensor
Your agents are not the only agents you need to control.
External AI agents and autonomous systems can interact with websites, applications, APIs, MCP endpoints, tools and business systems. The Inbound AI Sensor identifies AI-originated interaction, builds context around what the external agent is attempting to do, and routes the interaction through SAMI before the protected resource.
01
Detect incoming AI behavior. Identify autonomous or AI-driven interaction at the enterprise edge.
02
Understand requested access and action. Determine the application, API, data, MCP tool or business action being requested.
03
Enforce before access. Allow, restrict, hold, require approval or block the interaction before it reaches the enterprise system.
You do not have to deploy AI to have an AI security problem.
INBOUND AI CONTROL PATHEDGE
EXTERNAL AI AGENT
AUTONOMOUS SYSTEM
AI API CLIENT
SAMIINBOUND AI SENSOR + SECURITY ENGINE
APPLICATIONS / APIs
MCP / TOOLS / DATA
BUSINESS SYSTEMS
ALLOW
RESTRICT
HOLD / APPROVAL
BLOCK
AUDIT
BEHAVIOR HISTORY
Continuous AI Exposure Management
CTEM built for LLMs, MCP and agents.
Runtime protection answers “should this interaction be allowed?” AI CTEM answers “where are we exposed, can the weakness actually be exploited, what is the business impact and what should we fix first?”
LLM CTEM
Continuously test the model layer.
- Discover models and externally reachable AI services
- Validate prompt, response and data-exposure paths
- Simulate attacks and verify exploitability
- Prioritize weaknesses by context and business impact
MCP CTEM
Test the tool and trust layer.
- Inventory MCP servers, tools and trust relationships
- Find overexposed or risky tool paths
- Test authorization and misuse scenarios
- Validate whether an agent can reach an unintended action
AGENT CTEM
Test what autonomous AI can reach.
- Map agent permissions, tools, data and downstream systems
- Simulate unsafe or unintended action chains
- Assess potential blast radius and business consequence
- Re-test when permissions, tools or workflows change
External-facing AI gets both runtime protection and continuous testing.
Explore AI CTEM →Vulnerability Judge and attack simulation help validate how the AI application can be attacked from the outside; the Security Engine protects the live interaction.
Dynamic runtime policy
Guardrails are one part of the Security Engine not the whole story.
SAMI uses dynamic guardrails across prompts and responses, but guardrails are only one control surface. The same runtime policy can extend into RAG retrieval, MCP tool calls, agent actions, data privacy and external AI interactions so the decision follows the AI workflow instead of stopping at the chat window.
Why SAMI is different
Detection sees the event. Policy defines the boundary.
SAMI enforces the outcome.
SAMI combines runtime policy with context across prompts, responses, data, RAG, MCP and agents. The goal is not another alert or score; it is a traceable decision that can be enforced in the interaction.
Policy-as-runtime engine ★ UNIQUE
Hard allow/block/transform on every prompt, response, and tool call. Not a score. Not a flag. A decision. Auditable. Traceable. Enforceable by design. No developer required to update policy.
Autonomous tightening + simultaneous SOC alert ★ UNIQUE
When bypass is detected, policy tightens AND a SOC alert fires at the same moment not sequentially. Simultaneously. NeMo, LlamaGuard, Azure Content Safety: none can do this. SAMI is stronger before the attacker can try again.
Session-level pattern analysis ★ UNIQUE
Multi-step erosion detected across the full conversation. 20 individually benign messages that collectively cross the policy boundary caught before breach. Static guardrails evaluate per-message and miss this entirely.
Policy bundle lifecycle ★ UNIQUE
Draft → validated → approved → published. Model updates and policy updates are fully decoupled. Ship new model versions without touching guardrail code. Rollback in seconds.
Multi-tenant policy isolation
Each team or customer runs isolated policy bundles on shared infrastructure. No code forks. No policy bleed between tenants. Department-specific AI boundaries enforced without separate deployments.
Dual approval with separation of duties
High-risk overrides require a second approver. Self-approval blocked by policy. Exception governance built into the product not bolted on as a process nobody follows.
Audit-grade decision telemetry
Every runtime decision logged with request ID, component-level decisions, reason metadata, and tenant context. When your regulator asks what your AI did and under EU AI Act Article 9, they will, this is the record that answers it. Mean-time-to-investigate: minutes, not hours.
Continuous Gap Assessment
AI security coverage changes as your AI changes.
SAMI continuously finds the control gaps and helps close them.
Models change. RAG sources change. MCP tools appear. Agent permissions expand. Policies and attack techniques change. SAMI continuously reassesses the live AI stack so security coverage can move with the environment instead of becoming stale.
1
Audit current AI controls
SAMI evaluates the current controls across prompts, responses, data, RAG, MCP, agents and exposure paths against the live AI stack and threat context.
2
Recommend what's missing
A specific, prioritized list with the attack each missing control closes and the financial exposure without it. Not a generic checklist.
3
Auto-implement on approval
Your team reviews and approves. SAMI implements automatically no developer work, no model redeployment, no downtime. Policy-as-runtime updates instantly.
4
Self-tighten continuously
Guardrails update with live attack patterns, new threat intelligence, and policy changes. When bypass is detected, SAMI auto-tightens and fires a SOC alert simultaneously. No quarterly reviews.
WHY THIS MATTERS
92% of GenAI users with employer AI data guidelines still leaked company data. Your AI stack has changed since you wrote your guardrails. New attack techniques have been published. New models have been deployed. New compliance obligations have come into effect. Your guardrails don't know any of this, unless SAMI tells them.
The question is not whether you deployed AI security once. It is whether the controls still match how your AI operates today.
SOC & SIEM connection
Your SOC can see a port scan.
It cannot see a prompt injection, unless you give it SAMI.
Most SIEMs see API traffic. They cannot tell you whether the prompt was malicious, whether the response violated policy, or whether a session slowly eroded the AI's guardrails over forty turns. To your security team, AI attacks look exactly like normal user activity.
SAMI creates structured AI security events and sends them directly into your SIEM or SOC workflow. AI incidents are no longer invisible, they land in the same queue your team already works from, with no new workflow and no retraining.
Some AI incident record includes
Request ID
User & session context
Risk classification
Rule triggered
Policy decision
Data type detected
RAG source involved
Agent / tool involved
Action taken
Reason code
Evidence package
Recommended next step
Your SOC sees what happened. Compliance sees which rule applied. Privacy sees what data was protected. Audit has the evidence. Leadership sees that AI risk was controlled.
What changes
The same AI assistant.
Two very different outcomes.
Without SAMI
🔴User bypasses the guardrail, it only blocks the obvious phrasing. Subtle reframes and role-play get through.
🔴Employee pastes customer records into the prompt. The AI processes real PII. Nobody sees it.
🔴A conversation walks the AI outside policy over twenty messages. No session memory. No catch.
🔴Model updated. Guardrails not recalibrated. Behavior that was safe on v1 is now unsafe on v2 silently.
🔴New compliance obligation published. Gap exists for weeks until the next manual audit catches it.
🔴Compliance requires human review before the AI responds. AI answers anyway. The rule was never enforced at runtime.
🔴SOC sees normal traffic. Audit has no evidence. The business doesn't know what its AI did today.
With SAMI
✅Intent evaluated, not just phrasing. Reframes, role-play, and token smuggling caught before the model sees them.
✅Sensitive data tokenized before model contact. The AI processes tokens, not real values. PII never exposed.
✅Session memory holds 20+ turns. Slow erosion caught at message five, not after the breach at message twenty.
✅Drift detected on model update. ARE recalibrates guardrails automatically on approval. No gap between versions.
✅New compliance obligation detected. ARE runs gap analysis across all AI systems. Affected layers notified immediately.
✅Compliance rule enforced at runtime. Human review triggered before the AI responds. The rule runs, it doesn't just exist.
✅Every event creates a structured SOC incident. Security sees it live. Audit has the evidence trail. Leadership has proof.
AI productivity should not require data exposure.
Your teams want to use AI to move faster.
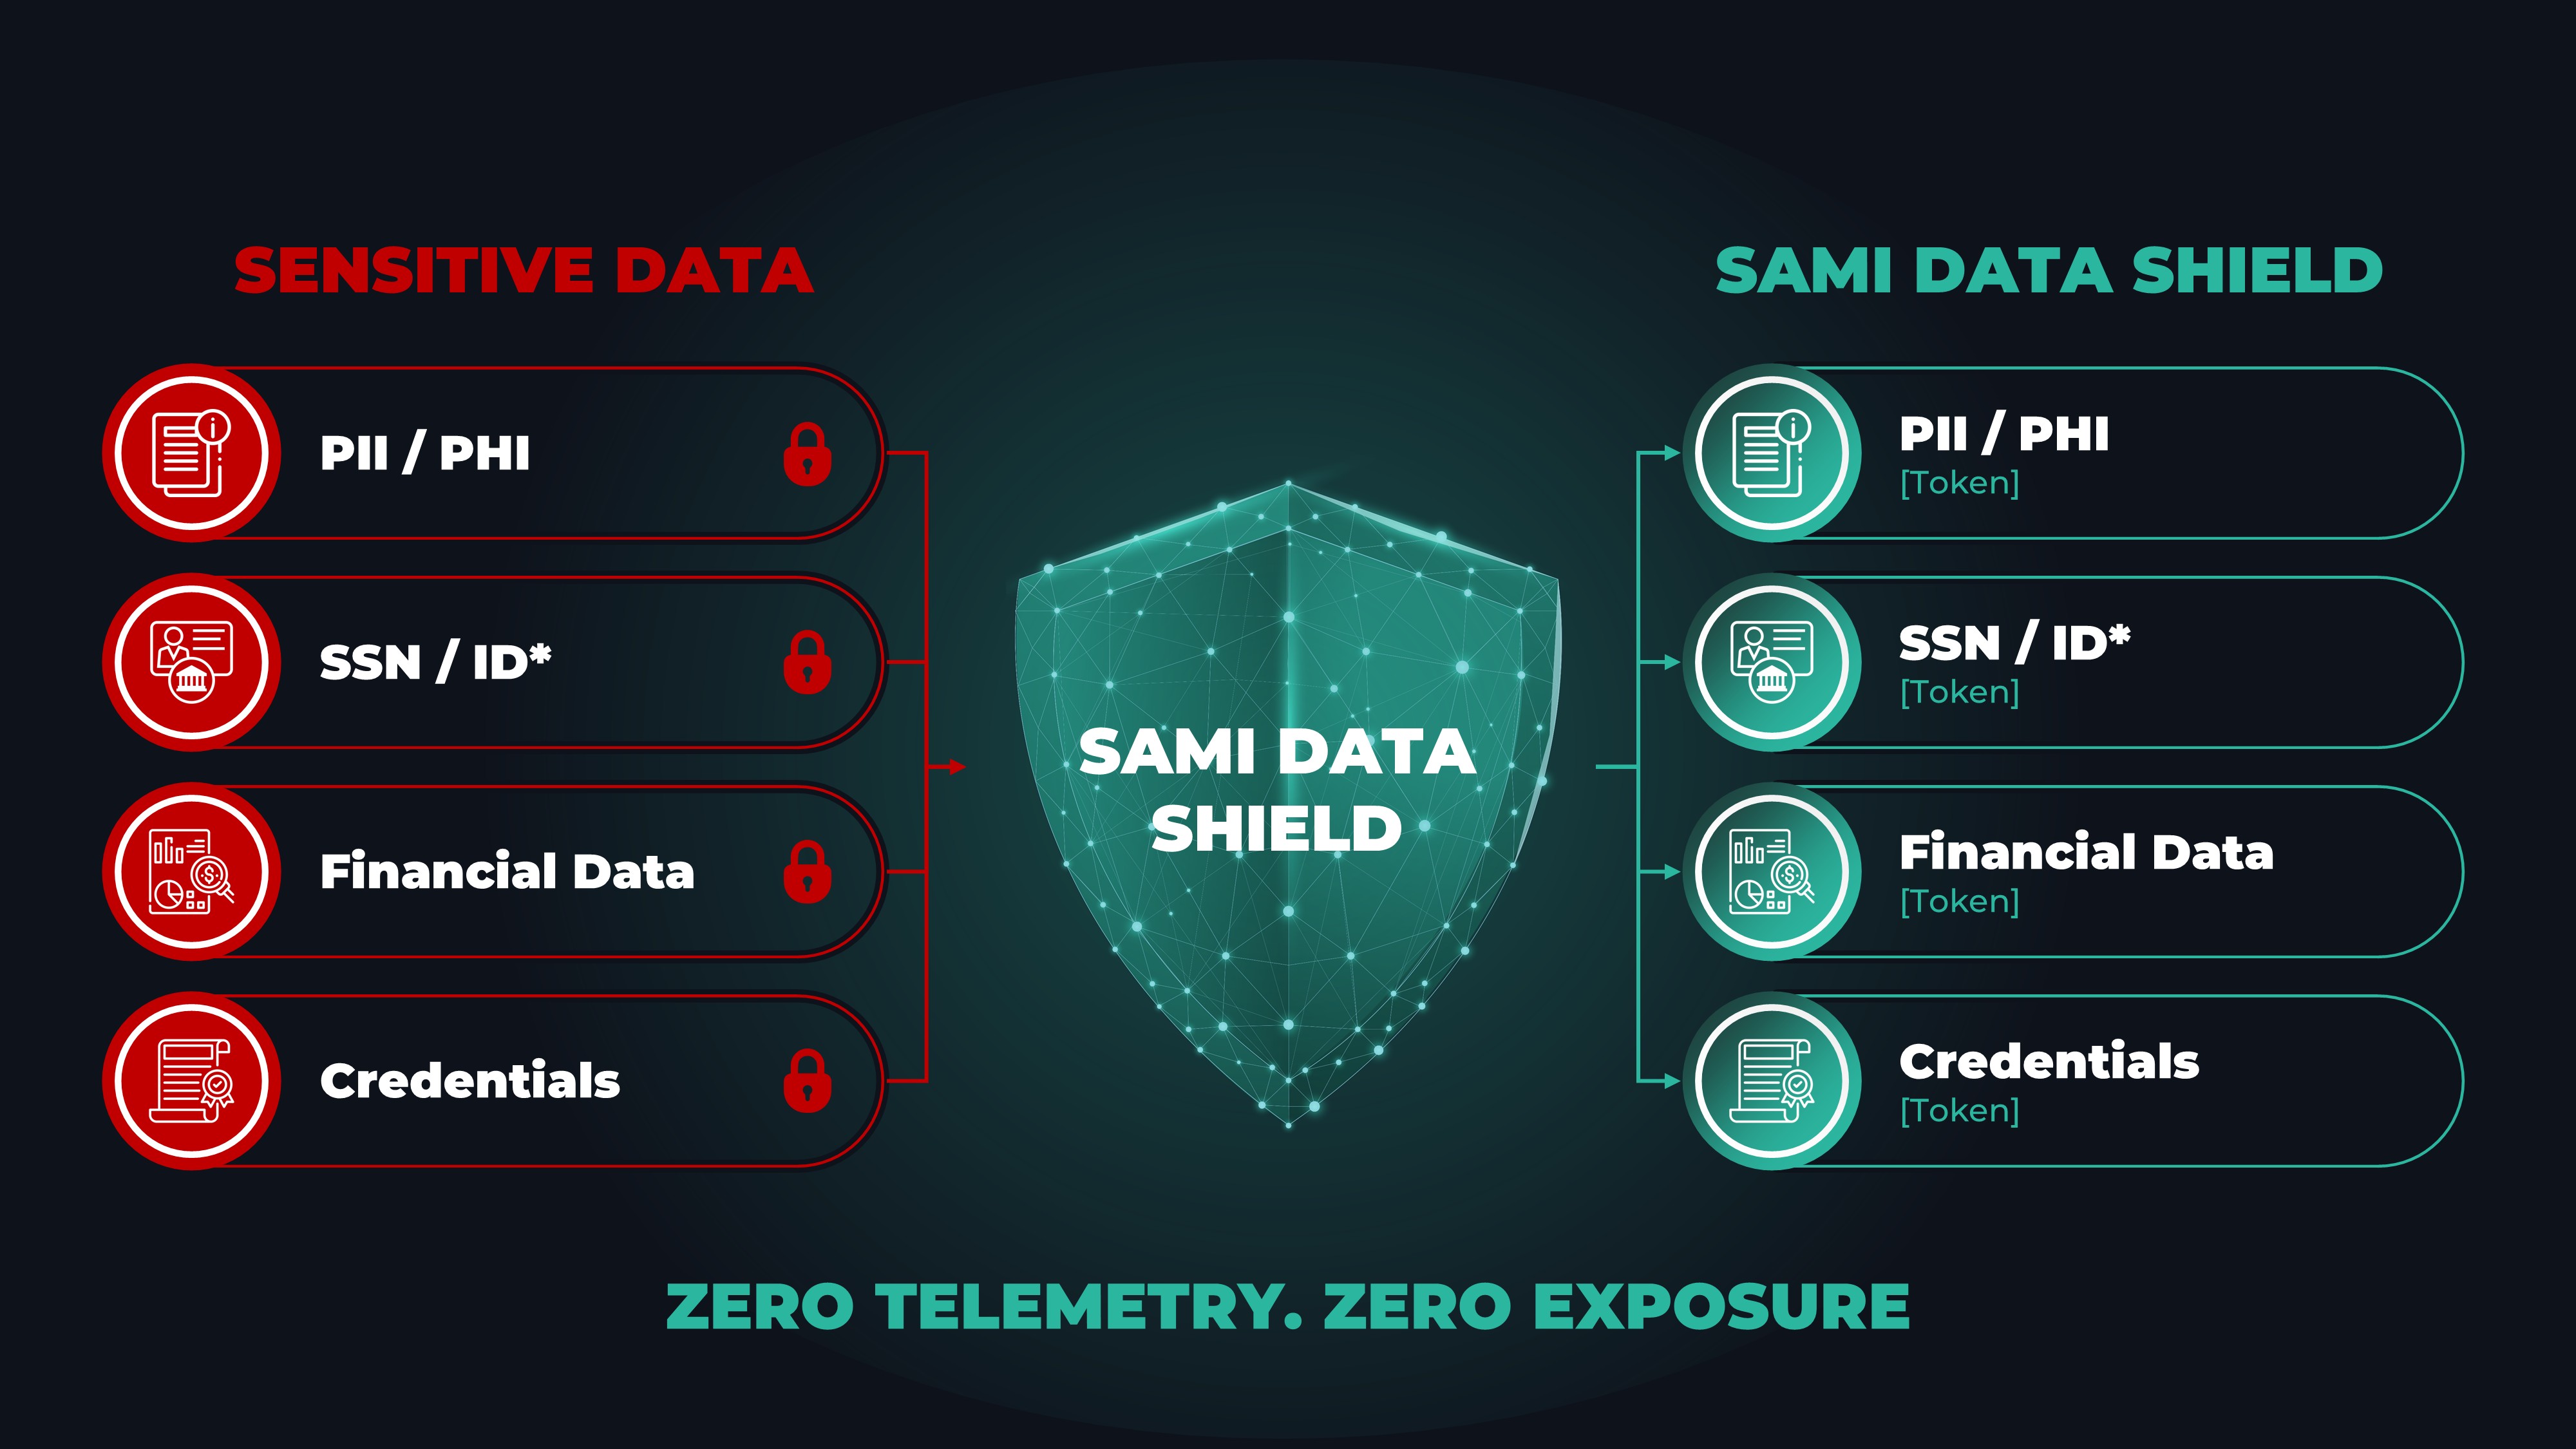
The problem is that most AI tools make the boundary between “useful assistance” and “sensitive data exposure” invisible. Every prompt can carry proprietary data, personal information, health data, customer records, contracts, credentials, or regulated context into systems you do not fully control. SAMI makes privacy structural, so data protection does not slow down your AI journey. Sensitive data is detected, redacted, tokenized, blocked, or processed locally before it reaches the model.
YOUR DPO NEEDS PROOF, NOT PROMISES
"When employees or your customers use AI with proprietary, personal, or regulated data, SAMI proves what happened: what was allowed, what was redacted, what was tokenized, what was blocked, and what stayed inside your environment, which privacy data did your AI access or which was sent out etc.
Why filtering output is not privacy and why architecture is
Most AI security tools create
the exposure they claim to prevent.
To inspect a prompt for sensitive data, most AI security tools send the prompt to their cloud for analysis. That means your engineers' proprietary code, your customers' PII, your confidential context all transmitted to a third party for processing. SAMI's Fully Private mode sends nothing. All analysis runs locally. Autnhive sees no data. Ever.
Tokenize-before-AI goes further. Sensitive data is tokenized locally before any model contact. The AI model whether local or external receives only tokenized content and processes it without ever seeing the sensitive values. SAMI rehydrates the real values in the output. Full accuracy. Zero exposure.
✓
Tokenize-before-AI ★ UNIQUE PII, PHI, and proprietary data tokenized locally before model contact. Model processes tokens only. SAMI rehydrates real values in output. Model never saw the data.
✓
GDPR Art.25 by architecture not detection, not filtering-after-the-fact. Structural privacy. The model cannot access what was never in its input.
✓
Calibratable privacy 3 modes ★ UNIQUE Fully Private (zero telemetry), Audit Mode (metadata only), Full Retention (complete forensic trail). Full SAMI capability across all three modes.
✓
Air-gapped from day one designed for classified defense and high-security banking as the default deployment, not a premium add-on. Zero external calls under any circumstance in Fully Private mode.
✓
On-prem sidecar deploys alongside your AI infrastructure. Compatible with Llama, Mistral, Falcon, and any fine-tuned model. No architecture changes required.
No other AI security platform offers a zero-telemetry privacy mode with full capability. SAMI supports private, on-prem, air-gapped, and zero-telemetry deployment where required. IBM watsonx.governance: partial on-prem only. SAMI is the only platform where full capability and zero data exposure are the same deployment mode.
How tokenization works step by step
1
Input arrives with sensitive data
PII, PHI, trade secrets, proprietary code detected by SAMI input screening locally.
2
Tokenization applied locally
Sensitive identifiers tokenized. Nothing leaves the environment.
3
Model processes tokens only
AI model local or external receives only tokenized content. Full analytical capability maintained.
→
4
SAMI rehydrates real values
SAMI rehydrates local PI data and user receives complete, accurate response.
✓
Sensitive data never left the jurisdiction
Engineer productive. IP protected. No ban required. GDPR Art.25 satisfied by design.
✓
All analysis local. Autnhive sees no data. Air-gapped and classified environments. Full SAMI capability.
Event types and timestamps only. No content transmitted. GDPR-sensitive deployments. EU AI Act evidence trail.
Full interaction logging. SOC 2 Type II. Financial regulators. Legal hold. Every decision traceable.
An AI vulnerability assessment before launch
cannot protect you from attack techniques that emerge after launch.
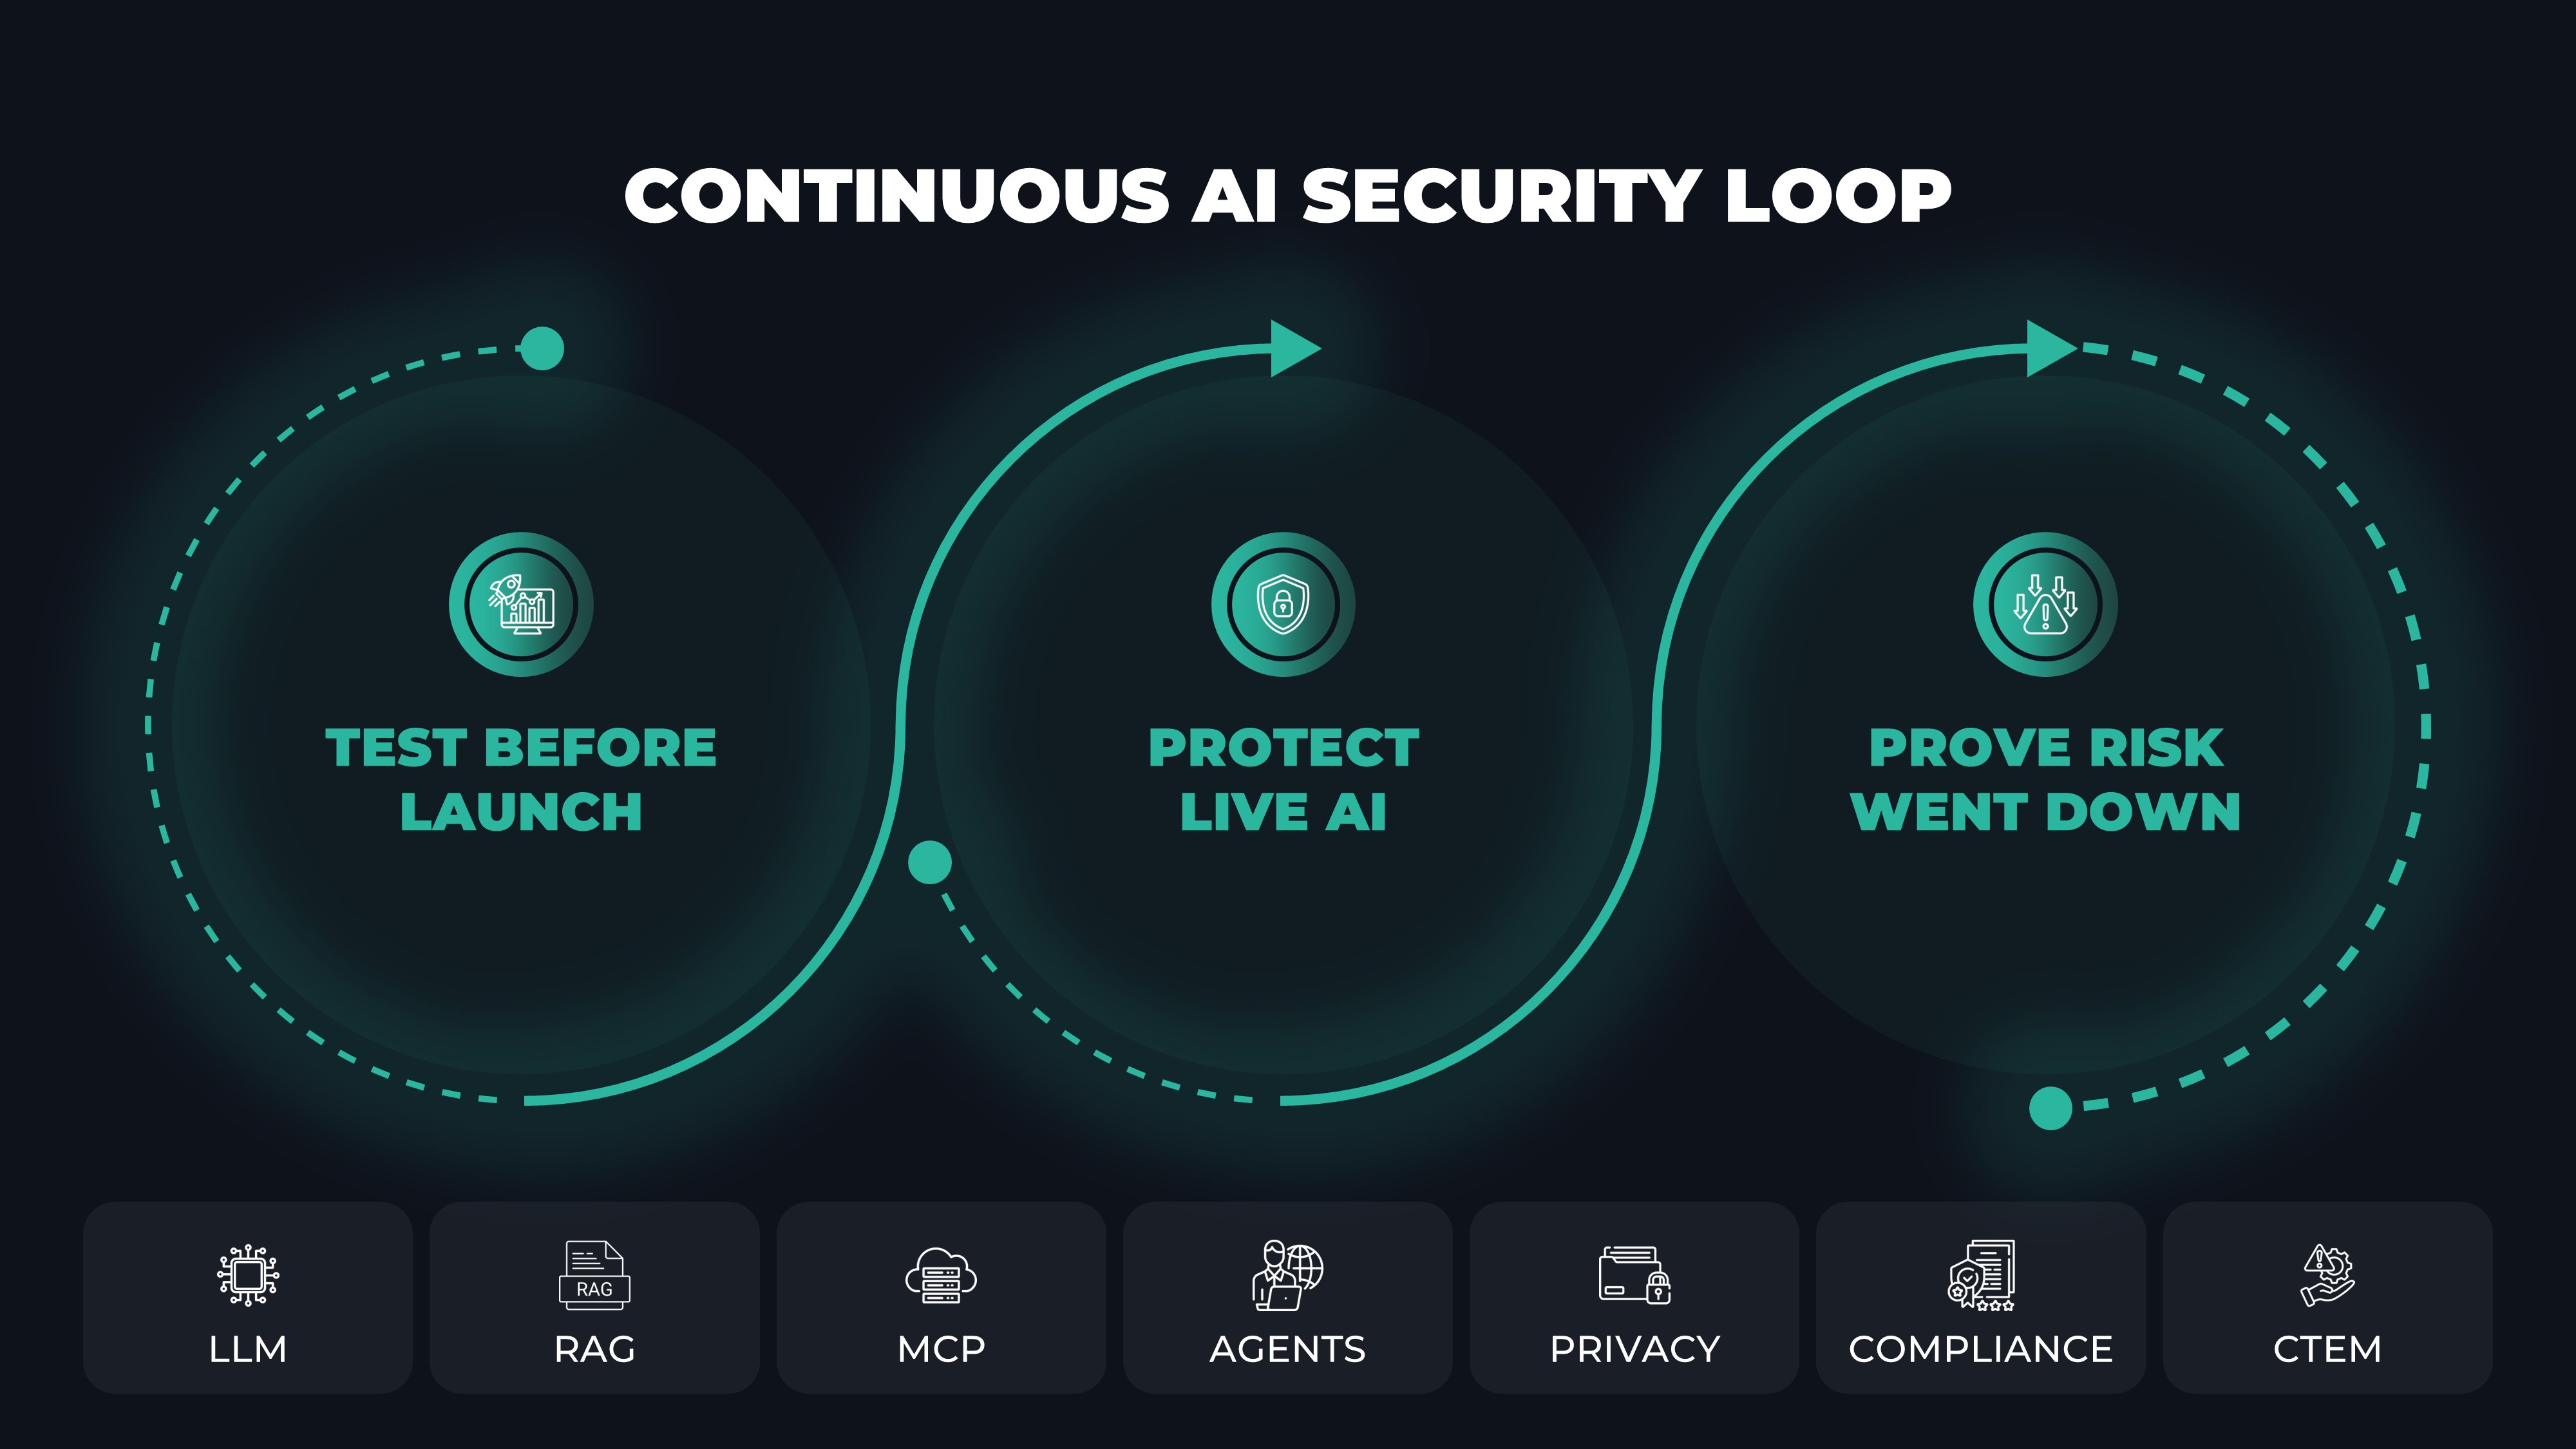
AI attack methods change constantly: prompt injection, jailbreak variants, model manipulation, agent hijacking, tool-call abuse, RAG poisoning, sensitive-data extraction and more. Even AI red teaming performed before launch becomes stale as new attack paths appear. SAMI continuously conducts vulnerability assessment and simulates adversarial attacks across the LLM, MCP and Agents, external facing AI system, so your defenses keep up as attackers change.
The CTO question
"Have you tested your AI against jailbreak and prompt injection attacks and is that testing continuous, or was it a one-time engagement six months ago?"
Why continuous simulation is the only answer
Attackers don't wait for
your next scheduled assessment.
The pen tester who assessed your AI in January used techniques that existed in January. The attacker targeting you in October has access to techniques published in September, August, and July plus zero-days the community hasn't documented yet. Continuous simulation means SAMI always tests with the latest known techniques, not the ones from your last engagement.
✓
Three attack surfaces LLM, MCP, Agentic ★ UNIQUE continuous adversarial simulation across LLM endpoints, agentic pipelines, and MCP tool connections simultaneously. No competitor covers all three.
✓
OWASP LLM Top 10 v1.1 full coverage of all 10 AI attack vectors, continuously. Not a checkbox compliance exercise.
✓
MITRE ATLAS the AI-specific adversarial attack framework. Full technique library, continuously applied.
✓
BRI per finding ★ UNIQUE every finding assigned a dollar-value breach exposure score. Fix what reduces liability most. Not fix what has the highest CVSS label. Fix what costs you most if exploited.
✓
SEC material risk ready BRI financial liability per AI system using IBM Cost of Breach methodology. P50/P75/P95 scenarios. Board-ready language. SEC material risk disclosure-ready.
SAMI combines : AI attack simulation with FLE/SPI/BRI impact scoring. NeMo Guardrails partial LLM testing only, no MCP or agentic coverage. IBM watsonx.governance no attack simulation. SAMI is the only platform offering continuous simulation across all three AI surfaces with financial liability scoring per finding.
OWASP LLM Top 10 full coverage, all environments
LLM01
Prompt Injection direct and indirect
CRITICAL
LLM02
Insecure Output Handling
CRITICAL
LLM03
Training Data Poisoning / RAG Poisoning
HIGH
LLM06
Sensitive Information Disclosure
CRITICAL
LLM08
Excessive Agency agent scope violation
CRITICAL
+5 more
LLM04 DoS · LLM05 Supply Chain · LLM07 Plugins · LLM09 Overreliance · LLM10 Theft
COVERED
The BRI difference: Every finding gets a dollar value. "Critical severity" is a label. "$2.4M expected breach cost if exploited" is a number your CFO understands, your board approves remediation for, and your SEC filing can reference. SAMI speaks the language that gets things fixed.
You connected your AI to your knowledge base.
That knowledge base is now an attack surface.
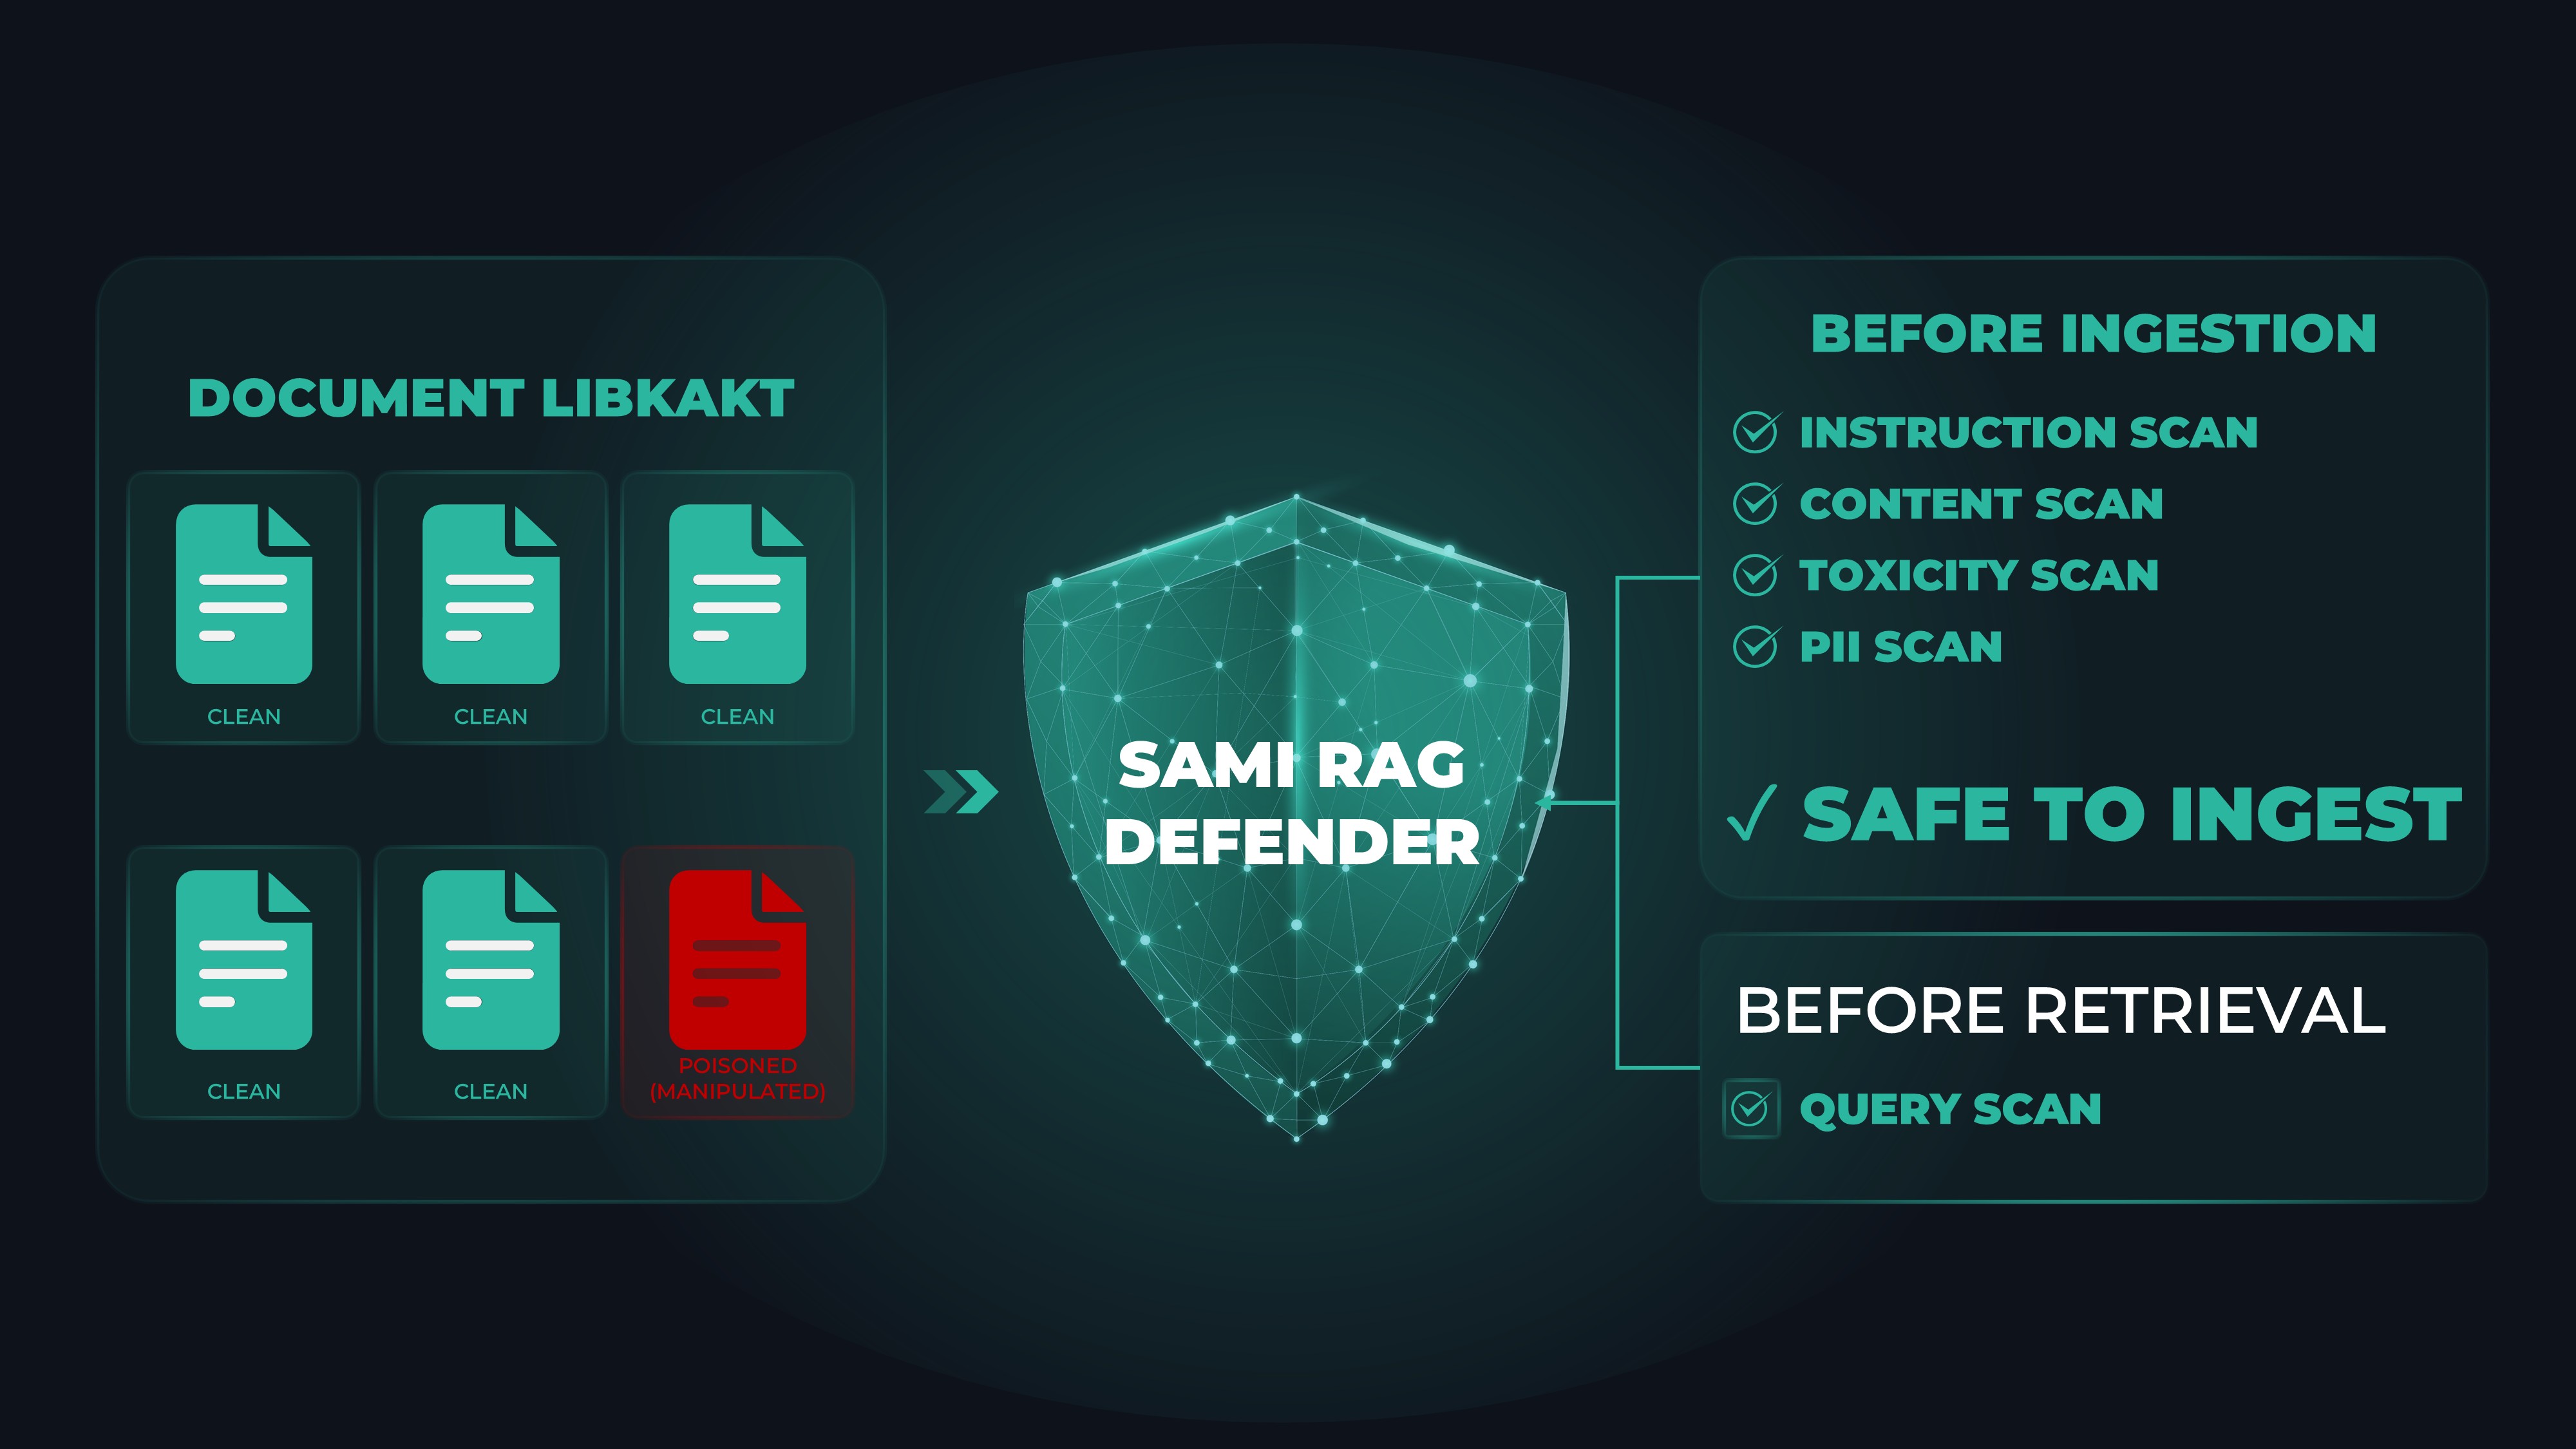
RAG Defender operates at two independent points: ingestion-time (before any document enters your knowledge base) and query-time (before any retrieved content reaches the model). Two layers covering 8 poisoning vectors no other platform addresses.
The question for your AI architect
"If an attacker contributed a document to your knowledge base today how many AI responses would be influenced before anyone noticed?"
The Slack AI incident and how it applies to your organization
No hacking required.
Just a message your RAG pipeline trusted.
In August 2024, an attacker with access to any public Slack channel embedded a hidden instruction in a message. When a victim later asked Slack AI to summarise their private channels, the AI executed the attacker's instruction and exfiltrated private data. No malware. No credentials. No vulnerability exploit. Just text that the RAG pipeline retrieved and trusted.
If your AI retrieves from any source that external parties can contribute to shared wikis, connected email, uploaded documents, indexed websites you have this attack surface right now.
✓
Ingestion-time quarantine workflow ★ UNIQUE suspicious documents quarantined before entering the knowledge base. Structured approve/reject review loop with audit events. No competitor has this operational workflow. Tainted content cannot accumulate silently.
✓
Query-time indirect injection removal ★ UNIQUE retrieved context re-screened before model contact. Hidden instructions detected and stripped. The Slack AI attack stopped here.
✓
8 poisoning vectors covered including embedding manipulation and supply-chain attacks that content-level filters cannot detect.
✓
Multi-tenant knowledge base isolation one tenant's documents cannot influence another tenant's AI responses. Cross-tenant data leakage structurally prevented.
✓
Agentic pipeline support RAG Defender covers agentic retrieval workflows. Poisoned context cannot propagate through multi-step agent chains.
Lakera Guard covers some inbound injection detection. Protect AI Guardian covers model/package risk. RAG needs two checkpoints: before storage and before generation.SAMI inspects both. None have ingestion-time quarantine workflow. None cover embedding poisoning or supply-chain attacks.
Some ways attackers poison what your AI retrieves and believes
Document injection
Hidden instructions in shared documents hijack AI responses when retrieved.
Web content poisoning
Malicious indexed pages inject false authoritative instructions via RAG.
Database manipulation
Tampered records cause AI to present false data as verified fact.
Supply chain poisoning
Third-party data feeds compromised before ingestion. The SolarWinds pattern applied to AI knowledge.
Embedding poisoning
Vector embeddings biased to retrieve malicious content. Invisible to all content-level filters.
Context collision
Injected content overrides legitimate context in the retrieval window.
Chunk-level injection
Instructions buried inside document chunks to survive RAG splitting.
Ranking manipulation
Attacker content crafted to score highest in retrieval and be prioritized by the model.
Two-layer defense both in the execution path: Ingestion screening catches the document before it enters the KB. Query-time screening catches the hidden instruction before the model sees it. An attacker who bypasses one still faces the other.
Inside ASDR, AI CTEM continuously tests the AI attack surface.
LLMs · RAG · MCP · agents · external-facing AI · AI applications · supporting infrastructure
Runtime protection ← Security EngineLLMs · RAG · MCP · agents · external-facing AI · AI applications · supporting infrastructure
AI CTEM · LLMs · RAG · MCP · Agents
Do not just protect AI.
Continuously try to break it.
SAMI AI CTEM continuously discovers the AI attack surface, simulates attacks, validates whether weaknesses are exploitable, prioritizes the paths that matter, drives remediation and re-tests as models, tools, permissions and workflows change.
13%
of the 600 breached organizations in IBM's 2025 study reported breaches involving AI models or applications.
1 in 5
organizations in that breach-study population reported a breach due to shadow AI.
+$670K
average breach cost associated with high levels of shadow AI versus low or no shadow AI in IBM's study.
Source: IBM Cost of a Data Breach Report 2025 / IBM Newsroom. These figures describe IBM's population of organizations that had experienced breaches.
AI CTEM
One-time testing is not enough for a changing AI environment.
AI CTEM gives a continuous view of what exists, how it may be attacked and what should be fixed first.
Continuous AI CTEM loop
DiscoverSimulateValidatePrioritizeRemediateRe-test
LLM CTEMContinuously test prompt injection, jailbreaks, unsafe configuration, data extraction and model exposure.
RAG CTEMAssess poisoning, retrieval abuse, access boundary issues and the trustworthiness of knowledge sources.
MCP & Agent CTEMTest tool trust, permission misuse, action reachability and the blast radius of autonomous workflows.
Coverage matrix
Assessment area
LLMs
RAG
MCP
Agents
Discovery
Model use & exposure
Knowledge paths
Servers & tools
Autonomous workflows
Simulation
Jailbreaks & prompt attacks
Poisoning & retrieval attacks
Tool trust & misuse tests
Rogue action paths
Validation
Exploitability
Data impact
Permission failure
Reachable actions
Prioritization
Model risk
Knowledge risk
Operational risk
Business action risk
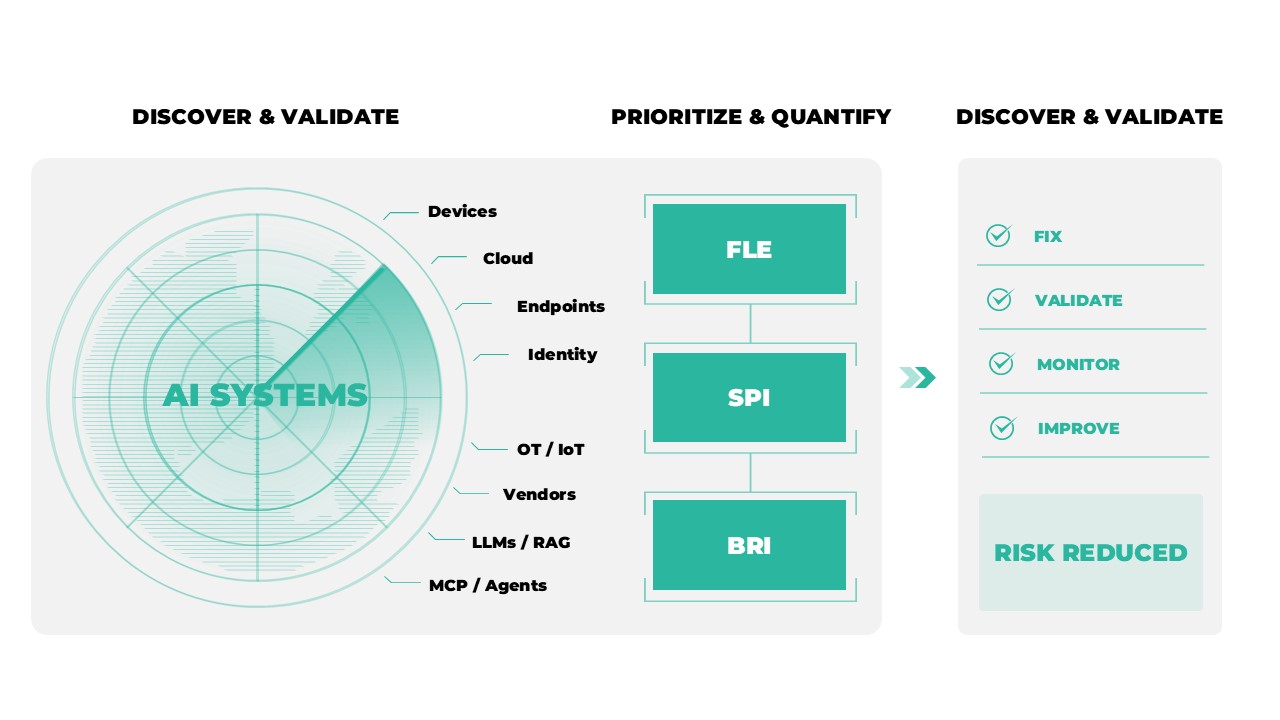
Prioritize the AI exposure that matters most and know what to fix first.
Continuous Threat Exposure Management
Your scanner found 3,200 things.
Here's why that number is useless.
Finding risk is the easy part. Knowing which three matter this week, what they cost in dollars, and closing them before anyone else finds them that's SAMI. Meanwhile every day those findings sit unaddressed, your liability compounds.
Validated in production CMiC Global & Salesloft, Feb 2025
"97% of SAMI's findings were confirmed true positives. A leading external risk platform returned ~35% on the same assets." That 62-point gap is what your team spends their week on while real vulnerabilities accumulate compounding liability.
The gap most teams don't see until the breach, the audit, or the insurance renewal
✗3,200 findings. No way to know which three are actively exploitable today.
✓Attack simulation validates every finding. 73% is noise. Three advance the right three.
✗CVSS 7.8 doesn't say whether that finding costs €50K or €5M when exploited.
✓FLE gives you the dollar number. SPI ranks by business impact, not a generic score.
✗800 open Jira tickets. Nobody knows which sprint owns them or what done means.
✓SAMI creates the ticket pre-filled with fix steps and ROI, and manages it to closure.
The SAMI Continuous Risk Loop
From first asset to closed ticket to board proof.
Seven stages. Fully automated. Continuously.
This is the process your team runs manually today across 10–15 disconnected tools. SAMI runs all seven stages end-to-end, automatically. Click any stage.
↑ Click any segment to explore
One platform. All seven stages. No gaps.
Most organizations cover stages 1–2 with scanners, maybe stage 3 with an annual pen test, then nothing. No dollar liability. No fix planning. No proof it worked. SAMI runs all seven stages continuously connected, automated, end to end.
Without SAMI: 10–15 tools, each covering 1–2 stages. Nothing connected. No dollars. No closure.
With SAMI: All 7 stages. One platform. Continuous. Automated from first finding to board proof.
Attack surfaces 13 covered
Every surface attackers use.
Including the ones added last Tuesday.
Click any surface to see what SAMI finds, what attackers do there, a real recent incident and what changes when SAMI is covering it.
Endpoints Windows, Linux, macOS
Every device is a door. Most have one left unlocked.
What SAMI does: Continuously assesses every managed endpoint against CIS benchmarks. Finds misconfiguration, unpatched software, and privilege escalation paths before attackers do.
When you feel the pain without it: Your EDR fires after the breach. Your patch management tool tells you what's missing not whether it's exploitable in your environment. SAMI validates exploitability and assigns FLE so you know which missing patch costs €800K if exploited, and which can wait.
With SAMI: Every endpoint finding carries a dollar value. Your team works on endpoints that matter, not endpoints that scored highest on a CVSS calculator.
Recent incident: MGM Resorts (2023) a 10-minute social engineering call gave attackers Active Directory access. Endpoint and identity misconfiguration mapped to attack paths SAMI surfaces continuously.
Network & Firewall Attack Simulation
Everyone checks firewall policies. Almost nobody tests if they actually work.
What SAMI does: Runs continuous attack simulation against your network controls and firewall rules not just configuration checks. Tests whether your firewall can withstand the specific techniques being used against organizations like yours today.
When you feel the pain without it: Your firewall policy review says "compliant." Then an attacker uses a technique your policy doesn't cover, and you find out months later. Policy review ≠ attack resistance. SAMI runs the attack if it gets through, you know before the attacker does.
With SAMI: Your firewall is validated against live attack techniques, not just checked for correct configuration. Network segmentation tested. Lateral movement paths mapped. FLE assigned per gap.
Recent incident: Volt Typhoon (2023-24) Chinese state actors lived inside US critical infrastructure networks for months, undetected, by exploiting misconfigured network devices. Policy compliance and attack resistance are not the same thing.
Wi-Fi Security
51 active checks. PCAP forensics. The surface IT forgets at renewal time.
What SAMI does: 51 active wireless security checks plus PCAP forensic analysis. Detects rogue access points, weak encryption, Evil Twin attacks, and authentication vulnerabilities across your wireless estate.
When you feel the pain without it: Wi-Fi security gets reviewed at implementation and then never revisited. A rogue access point running for 6 months is invisible until someone trips over the cable. SAMI continuously monitors your wireless perimeter not just at audit time.
With SAMI: Every wireless finding carries FLE scoring. Rogue APs detected within hours, not quarters. PCAP evidence available for forensic investigation.
Third-Party & External DAST, Pen Testing, Exposed Products
Your external surface is what attackers see. SAMI sees it first.
What SAMI does: Continuous DAST against your externally-facing applications. Automated pen testing updated as new techniques are published. External attack surface mapping covering domains, subdomains, exposed APIs, shadow assets, and externally-facing products. IoT/OT device exposure analysis. External-facing AI system assessment. WAF validation against 200+ bypass techniques.
When you feel the pain without it: Your annual pen test covers what existed 11 months ago. Your WAF report says "rules active" not "rules effective." An externally-facing API deployed by a dev team three weeks ago has no security assessment. SAMI covers your external surface as it exists today, not as it existed last year.
With SAMI: Every new external asset assessed within 24 hours of discovery. Pen testing runs continuously, not annually. WAF validated against live bypass techniques. IoT and OT exposure mapped with FLE per finding.
Recent incident: MOVEit Transfer (2023) zero-day in an externally-facing file transfer application led to hundreds of breaches across industries. Continuous external surface monitoring catches new deployments before attackers find them.
Identity & Access Management (IAM)
Identity is the new perimeter. It's also the most misconfigured one.
What SAMI does: Continuously assesses IAM configuration across your environment Entra ID / Azure AD, AWS IAM, GCP IAM, and on-premises Active Directory. Maps privilege escalation paths, over-permissioned roles, stale accounts, and MFA bypass vectors. Identifies attack paths from any identity to your most critical assets.
When you feel the pain without it: Your IAM review is annual. Accounts accumulate permissions over time no one removes what's no longer needed. A stale service account with Domain Admin rights is invisible until an attacker uses it. SAMI continuously maps identity risk and assigns FLE per path.
With SAMI: Every privilege escalation path carries a dollar liability. Stale accounts flagged within hours of becoming risk. Crown jewel access paths mapped continuously not discovered during the forensic investigation.
Recent incident: MGM Resorts (2023) Scattered Spider used vishing to get Okta credentials, then moved laterally through overpermissioned identities. SAMI's IAM CTEM maps exactly these privilege escalation paths continuously.
M365 & Google Workspace
Where your data lives. Where attackers go first.
What SAMI does: Continuously assesses M365 and Google Workspace configuration. Entra ID attack paths, Exchange mail flow rules with exfiltration potential, Teams guest access misconfigurations, SharePoint over-sharing, OAuth app permissions, and conditional access gaps.
When you feel the pain without it: Microsoft Secure Score tells you what Microsoft recommends. It doesn't tell you which misconfiguration an attacker can exploit today. A Secure Score of 68 can coexist with three confirmed Entra ID attack paths. It does, regularly.
With SAMI: Every M365 and Google Workspace finding validated for exploitability. FLE per path. Remediation guidance specific to your configuration not generic Microsoft documentation.
Recent incident: Microsoft Exchange Online breach (2023) attackers used a stolen MSA signing key to forge tokens and access cloud email across multiple organizations. SAMI's M365 CTEM covers token and authentication risk continuously.
Cloud AWS, Azure, GCP
Every change creates a new configuration. SAMI retests within 24 hours.
What SAMI does: Continuous cloud configuration assessment across AWS, Azure, and GCP. Detects misconfiguration, over-permissioned roles, exposed storage, and insecure defaults. Integrates with your existing cloud security tooling. Cloud findings produce IaC-ready remediation output (Terraform/Bicep).
When you feel the pain without it: A developer spins up a new resource with a public IP. A security group widens for testing and never tightens back. Your quarterly cloud audit finds it months later after it's been an active attack vector. SAMI detects every change within 24 hours and validates exploitability before it becomes a breach.
With SAMI: Cloud drift caught in hours, not quarters. Every misconfiguration carries FLE. IaC-ready remediation means DevOps can fix it in the same sprint it's found.
Recent incident: Capital One (2019) misconfigured AWS WAF and overpermissioned EC2 role exposed 100M+ records. Cloud misconfiguration remains the leading cause of cloud breaches. SAMI catches drift before attackers do.
OT / IoT / ICS / SCADA
27+ industrial protocols. The surface that can't go offline to be patched.
What SAMI does: Assesses OT/IoT/ICS environments without disrupting operations. Supports 27+ industrial protocols. Maps every connected device, identifies legacy vulnerabilities, and produces FLE-scored findings your engineering and risk teams can actually act on.
When you feel the pain without it: OT assessed in isolation, separate tools, separate reports. A PLC finding scored against OT benchmarks in isolation looks different from the same finding scored in the context of your full risk picture adjacent to IT attack paths, connected to production systems, with regulatory exposure. Context changes priority completely.
When you feel the pain without it: OT security is assessed in isolation a separate team, separate tools, separate report that never connects to your broader risk picture. A vulnerable Siemens PLC assessed in isolation scores differently than the same finding in context connected to production systems, with OT-specific regulatory exposure, adjacent to IT systems with active exploits. SAMI maps OT risk in the same FLE/SPI framework as everything else. Context changes the priority completely.
With SAMI: OT/IoT findings in the same SPI/BRI scoring framework as all other surfaces. Board report includes OT liability. Remediation orchestrated alongside IT findings.
Recent incident: Oldsmar water treatment plant (2021) attacker remotely increased sodium hydroxide levels 111× via an exposed remote access tool. ICS security assessment is a core SAMI CTEM surface.
Applications Custom, Vibe-Coded & Supply Chain
The fastest-growing attack surface. The one most security teams aren't ready for.
What SAMI does: SAST, DAST, API security, and dependency scanning for custom-built applications. Specific assessment of vibe-coded apps AI-assisted development where developers accept LLM-generated code without full review, introducing insecure defaults and exposed credentials. Software composition analysis and SBOM risk for third-party and supply chain dependencies.
When you feel the pain without it: A developer ships a feature built with Copilot in two hours. Nobody reviewed the LLM-generated authentication logic. Your DAST scanner wasn't updated to cover that new endpoint. Three months later, it's a breach. SAMI covers apps as they're shipped, not 6 months after.
With SAMI: Every new deployment assessed. Vibe-coded code scanned for AI-specific risk patterns. Supply chain dependencies mapped to live CVEs with FLE per finding.
Recent incident: XZ Utils backdoor (2024) a malicious contributor spent two years building trust before embedding a backdoor in a widely-used compression library. SAMI's supply chain CTEM identifies dependency risk before exploitation.
AI, LLM, MCP & Agentic Security
OWASP Top 10 for LLM Applications 2025 · MITRE ATLAS · The surface your WAF can't see.
What SAMI does: Continuously assesses your AI deployment against all OWASP LLM Top 10 categories and MITRE ATLAS AI attack patterns. LLM endpoint vulnerability assessment, MCP tool permission analysis, agentic chain blast radius simulation. Assigns FLE per finding. Re-assesses within 24 hours of every model or pipeline change.
When you feel the pain without it: AI vulnerabilities don't look like vulnerabilities. No malware, no unusual ports. Prompt injection, RAG poisoning, and agent hijacking appear as normal API calls because they are. WAF, SIEM, and EDR need AI context to judge prompt intent, retrieved-content risk, and agent action scope. You have no idea they're happening until the data is gone.
With SAMI: Every AI interaction inspected in real time. Every AI surface assessed continuously. Complete audit trail: who sent the prompt, what RAG data was retrieved, what the agent did, what the model returned.
Recent incident: Slack AI (Aug 2024) attackers injected instructions into documents retrieved by Slack's AI assistant, exfiltrating private messages from other users. Covered by SAMI RAG Defender at ingestion-time and query-time.
How SAMI compares
Other tools find risk.
SAMI is the only one that closes it.
The differences determine whether your team spends the week closing real risk or validating false positives.
97%
SAMI true positive rate
CMiC Global & Salesloft, Feb 2025
~35%
Black Kite / SecurityScorecard
Same assets · Same timeframe · Validated
73%
Scanner noise eliminated
Before any finding reaches your team
| Capability | SAMI | Tenable Nessus/One |
Qualys VMDR |
Black Duck Synopsys |
Security Scorecard |
Black Kite |
|---|---|---|---|---|---|---|
| Scoping | ||||||
| Mapping Endpoint Assets | ✓ | |||||
| Mapping Network Assets | ✓ | |||||
| Mapping Cloud Assets | ✓ | |||||
| Mapping Softwares | ✓ | |||||
| Discovery | ||||||
| Vulnerability scanning | ✓ | ✓ | ✓ | Partial | ✓ | ✓ |
| External attack surface + pen testing (continuous) | ✓ | Partial | Partial | ✓ | ✓ | |
| IAM / identity attack path mapping | ✓ | Partial | Partial | |||
| M365 / Google Workspace misconfiguration | ✓ | |||||
| OT / IoT / ICS / SCADA | ✓ | Partial | Partial | |||
| LLM / AI / MCP / Agentic security | ✓ | |||||
| Supply chain / SBOM / vibe-coded app risk | ✓ | ✓ | Partial | Partial | ||
| Validation | ||||||
| Network & firewall attack simulation | ✓ | |||||
| Attack simulation validates exploitability (not just existence) | ✓ | |||||
| BIA & Priority | ||||||
| Dollar liability per vulnerability (FLE) | ✓ | |||||
| Remediation Modelling | ||||||
| Business-context prioritisation replacing CVSS (SPI) | ✓ | |||||
| Orchestration | ||||||
| Remediation orchestration tickets managed to closure | ✓ | |||||
| Reporting | ||||||
| EU AI Act Article 9 continuous evidence | ✓ | |||||
The Loop No Competitor Closes
Finding risks fills dashboards.
Fixing the right ones changes outcomes.
Your security team closed 240 tickets last quarter. How many of those actually reduced your financial liability? Which three would have mattered most if attackers had arrived last Tuesday? Without SAMI, nobody knows. With SAMI, everybody does before a single hour is spent.
The remediation backlog problem
The average enterprise security team has 1,400 open findings. They close about 60 per month. At that rate, they will never catch up. The question is not "how do we close more tickets?" The question is "which 6 tickets, if closed this week, would reduce our liability by 80%?"
The Question SAMI Answers That Others Don't
"Are you fixing what reduces real liability the most and can you prove it worked?"
The 6-Step Loop
Model. Assign. Track.
Validate. Prove.
Click each step to see exactly what SAMI does and what no other platform does.
Step 01
Validated Finding
Attack-confirmed only
Step 02
Risk Business Impact Assessment & Prioritization
Fix-first order
Step 03
Remediation Modelling
Liability delta before fix
Step 04
Remediation Orchestration
Right team, right tool
Step 05
Track & SLA
Live visibility
Step 06
Re-Validate
Prove it worked
Step 01: Validated Finding
SAMI only advances findings that have been confirmed exploitable by attack simulation. Before any remediation effort is spent, SAMI has already proved an attacker can actually reach and exploit the vulnerability in your specific environment. This single step eliminates an average of 73% of typical scanner noise ensuring every remediation ticket represents a real, confirmed risk.
Noise Reduction
73% avg
False Positive Rate
< 2%
Time to Validate
< 4 min
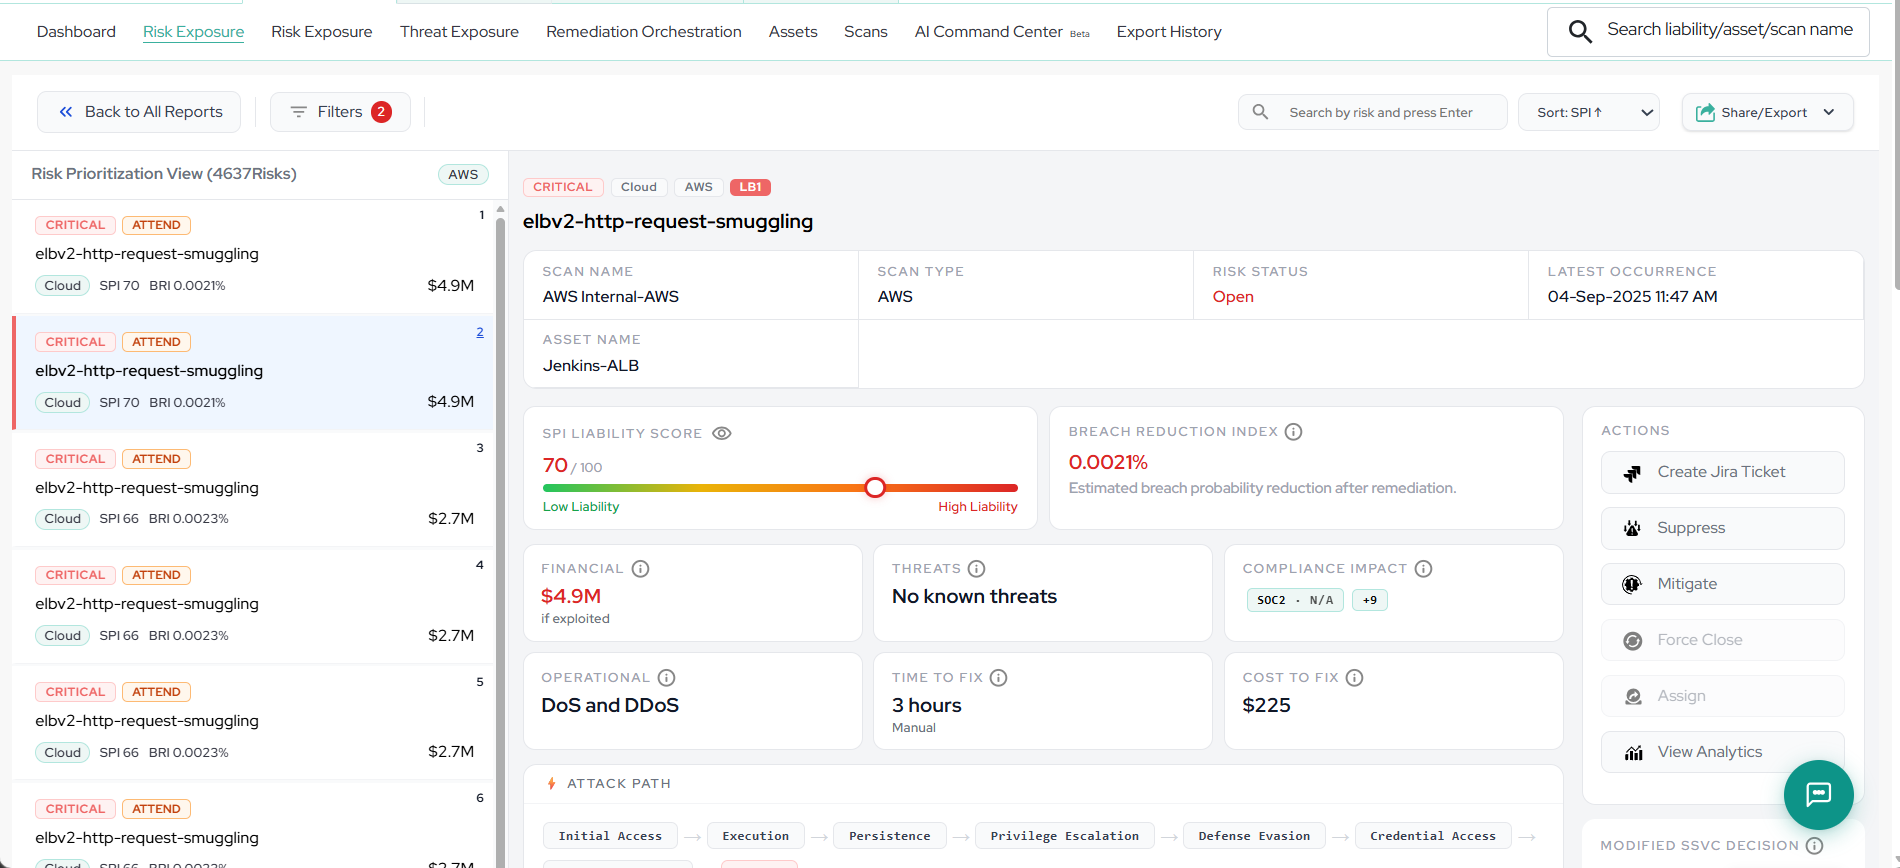
Integrations
Fits your existing
workflow exactly.
SAMI doesn't ask your team to change tools. It enriches the tools they already use.
Jira / ServiceNow
Validated findings become tickets automatically. SPI score, financial liability, effort estimate, and fix guidance in every ticket body.
SIEM / SOAR
AI attacks feed as first-class incidents. OWASP LLM IDs, SPI scores, and liability data included. SOC works exactly as before just with full AI visibility.
Slack / Teams
Real-time remediation updates, SLA alerts, and re-validation confirmations via existing channels. No new notification fatigue.
Coming Soon...
Coming Soon...
CI/CD Pipelines
Security findings in your DevOps workflow. Block deployments on Critical SPI findings. AI security gates in your pipeline.
Terraform / IaC
Cloud findings produce IaC-ready remediation code. Handed directly to DevOps no manual translation, no rewriting.
Compliance Platforms
EU AI Act, HIPAA, ISO 27001, SOC 2 evidence auto-exported. Audit-grade PDF and JSON. Reduces manual GRC work from weeks to minutes.
Insurance Brokers
P50/P75/P95 liability model plus SAMI coverage summary generated on demand. Insurer-grade format. Premium negotiation evidence.
Board Reporting
One-click board PDF: BRI trend, SPI queue, liability reduction achieved, regulatory exposure, remediation velocity. No manual slides.
Newsroom
Featured News.
Real-world incidents. Platform announcements. Threat intelligence. Regulatory developments. The AI security landscape changes daily SAMI tracks what matters.
Autnhive announces "SAMI for AI" at the 2026 World Defense Show in Riyadh, Saudi Arabia. Autnhive's breakthrough security platform for AI systems - SAMI for AI, the world's most comprehensive security platform for AI systems, was recently announced by Devi Narayan, Founder & CEO of Autnhive. SAMI for AI was extremely well received by industry leaders and governments alike, all who are desperate to secure their AI systems.
All
Press Releases
White Papers
Autnhive in News
Autnhive at Global Stage
Featured Videos
Video
Loading video…
Every claim below is checkable
Ways to verify SAMI works
DEMO
Book a Demo
30 minutes with our team, walked through your own AI stack, not a canned slide deck.
Book a Demo
TEST
Try It Out
- Pen testing & DAST on your website
- Attack simulation & vulnerability assessment on exposed AI systems
- Vulnerability checks on your mobile & desktop apps
AUDIT
View Audit Evidence & Receipt
Inspect the cryptographic Merkle trail behind a finding tamper-evident, not just logged.
View Evidence
BOUNTY
Ethical Hacking Disclosure Program
Find a real gap in SAMI, report it responsibly, and get paid for it.
Join the Program
POV
Try Full SAMI (POV)
Run the complete platform against your own environment for a fixed evaluation window.
Start a POV
TALK
pan>
Contact Us
Have a question that doesn't fit the options here? Reach the team directly.
Contact UsResponsible disclosure, real recognition
Help make enterprise AI safer
Autnhive welcomes responsible AI security research that helps improve SAMI and strengthen protection across prompts, responses, RAG, agents, MCP/tool calls, sensitive data, and AI workflows.
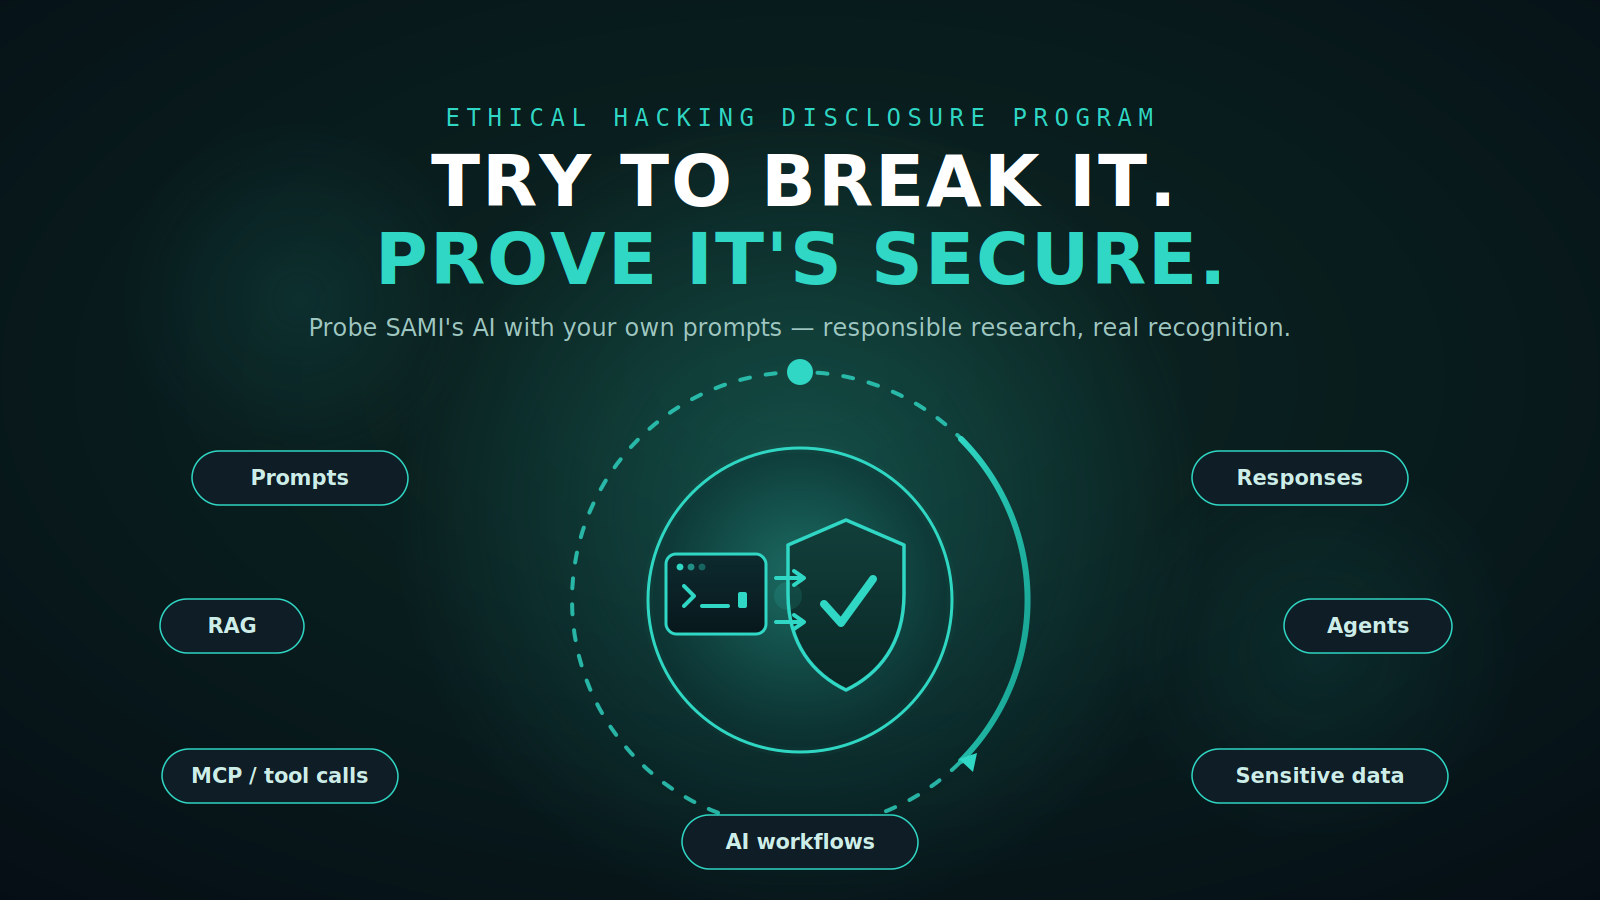
The Autnhive Ethical Hacking Disclosure Program gives security researchers a responsible path to report potential AI security findings, product issues, and proof-of-concept attacks. Our goal is to work with ethical hackers, not against them, to make enterprise AI safer for everyone.
Research areas
PROMPT / RESPONSE
Prompt and Response Security
Jailbreaks, prompt injection, unsafe responses, policy bypass attempts, and harmful output attempts.
RAG
RAG Security
RAG poisoning, unsafe retrieval, stale source influence, sensitive chunk exposure, and unauthorized data access.
AGENT / MCP
Agent and MCP Security
Agent tool misuse, unsafe tool calls, privilege escalation, unauthorized actions, and side-effect abuse.
SENSITIVE DATA
Sensitive Data Protection
PII, PHI, credentials, secrets, regulated data, and proprietary data exposure risks.
WORKFLOW
AI Workflow Security
Multi-step attack chains, chained agent behavior, workflow bypasses, and unsafe automation paths.
AUDIT / EVIDENCE
Audit and Evidence Integrity
Proof Evidence, Evidence Receipt, Proof Verified checks, event integrity, and evidence export behavior.
What a useful disclosure includes
A strong disclosure should include a clear description of the issue, steps to reproduce, affected feature or workflow, test input, observed behavior, expected behavior, screenshots or video evidence, and potential impact.
Disclosure Intake Required Fields
- Researcher name or handle
- Contact email
- Affected SAMI feature or workflow
- Description of the issue
- Steps to reproduce
- Test prompt, payload, or workflow
- Impact explanation
- Screenshots or video evidence
- Suggested remediation, if available
Responsible testing expectations
Autnhive supports responsible security research performed in good faith, within authorized testing environments, and without harm to customers, systems, data, or third parties. Researchers must not access, modify, exfiltrate, destroy, or disclose customer data. Researchers must not perform denial-of-service testing, social engineering, physical attacks, or testing against systems outside the permitted scope.
Autnhive will review valid submissions, coordinate remediation where appropriate, and provide recognition or rewards based on severity, quality, reproducibility, and impact.
⚠ LEGAL REVIEW REQUIRED this section states safe-harbor and testing-scope terms. Do not publish until legal counsel has reviewed it.
Recognition and rewards
Eligible submissions may receive recognition, reward consideration, or coordinated disclosure credit based on severity, originality, business impact, and quality of the report. Autnhive may prioritize findings that improve AI security, privacy, compliance, agent safety, RAG security, MCP/tool security, or audit evidence integrity.
Tamper-evident audit for enterprise AI
SAMI Proof Ledger
Prove what happened across AI prompts, responses, RAG access, agent actions, MCP/tool calls, CTEM findings, policy changes, administrator activity, and compliance evidence.
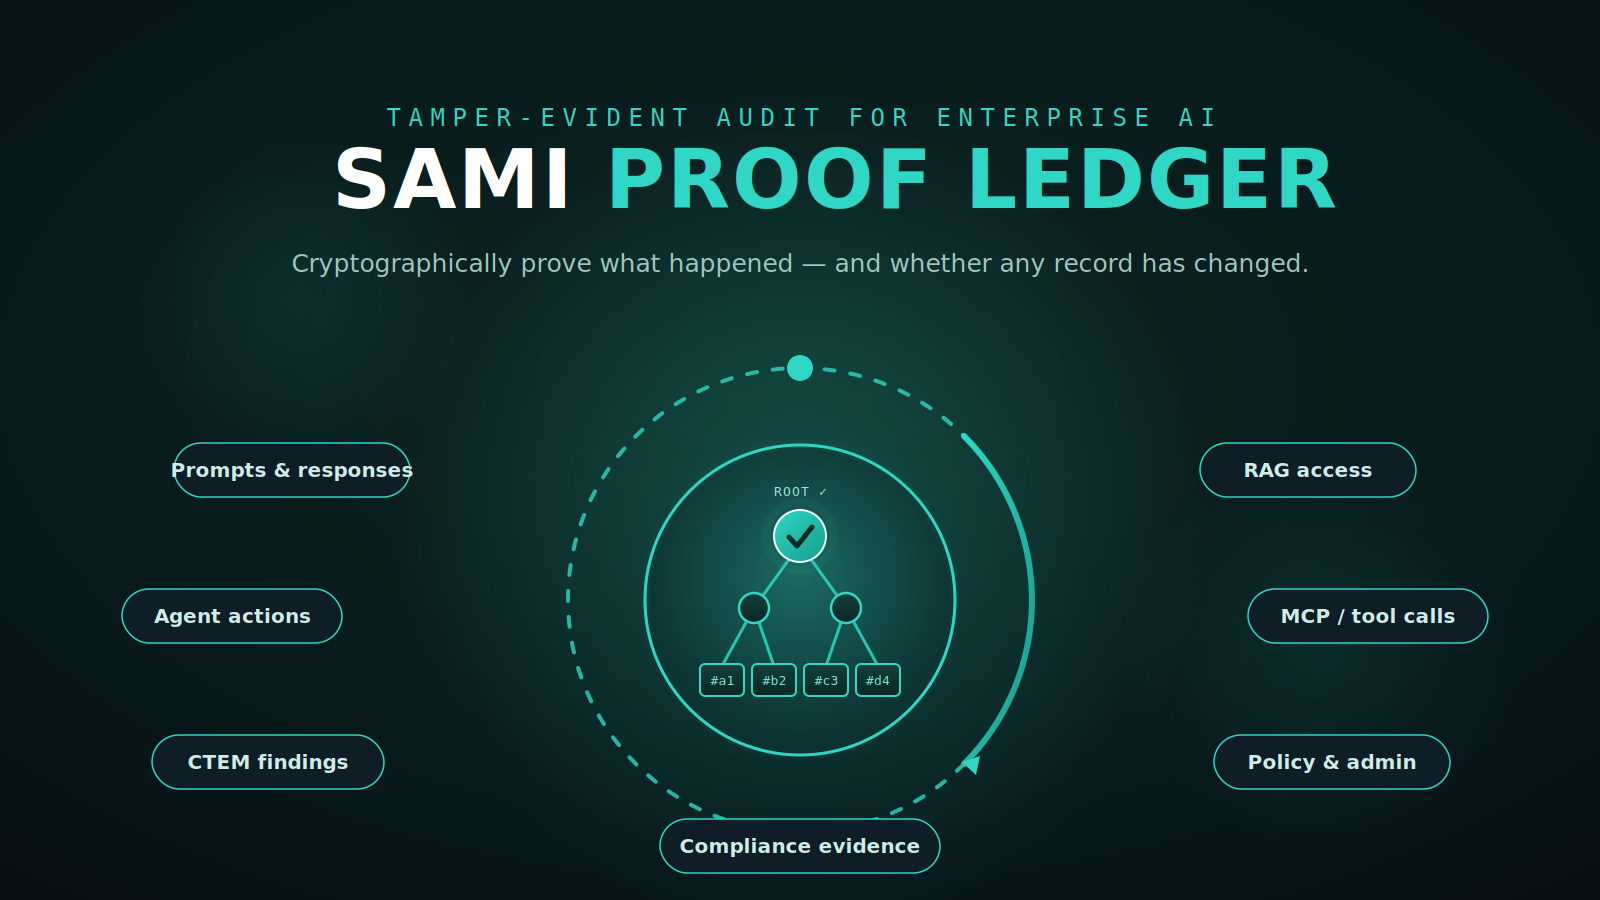
SAMI Proof Ledger creates Proof Evidence and Evidence Receipts for critical AI, security, governance, compliance, and administrative events. SAMI uses a Merkle-based process to cryptographically link important records, verify proof paths, match expected roots, validate signed checkpoints, and show whether an event record has changed.
"Workflow Intelligence shows what happened. SAMI Proof Ledger proves what happened."
Tamper-evident proof for every critical AI event
SAMI Proof Ledger records the activity that matters most across AI security, governance, compliance, and operations.
AI Firewall Decisions
Prompts, responses, allow/block/redact/escalate decisions, matched rules, policy bundles, and enforcement outcomes.
RAG Access
Documents indexed, chunks retrieved, data classification, context injection, sensitive data handling, and access decisions.
Agents and MCP Tools
Agent triggers, agent plans, tool requests, approvals, blocks, side-effect status, handoffs, and agent run completion.
CTEM Findings
AI assets discovered, exposures detected, findings created, remediation assigned, fixes completed, and re-validation passed.
Policy and Admin Changes
Guardrail updates, policy changes, role changes, permissions, sign-ins, integrations, approvals, and evidence exports.
Compliance Evidence
Control mappings, framework evidence, audit exports, SOC evidence, legal evidence, and GRC-ready proof records.
Two proof outputs. Two jobs.
Proof Evidence gives analysts a quick in-product view that an event is verified and unchanged. Evidence Receipt gives auditors, compliance, legal, and investigators a portable proof package.
| Output | Purpose | Audience |
|---|---|---|
| Proof Evidence | Quick in-product verification | SOC teams, analysts, admins, developers, AI governance teams |
| Evidence Receipt | Full audit-ready proof package | Auditors, compliance, legal, CISOs, regulators, customers, investigators |
Sample · Try It Out preview
Agent Tool Misuse Blocked
An AI agent attempted to run a high-risk shell command. SAMI blocked the action, enforced the decision, confirmed no side effect occurred, and generated Proof Evidence and an Evidence Receipt.
Proof Verified
Nothing changed
- Event fingerprint recomputed
- Event fingerprint matches original
- Hash chain verified
- Proof path verified
- Batch root verified
- Signed checkpoint verified
Proof Verified means nothing changed
When SAMI shows Proof Verified, SAMI has recomputed the event fingerprint, verified the event chain, verified the proof path, matched the expected root, and validated the signed checkpoint. If the event was changed, removed, reordered, or replaced, the proof would fail.
- Event fingerprint recomputed
- Event fingerprint matches original
- Hash chain verified
- Proof path verified
- Batch root verified
- Signed checkpoint verified
- Evidence archive synced
Share evidence without exposing sensitive data
Evidence Receipts can include redacted values, payload fingerprints, policy hashes, proof checks, and verification results instead of raw prompts, responses, PHI, PII, secrets, or confidential business data. This allows customers to prove integrity without unnecessarily exposing private information.
Validate SAMI claims through Try It Out, video evidence, whitepapers, and POV
Autnhive is transparent about SAMI's capabilities. Customers can validate SAMI through the Try It Out experience, video evidence of live SAMI protections, whitepapers with real attack examples, sample Evidence Receipts, and a full customer proof of value.
Use cases for tamper-evident AI audit
AI Incident Investigation
Reconstruct prompts, model calls, RAG access, agent actions, and proof status.
Regulatory Audit
Audit-ready evidence showing what happened, which policy was active, and whether the record changed.
SOC 2 Evidence
Control evidence, access reviews, admin changes, and proof that evidence remains unchanged.
Legal & Forensic Review
Event fingerprints, proof paths, signed checkpoints, and chain-of-custody records.
Customer Assurance
Share redacted Evidence Receipts to prove AI security, privacy, and governance controls.
CTEM Remediation Proof
When an exposure was discovered, assigned, fixed, re-tested, and verified.
AI Agent Audit
What triggered an agent, what it planned, what SAMI allowed or blocked, and any side effect.
RAG Data Provenance
Which documents were retrieved and whether the AI answer used approved sources.
SAMI FAQ
Straight answers about AI security, AI CTEM, Workflow Intelligence, Evidence Gap Assessment, Proof Ledger, remediation, compliance, and governance.
Browse by topic
All categories
All categories
Search results
Trust & Compliance
EU AI Act Article 9 requires proof.
SAMI keeps that proof live.
Article 9 of the EU AI Act requires documented, lifecycle risk management for high-risk AI systems, evidence that risks are identified, monitored, mitigated, and reviewed over time. SAMI automates the evidence trail from day one: risk events, decisions, remediation actions, and audit-ready exports.
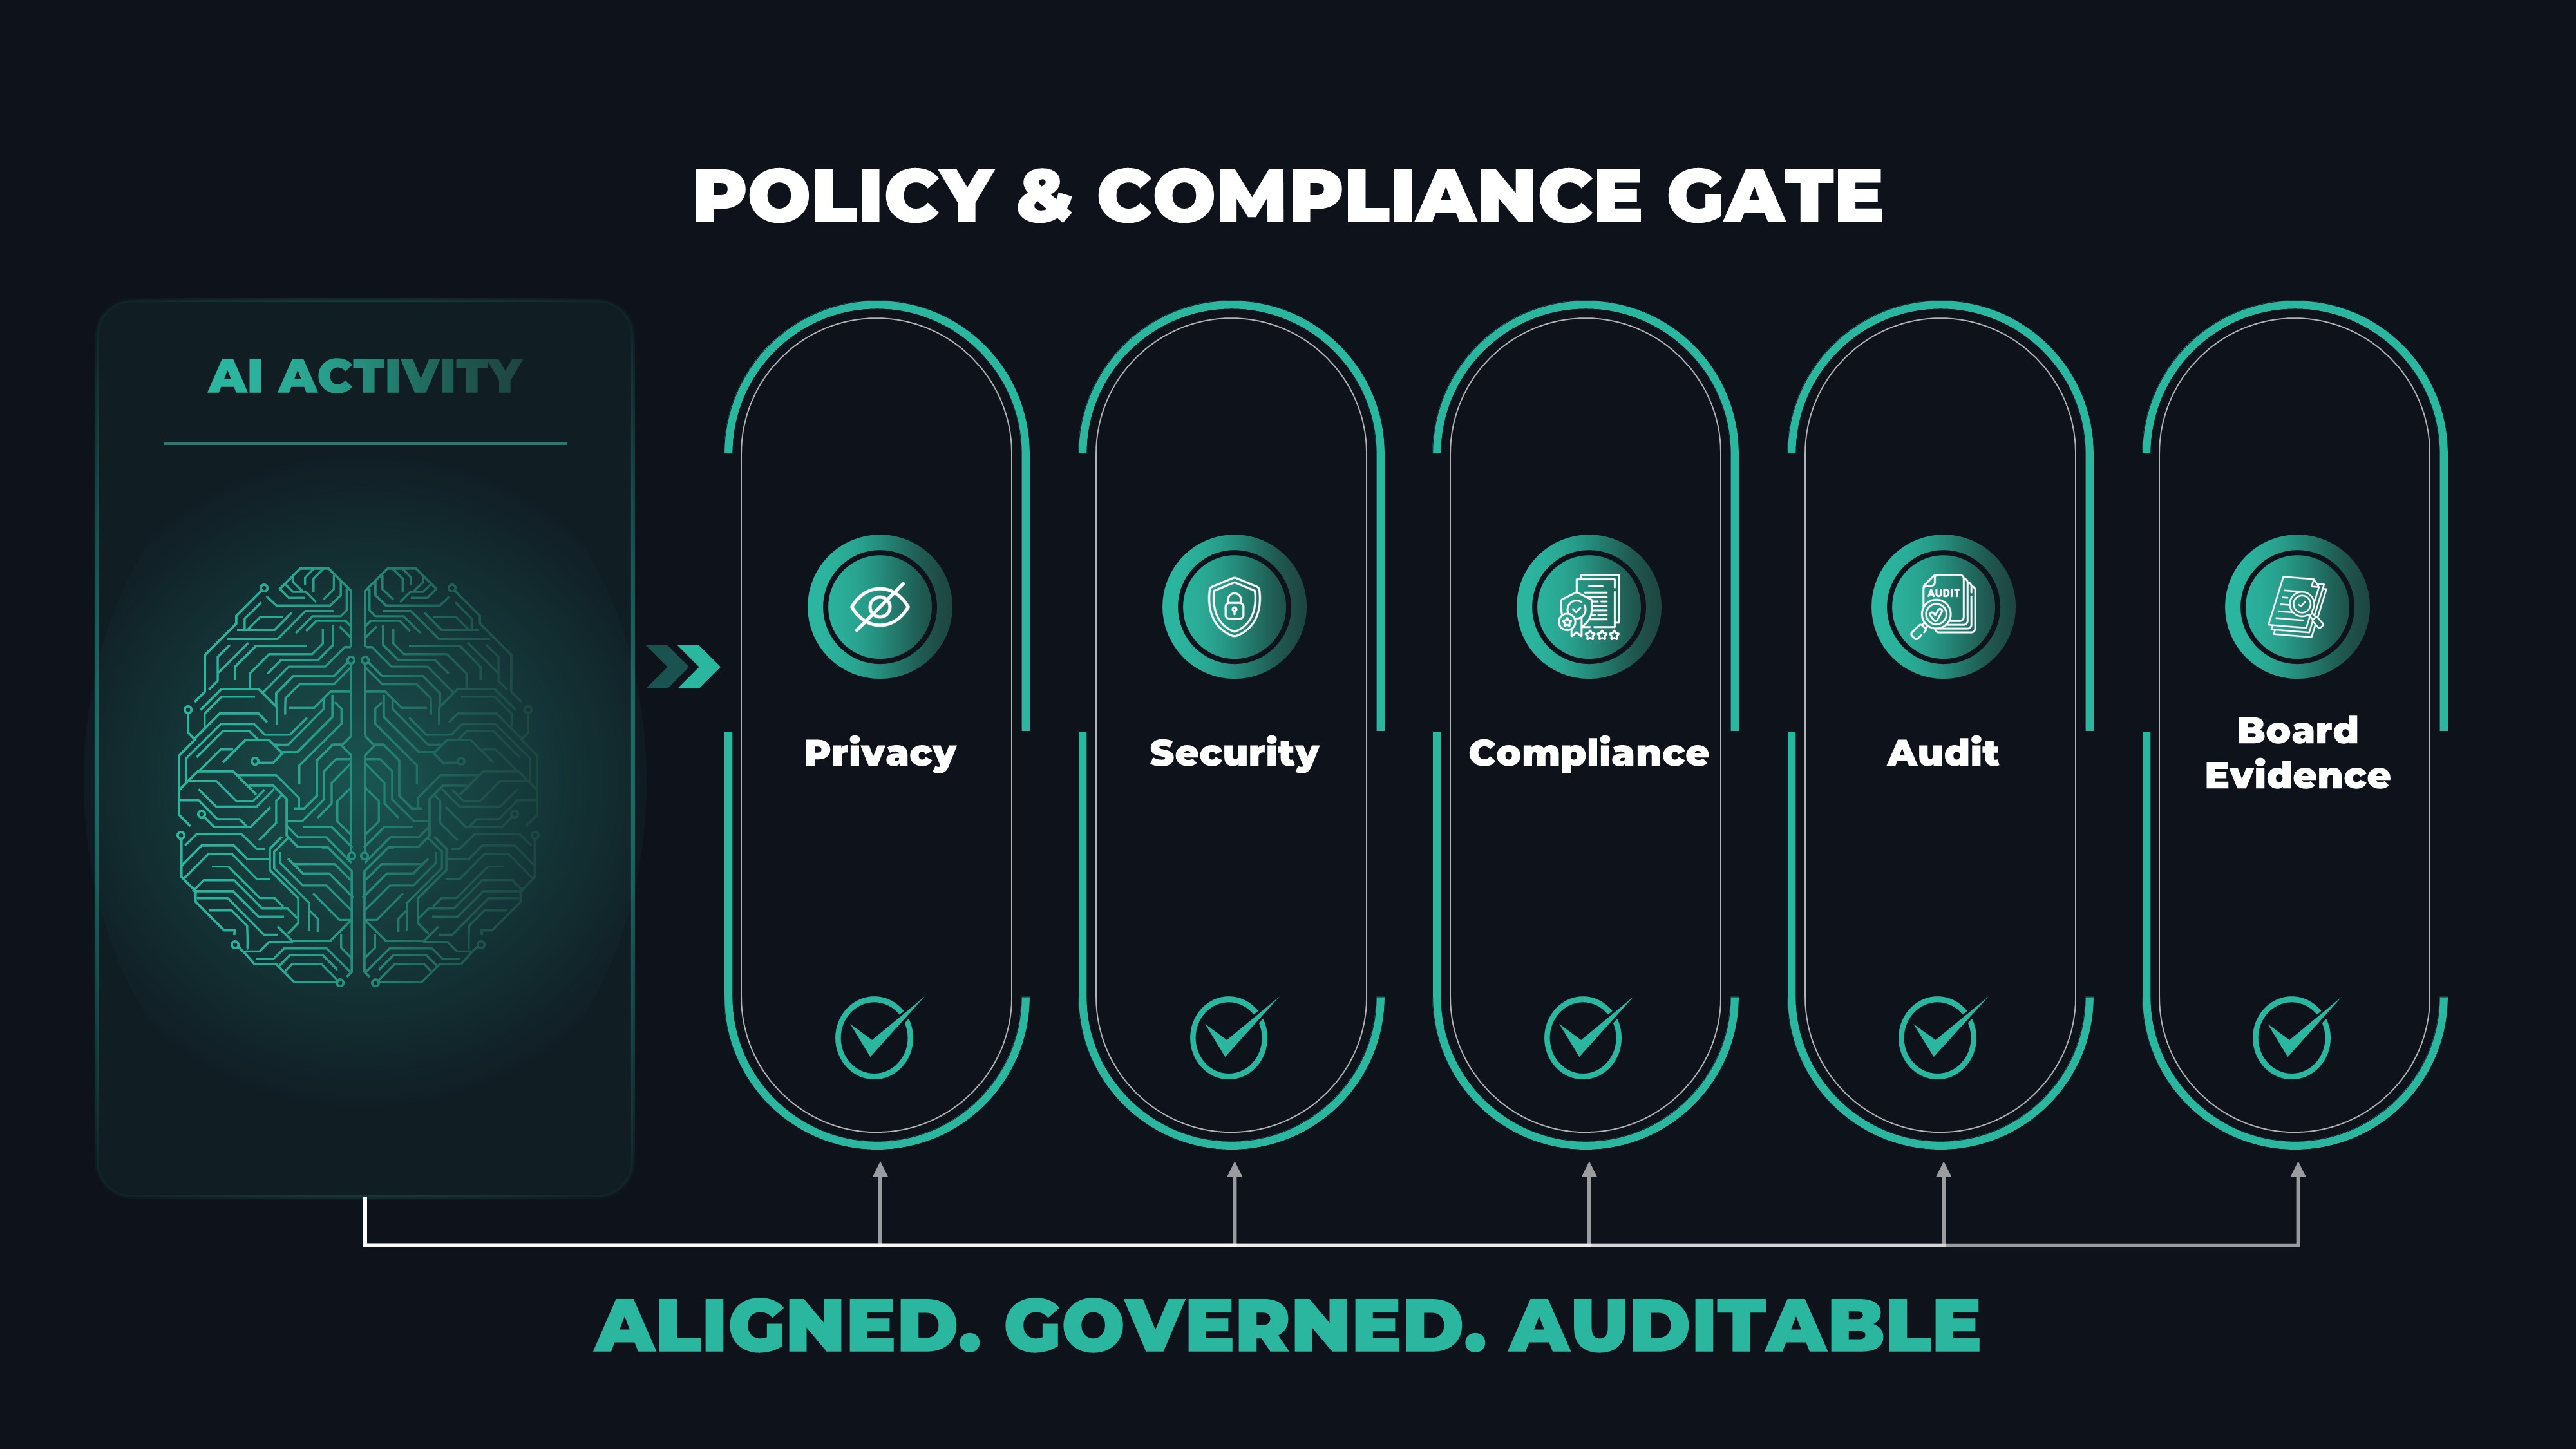
EU AI Act · Article 9
"If the EU AI Office audited your high-risk AI systems tomorrow, do you have documented continuous risk management evidence ready to produce?"
HIPAA + AI · OCR Guidance
"Which AI systems in your environment are processing protected health information and can you prove that PHI is never stored unencrypted in model context?"
Regulatory Clocks
The regulations that
require SAMI.
Every one of these frameworks requires documented, continuous AI risk management. Manual spreadsheets fail all of them.
🇪🇺
EU AI Act - Phased Enforcement
First fine already issued: €8.4M · March 2026
Regulation (EU) 2024/1689 is in force and applies in phases, with most high-risk AI obligations applying from August 2026.. Articles 9 (risk management), 13 (transparency), and 17 (quality management) require documented, continuous monitoring for every high-risk AI system. Enforcement risk is evidence-based: organizations should maintain documented lifecycle risk management, testing, monitoring, incident handling, and governance records. Penalties can reach €35M or 7% of worldwide annual turnover for prohibited AI practices, and €15M or 3% for many operator obligations.
✓ SAMI automates Art.9 risk management, Art.13 transparency logs, Art.17 QMS proof continuously
🇺🇸
Colorado AI Act (SB 205)
Active Since 1 Feb 2026
Risk management obligations, bias audits, and consumer disclosures for high-risk AI systems. Template legislation being adopted by 8+ US states. SAMI's continuous monitoring and gap analysis maps to all SB 205 obligations automatically.
✓ SAMI generates SB 205 compliance evidence automatically · Risk analysis on every assessment
SEC Cybersecurity Rule
Active Since 2023
Material AI cyber incidents must be disclosed within 4 business days (17 CFR §229.106). AI risk must be detailed in annual 10-K filings. SAMI generates 10-K-ready AI risk documentation and flags material incidents in real time.
✓ SAMI auto-generates 10-K AI risk documentation · Material incident alert within minutes
HIPAA + AI (OCR Guidance)
Actively Enforced
HHS OCR confirmed AI systems processing PHI are subject to full HIPAA Technical Safeguards. HIPAA civil penalties are inflation-adjusted and can reach multi-million-dollar annual caps. SAMI tokenizes PHI before any AI model processes it PHI never appears in model context, logs, or outputs.
✓ PHI tokenization pre-model · Supports HIPAA Technical Safeguards with audit controls, access evidence, and PHI protection · BAA available
FTC Section 5
Active Now
Already enforcing. No new law required. AI-specific guidance in force since 2023. Deceptive AI outputs constitute an unfair commercial practice. SAMI prevents unauthorized and hallucinated outputs at the model boundary before users see them.
✓ SAMI AI Firewall intercepts outbound responses · Prevents deceptive outputs before delivery
US AI Litigation
No Deadline
Courts are establishing the standard of care for AI right now. Air Canada liability ruling (2024) has been cited in 3 subsequent cases establishing that organizations are responsible for AI outputs. Without documented, continuous monitoring, every AI incident is a liability event.
✓ SAMI provides legal-grade audit trail · Continuous documented monitoring · Evidence on demand
Compliance Coverage Matrix
How SAMI covers
every framework.
| Regulation | Actual Requirements | Explanation | SAMI Coverage |
|---|---|---|---|
| EU AI Act Article 9 | Article 9 requires providers of high-risk AI systems to establish, implement, document, and maintain a continuous risk management system throughout the entire AI lifecycle. | Requires organizations to continuously manage and monitor AI risks instead of treating risk assessment as a one-time activity. The regulation expects measurable governance and evidence of ongoing risk control. | HIVE CTEM provides the continuous risk management loop, documented, maintained,auditable. Board PDF auto-generated. |
| EU AI Act Article 13 | Article 13 requires high-risk AI systems to be designed and developed with sufficient transparency to enable users to interpret outputs and use the system appropriately. | Requires organizations to ensure users and auditors can understand how AI systems function, how outputs are generated, and how decisions can be traced for governance and compliance purposes. | Workflow Intelligence provides transparency and traceability for every high-risk AI interaction. |
| GDPR Article 25 | Article 25 requires Data Protection by Design and by Default, ensuring appropriate technical and organizational measures are implemented to protect personal data during processing. | Requires privacy and security controls to be embedded directly into systems and AI workflows so that unnecessary personal data exposure is prevented by default. | L05 tokenizes PII before model contact, the model never processes real personal data. Structural, not detection policy. |
| GDPR Article 30 | Article 30 requires Records of Processing Activities (ROPA), including purposes, categories, transfers, recipients, retention periods, and safeguards related to personal data processing. | Requires organizations to maintain auditable records showing how personal data is processed, accessed, transferred, retained, and secured across systems and workflows. | Workflow Intelligence provides detailed audit trails of AI interactions, including data access events, applied policies, workflow activities, and processing evidence that support GDPR Article 30 record-keeping and audit requirements. |
| GDPR Article 32 | Article 32 requires controllers and processors to implement appropriate technical and organizational measures to ensure a level of security appropriate to the risk associated with processing personal data. | Requires organizations to implement risk-based cybersecurity and privacy controls to protect personal data against unauthorized access, loss, alteration, or disclosure. | Live layers L01–L05 plus CTEM evidence of continuous risk management.(Physical not applicable, however, Logical Controls are implemented) Technical and Organizational Measures (TOM) |
| HIPAA 45 CFR 164.312(b) | HIPAA 45 CFR 164.312(b) requires implementation of hardware, software, and procedural mechanisms that record and examine activity in systems containing electronic protected health information (ePHI). | Requires healthcare organizations and service providers to maintain audit trails and monitoring capabilities for systems handling protected health information. | L05 ensures PHI never enters model context or logs. Workflow Intelligence provides the required access log. |
| OWASP LLM Top 10 2025 | OWASP LLM Top 10 identifies the most critical security risks affecting Large Language Model (LLM) applications and AI systems. | Provides practical security guidance for securing AI and LLM applications against emerging threats, misuse, and adversarial attacks. | All ten vectors addressed across SAMI's five live security layers. Framework auto-mapping per guardrail. |
| NIST AI RMF | The NIST AI Risk Management Framework provides guidance for managing risks associated with trustworthy AI systems throughout their lifecycle. | Helps organizations establish structured governance and risk management processes for developing, deploying, and operating trustworthy AI systems. | Framework auto-mapping in TrustGuard. Gap analysis identifies obligations not yet covered. |
| ISO 42001 | ISO/IEC 42001 specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS). | Provides a formal management system framework for governing AI systems responsibly, securely, and compliantly within organizations. | Guardrail inventory, decision history, framework mappings, and risk scores in regulatory-grade exports. |
| SEC Cybersecurity Rules | SEC Cybersecurity Rules require public companies to disclose material cybersecurity incidents and describe cybersecurity risk management, governance, and oversight practices. | Requires publicly traded organizations to demonstrate executive and board-level cybersecurity governance and timely reporting of material cyber incidents. | Structured AI incident records showing what happened, what data/tool was involved, and what control action occurred. |
| NYDFS 23 NYCRR 500 | NYDFS Part 500 requires covered financial institutions to establish and maintain a cybersecurity program designed to protect information systems and nonpublic information. | Establishes mandatory cybersecurity requirements for financial institutions operating under the New York Department of Financial Services. | AI activity audit trail, risk assessments, vulnerability management, and incident response evidence. |
| FTC Safeguards Rule | The FTC Safeguards Rule requires financial institutions to develop, implement, and maintain a comprehensive information security program to protect customer information. | Requires organizations handling consumer financial information to implement safeguards protecting confidentiality and integrity of customer data. | AI workflow risk assessment, remediation tracking, control evidence, and service/vendor AI workflow review. |
| PIPEDA (Canada) | PIPEDA requires organizations to protect personal information through appropriate security safeguards and obtain meaningful consent for collection, use, and disclosure of personal data. | Governs how private-sector organizations in Canada collect, use, disclose, and protect personal information. | Workflow evidence of personal-data protection in AI workflows. CTEM maps personal-data exposure. |
| Privacy Act / APP 11 (Australia) | APP 11 requires organizations to take reasonable steps to protect personal information from misuse, interference, loss, unauthorized access, modification, or disclosure. | Requires organizations in Australia to safeguard personal information using reasonable security measures throughout the data lifecycle. | Runtime data controls plus CTEM evidence of AI personal-information exposure management. |
| SOCI Act (Australia) | The Security of Critical Infrastructure (SOCI) Act requires operators of critical infrastructure assets to manage and report cyber risks affecting essential services. | Strengthens cybersecurity and resilience requirements for organizations operating critical national infrastructure in Australia. | Runtime controls and CTEM evidence for AI workflows affecting critical infrastructure. |
| Saudi PDPL | The Saudi Personal Data Protection Law (PDPL) regulates the processing of personal data and requires organizations to protect privacy rights and secure personal information. | Establishes privacy and data protection obligations for organizations processing personal data within Saudi Arabia.PDPL also includes consent, lawful basis, rights, and international transfer obligations. | Personal-data controls in AI prompts, responses, RAG, agents, and MCP/tool calls. Workflow evidence. |
| UAE PDPL | The UAE Personal Data Protection Law (PDPL) establishes requirements for lawful processing, protection, and transfer of personal data within the UAE. | Provides a national privacy framework governing the collection, use, storage, and protection of personal data in the UAE. | Workflow evidence showing what data was touched, what policy applied, and how exposure was reduced. |
| Japan APPI | The Act on the Protection of Personal Information (APPI) requires businesses to properly handle and protect personal information while respecting individual privacy rights. | Governs personal data protection and privacy obligations for organizations operating in Japan. | Runtime controls and Workflow Intelligence audit trail for AI systems processing Japanese personal data. |
| DORA (EU) | The Digital Operational Resilience Act (DORA) requires financial entities to ensure ICT operational resilience and manage cyber risks affecting financial services. | Strengthens operational resilience and cybersecurity requirements for financial institutions and ICT providers across the EU. | Resilience testing via attack simulation, third-party AI workflow evidence, re-validation, and incident response. |
| NIS2 Article 21 | Article 21 of the NIS2 Directive requires essential and important entities to implement appropriate and proportionate cybersecurity risk management measures. | Requires organizations operating critical or important services in the EU to implement strong cybersecurity and resilience measures. | AI asset discovery, vulnerability validation, incident evidence, remediation prioritisation, and audit records. |
| EU AI Act Article99 penalty | Article 99 establishes penalties and administrative fines for non-compliance with obligations under the EU AI Act. | Defines the financial and regulatory consequences for organizations failing to comply with EU AI Act requirements, including significant monetary penalties for high-risk violations. | €35M or 7% of global annual turnover for the most Prohibited Practices.€15M or 3% for most operator obligations. |
By Industry
Your industry.
Your regulations.
Healthcare
HIPAA
ISO 27001
EU AI Act (medical AI)
GDPR Art.25
PHI tokenization, medical AI compliance, HIPAA Technical Safeguards, clinical AI audit trails. BAA available.
Financial Services
SEC 17 CFR §229.106
FTC Section 5
EU AI Act (high-risk)
SOC 2 Type II
SEC disclosure automation, FTC AI compliance, financial model protection, insider threat via AI agents, board-ready P95 liability model.
Government & Defense
Zero Telemetry Mode
Air-Gap Deployment
NIST SP 800-207
MITRE ATLAS
Zero telemetry, air-gap, classified environments. ICS/SCADA security (27+ protocols). Nation-state AI attack detection.
Education
GDPR / FERPA
COPPA (student data)
ISO 27001
Student data protection, AI tutoring security, M365/Teams for Education, COPPA-compliant AI deployment. Reference customer: Peel District School Board.
Critical Infrastructure
IEC 62443
NIST SP 800-82
CISA Guidelines
OT/ICS/SCADA security (27+ protocols), IEC 62443 compliance, passive-first assessment, air-gap deployment for plant floor environments.
Retail & E-Commerce
PCI-DSS
GDPR Art.25
FTC Section 5
Customer AI chatbot security, PCI-DSS Req.11 continuous testing, WAF validation against ecommerce bypass patterns, Air Canada-type liability prevention.
Trust & Compliance
Our pursuit of excellence is measured by trust.
SAMI helps organizations align AI security, privacy, and governance with the certifications, frameworks, and compliance expectations required by customers, auditors, regulators, and enterprise buyers.
Certifications
Certifications by SAMI
your team looks for.
SAMI holds, or continuously monitors against, major security, privacy, and AI governance framework. Evidence packages available on request.
ISO 27001
Information Security Mgmt
SAMI is ISO 27001:2022 certified across all scopes platform development, cloud operations, customer data handling, and incident management. Annual surveillance audits with zero findings to date. Certificate available on NDA.
SAMI Coverage
Annex A controls automated where applicable. Continuous monitoring closes the gap between annual audits. Evidence export on demand.
SOC 2 Type II
Security · Availability · Confidentiality · Processing Integrity
SAMI completed SOC 2 Type II Attestation across Security, Availability, Confidentiality, and Processing Integrity Trust Service Criteria. Full report available under NDA to qualified prospects.
SAMI Coverage
SOC 2 controls evidenced continuously. SAMI's own audit logging covers the CC6, CC7, CC8, and CC9 criteria automatically.
ISO 42001:2023
AI Management System
Readiness Support
SAMI supports ISO/IEC 42001 readiness by helping organizations document AI management system activities, monitor AI risks and export supporting evidence for internal governance and assessment preparation.
SAMI Coverage
SAMI supports ISO/IEC 42001 readiness by helping teams maintain AI management system evidence.
🇪🇺
GDPR
EU Data Protection Regulation
SAMI is GDPR compliant across all processing activities. Article 25 (data protection by design) is satisfied through tokenization PII is replaced before AI processing and rehydrated in outputs. DPA available for all customers. Data residency options available.
SAMI Coverage
SAMI's tokenization layer satisfies Art.25. Continuous monitoring generates Art.30 Records of Processing Activities automatically. DPA available on request.
HIPAA
Health Insurance Portability Act
SAMI is HIPAA-ready with Business Associate Agreement (BAA) available for covered entities and business associates. PHI tokenization ensures AI models process tokens only PHI never appears in model context or outputs. Technical Safeguards satisfied by design.
SAMI Coverage
PHI tokenization pre-model. BAA available. Audit logs for all PHI access events. Technical Safeguard evidence generated automatically.
🇺🇸
NIST AI RMF
AI Risk Management Framework
SAMI helps organizations prepare for NIST AI RMF adoption by supporting evidence collection across the four AI RMF functions: Govern, Map, Measure, and Manage. SAMI provides policy enforcement evidence, AI system discovery, risk scoring through SAMI BRI/SPI metrics, remediation tracking, and exportable documentation for internal governance review.
SAMI Coverage
Govern: policy enforcement evidence · Map: AI system discovery · Measure: SAMI BRI/SPI scoring · Manage: remediation tracking · Evidence export for governance review.
PCI DSS v4.0.1
Payment Card Industry Data Security Standard
Evidence Support
SAMI helps organizations prepare evidence for PCI DSS v4.0.1 review by supporting application-security testing, WAF and AI Firewall validation, vulnerability assessment evidence, wireless access point assessment support where in scope, and penetration-testing documentation. Evidence packages can support internal reviews and QSA assessment workflows.
SAMI Coverage
Req. 6: application-security evidence support · Req. 6.4.2: public-facing web application protection evidence · Req. 11.2: wireless access point assessment support · Req. 11.3: vulnerability scanning evidence · Req. 11.4: penetration-testing documentation
OWASP LLM Top 10
AI Security Framework
SAMI provides defense against all 10 OWASP LLM Top 10 categories: LLM01 Prompt Injection, LLM02 Insecure Output Handling, LLM03 RAG Poisoning, LLM04 Model DoS, LLM05 Supply Chain, LLM06 Data Disclosure, LLM07 Insecure Plugin Design, LLM08 Agent Hijacking, LLM09 Overreliance, LLM10 Model Theft. Coverage rates published quarterly.
SAMI Coverage
100% OWASP LLM Top 10 coverage across 9 security layers. Quarterly coverage reports published. OWASP IDs tagged on every SOC incident.
MITRE ATLAS
AI Adversarial Threat Landscape
SAMI maps to MITRE ATLAS the AI-specific adversarial threat framework. Unlike MITRE ATT&CK (designed for traditional infrastructure), ATLAS covers AI-native attack techniques. SAMI's attack simulation uses ATLAS technique IDs so your SOC team has consistent taxonomy.
SAMI Coverage
All current ATLAS v4 techniques mapped to SAMI defenses. Technique IDs included in every incident alert and assessment report.
EU AI Act
Regulation (EU) 2024/1689
Evidence Support
SAMI supports EU AI Act readiness by helping organizations monitor AI systems, collect evidence, document risks, maintain transparency logs, and export structured records for internal governance and legal review. SAMI can support documentation workflows related to Article 9 risk management, Article 13 transparency, Article 17 quality management evidence, and applicable GPAI documentation needs under Articles 53–55.
SAMI Coverage
Art.9 risk documentation support · Art. 13: transparency and usage logs · Art. 17: quality-management evidence support · Art. 53–55: GPAI documentation support where applicable · Evidence export for internal review.
Zero Trust
Architecture Validation
Evidence Support
SAMI applies inspection and policy enforcement at the AI model boundary for prompts, retrieval, and agent actions. It is designed to reduce implicit trust in retrieved content, user inputs, system prompts, identities, and agent actions. SAMI supports Zero Trust architecture principles described in NIST SP 800-207. SAMI does not require special network access or trust relationships to operate.
SAMI Coverage
AI interaction inspection at the model boundary · Policy enforcement for prompts, retrieval, and agent actions · Reduced implicit trust in retrieved content, user input, and system prompts · Evidence support for internal Zero Trust reviews.
Air-Gap / Zero Telemetry
Classified Environments
SAMI's Fully Private Zero Telemetry mode sends absolutely nothing to Autnhive. Designed for classified government, defense, nuclear, and high-security financial environments. Full platform capability all 9 security layers with zero external dependencies or data egress.
SAMI Coverage
Zero telemetry mode: fully on-premises. Air-gap deployment: supported. Classified environments: available. Three privacy modes: Fully Private, Audit, Full Retention.
US
CCPA/CPRA
California Consumer Privacy Act / California Privacy Rights Act
Autnhive is Compliant with CCPA and CPRA requirements, SAMI supports compliance with CCPA and CPRA requirements for the collection, processing, retention, and protection of personal information. Privacy-by-design controls, data minimization, access controls, and tokenization help protect personal information throughout AI-enabled workflows. Customer data processing terms are available, and organizations can support consumer rights requests, including access, deletion, correction, and data portability.
SAMI Coverage
SAMI's tokenization layer reduces exposure of personal information by replacing sensitive data before AI processing and rehydrating only authorized outputs. Continuous monitoring and audit logging provide evidence of data processing activities, access events, and remediation actions.
AutnHive/SAMI supports readiness, monitoring, evidence collection, and control-mapping workflows. It does not claim certification, legal compliance, regulatory approval, or third-party validation for the frameworks listed unless separately confirmed in a signed assessment or validation report.
Legal
Legal &
Privacy Centre.
All legal documents governing your use of SAMI and Autnhive services. We publish these in full because trust requires transparency not because lawyers said we had to. For questions, requests, or DPA/BAA: info@autnhive.com
Master Use Agreement
Terms of Service
Privacy Policy
Cookie Policy
Security Policy
This Master Use Agreement ("Agreement") is entered into by and between Autnhive Corporation ("Autnhive"), and the Customer identified in the applicable Order Form ("Customer"). Each of Autnhive and Customer may be referred to individually as a "Party" and collectively as the "Parties."
1. DEFINITIONS
The following terms shall have the meanings set forth below:
- "SAMI Platform" means Autnhive’s Secure Assessment, Testing, Simulating, Analytics, and Monitoring Intelligence platform, including all associated software, systems, configurations, threat assessment modules, business impact analysis tools, third-party vendor assessment functions, penetration testing and attack simulation capabilities, artificial intelligence engines, data ingestion and intelligence analytics features, as well as any updates, enhancements, documentation, or related technology provided by Autnhive.
- "Customer Data" means data provided or made available by Customer, or collected from Customer's systems, networks, or infrastructure by Autnhive in the performance of the Services.
- "Derived Data" means any data, metadata, analysis, intelligence, models, reports, conclusions, risk profiles, vulnerabilities, threat information, or liability-related assessments that are generated, inferred, or derived by the SAMI Platform or by Autnhive in the course of performing the Services, including through the processing or analysis of Customer Data or other inputs provided by or accessed from Customer.
- "Deliverables" means any reports, analyses, risk assessments, simulation results, third-party vendor reviews, threat intelligence briefs, documentation, or other materials provided to Customer.
- "Order Form" or "SOW" means any ordering document or statement of work that sets forth the scope of Services to be provided by Autnhive and that is executed by the Parties either in writing, electronically through digital signature, or by Customer's affirmative acceptance via an “I Agree” or “Agree to Terms and Conditions” button.
- "Services" means all activities performed by Autnhive or its authorized subcontractors or third-party service providers under this Agreement or any applicable Order Form or SOW.
- "Confidential Information" means any non-public, proprietary, business, technical, financial, operational, strategic, or other information disclosed by one Party to the other.
2. LICENSE AND RESTRICTIONS
License Grant. Autnhive grants Customer a limited, non-exclusive, non-transferable right to access and use the SAMI Platform and Deliverables for internal business purposes, subject to the terms of this Agreement.
Restrictions. Customer shall not:
- (a) sublicense, resell, or distribute the Platform;
- (b) reverse engineer, decompile, disassemble, or create derivative works;
- (c) use the Services to build or improve a competing product;
- (d) exceed usage limitations specified in the SOW;
- (e) alter or obscure any proprietary notices or branding unless expressly permitted;
- (f) use the SAMI Platform, or any data, output, or insight derived from it, in any manner intended to cause harm or adverse impact to any individual, organization, system, or third party;
- (g) conduct or initiate any assessments, testing, or simulations on any third party without prior written approval;
- (h) fail to implement and maintain appropriate internal safeguards, access controls, and monitoring procedures.
3. SERVICES AND ACCESS
Service Delivery. Autnhive shall provide the Services and access to the SAMI Platform using commercially reasonable efforts, skill, and diligence, and in accordance with the applicable Order Form or SOW.
Customer Responsibilities and Access. Customer shall provide Autnhive with timely access to all environments, credentials, interfaces, APIs, personnel, documentation, and resources necessary to enable Autnhive to perform the Services effectively.
Simulations and Testing. By requesting penetration tests, threat simulations, business impact analyses, or exploit emulations, Customer affirms and accepts full responsibility for initiating such assessments and confirms that it is duly authorized to allow such actions on the applicable systems.
Third-Party Authorizations. Where Testing Services are to be performed on third-party vendors or systems, Customer warrants and guarantees that it has obtained prior written authorization from a duly authorized representative of such third party.
Use and Disclosure Limitations. Customer agrees to use all information, Deliverables, or outputs resulting from Risk Assessments, Testing Services, Liability Analysis, and Compliance activities solely for internal security improvement, governance, or risk mitigation purposes.
4. DATA OWNERSHIP AND RIGHTS
Customer Data. Customer retains all right, title, and interest in and to all Customer Data. Autnhive shall access, use, or process Customer Data solely as necessary to provide the Services, fulfill its obligations under this Agreement, or as required by applicable law. Autnhive shall not disclose Customer Data to any third party without Customer’s prior written consent, except as required by law.
Autnhive may use data derived from the operation of the SAMI Platform in aggregated and anonymized form solely for internal purposes such as improving system performance, ensuring service reliability, or identifying general usage trends, provided such use does not include any identifiable or confidential Customer Data and complies with applicable data protection laws.
The following ownership and usage rights apply:
- Derived Data. Autnhive owns all Derived Data. Customer is granted a perpetual, non-exclusive license to use such Derived Data solely for its internal governance, risk, and compliance purposes.
- Third-Party Assessment Data. All data generated from assessments of third-party vendors belongs to Autnhive. Customer is granted a broad license to use such results for internal evaluation, compliance reporting, and audits.
- Deletion. Upon written request and within thirty (30) days after termination, Autnhive shall delete Customer Data unless legally required to retain it. Autnhive may retain anonymized, aggregated insights.
5. SECURITY AND COMPLIANCE
Security Program. Autnhive shall maintain administrative, technical, and physical safeguards in accordance with industry best practices (e.g., ISO 27001, HIPAA, GDPR, etc.).
6. CONFIDENTIALITY
Each Party agrees to maintain the confidentiality of information disclosed under this Agreement and to use such information solely as necessary to perform its obligations or exercise its rights.
The Receiving Party shall:
- Protect Confidential Information using at least reasonable care and no less than the care used to protect its own confidential information.
- Disclose Confidential Information only to employees, contractors, and professional advisors with a legitimate need to know and who are bound by comparable confidentiality obligations.
- Provide prompt written notice, where legally permissible, if compelled by law to disclose Confidential Information.
Confidential Information does not include information that:
- (a) is or becomes publicly available through no breach of this Agreement;
- (b) was lawfully known to the Receiving Party before disclosure;
- (c) is received from a third party with the legal right to disclose it; or
- (d) is independently developed without reference to the Disclosing Party’s Confidential Information.
The obligations in this Section survive for three (3) years following termination or expiration of this Agreement, except for trade secrets or information entitled to longer protection under applicable law.
7. INTELLECTUAL PROPERTY
Ownership. All right, title, and interest in and to the Autnhive Platform and related Intellectual Property shall remain exclusively owned by Autnhive, its licensors, or affiliates.
Customer shall not:
- (a) use Autnhive Intellectual Property outside the scope of this Agreement;
- (b) claim ownership of any Platform enhancements, modifications, or documentation;
- (c) reproduce, distribute, modify, or disclose Autnhive Materials without prior written consent.
Additional Intellectual Property provisions:
- Branding and White-Labeling. Any use of Autnhive trademarks, logos, or branding elements requires prior written consent and does not grant ownership rights.
- Feedback. Autnhive may freely use, incorporate, and exploit any feedback, suggestions, or enhancement requests provided by Customer without compensation.
- Autnhive Materials. Documents, reports, analyses, white papers, and similar materials created by Autnhive remain the sole intellectual property of Autnhive.
8. FEES AND PAYMENT
Customer shall pay all fees specified in the applicable Order Form or Statement of Work (SOW).
- Fees. All fees are non-cancelable and non-refundable unless expressly stated otherwise.
- Invoicing and Payment Terms. Undisputed invoices are due within thirty (30) days of the invoice date.
- Late Payments. Overdue undisputed amounts may be subject to interest or late fees as permitted by law.
- Taxes. Customer is responsible for all applicable taxes, duties, and charges other than taxes based on Autnhive’s net income.
9. WARRANTIES AND DISCLAIMERS
The Parties acknowledge and agree to the following warranties and disclaimers.
- Mutual Representations. Each Party represents and warrants that it has the full power and authority to enter into and perform its obligations under this Agreement, and that doing so does not and will not violate any other agreement or legal obligation to which it is a party.
- Limited Service Warranty. Autnhive warrants that the Services will be performed in a professional and workmanlike manner consistent with generally accepted industry standards. If Customer notifies Autnhive in writing of a material breach of this warranty within thirty (30) days of delivery of the affected Services, Autnhive will, at its sole discretion, re-perform the Services or refund the fees paid for the non-conforming portion. This remedy is Customer’s sole and exclusive remedy for breach of this warranty.
- No Vulnerability Guarantee. Customer acknowledges that cybersecurity threat landscapes are dynamic and continuously evolving, and that the identification, detection, or simulation of vulnerabilities, threats, breaches, threat intelligence, or business intelligence is inherently probabilistic. Accordingly, Autnhive makes no representation or warranty that the SAMI Platform or Services will identify all vulnerabilities, misconfigurations, threats, or exposures in Customer’s or any third party’s environment.
- Third-Party Services Disclaimer. The SAMI Platform may interact with, rely upon, or incorporate third-party software, services, tools, or data feeds (including threat intelligence and integrations). Autnhive does not control such third-party services and makes no warranties, express or implied, regarding their performance, availability, accuracy, security, or continued integration.
- False Positives. While Autnhive uses commercially reasonable efforts to minimize false positives and to meet or exceed industry benchmarks in its analysis, simulations, and threat detection mechanisms, it does not guarantee the absence of false positives or false negatives. Customer is solely responsible for reviewing and validating all outputs before relying on them for operational or compliance decisions.
- General Disclaimer. EXCEPT AS EXPRESSLY PROVIDED IN THIS SECTION, THE SAMI PLATFORM, SERVICES, DELIVERABLES, AND ANY RELATED MATERIALS ARE PROVIDED “AS IS” AND “AS AVAILABLE.” AUTNHIVE EXPRESSLY DISCLAIMS ALL OTHER WARRANTIES, EXPRESS, IMPLIED, STATUTORY, OR OTHERWISE, INCLUDING WITHOUT LIMITATION ANY WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE, NON-INFRINGEMENT, ACCURACY, OR THAT THE PLATFORM OR SERVICES WILL BE UNINTERRUPTED, ERROR-FREE, OR FREE FROM VULNERABILITIES OR SECURITY ISSUES.
10. INDEMNIFICATION
The Parties agree to the following indemnification obligations.
- Indemnification by Autnhive. Autnhive shall defend, indemnify, and hold harmless Customer from and against any third-party claims, demands, suits, or proceedings ("Claims") to the extent arising from an allegation that the SAMI Platform, as provided by Autnhive and used by Customer in accordance with this Agreement, infringes any intellectual property rights of a third party.
Autnhive’s indemnification obligations do not apply to Claims arising from:
- (a) Modifications to the Platform not made by Autnhive;
- (b) Use of the Platform in combination with third-party products or services not provided or approved by Autnhive;
- (c) Customer’s use of the Platform in violation of this Agreement or applicable law.
If the Platform becomes, or in Autnhive’s reasonable opinion is likely to become, the subject of a Claim, Autnhive may, at its option and expense:
- (a) Procure for Customer the right to continue using the Platform;
- (b) Replace or modify the Platform to make it non-infringing; or
- (c) Terminate the affected Services and refund any unused, prepaid fees.
- Indemnification by Customer. Customer shall defend, indemnify, and hold harmless Autnhive and its affiliates, officers, employees, and subcontractors from and against all third-party Claims, losses, liabilities, damages, costs, and expenses (including reasonable attorneys’ fees) arising out of or relating to:
- (a) Customer Data or Customer’s use of the Services in violation of law or third-party rights;
- (b) Any unauthorized security testing, simulations, or assessments initiated by Customer or performed without proper third-party consent;
- (c) Customer’s breach of this Agreement or misuse of the SAMI Platform;
- (d) Any failure by Customer to safeguard sensitive outputs or to restrict access by internal personnel in accordance with Section 3.
- Conditions for Indemnification. The indemnified Party must promptly notify the indemnifying Party in writing of any Claim, provide reasonable cooperation and assistance at the indemnifying Party’s expense, and allow the indemnifying Party sole control of the defense and settlement. The indemnifying Party may not settle any Claim that imposes obligations or liability on the indemnified Party without its prior written consent (not to be unreasonably withheld).
11. LIMITATION OF LIABILITY
The Parties agree that liability under this Agreement shall be subject to the limitations set forth below.
- Exclusion of Certain Damages. TO THE MAXIMUM EXTENT PERMITTED BY LAW, IN NO EVENT SHALL EITHER PARTY BE LIABLE TO THE OTHER FOR ANY INDIRECT, INCIDENTAL, SPECIAL, EXEMPLARY, PUNITIVE, OR CONSEQUENTIAL DAMAGES, INCLUDING BUT NOT LIMITED TO LOST PROFITS, LOST REVENUE, BUSINESS INTERRUPTION, OR LOSS OF DATA, EVEN IF SUCH PARTY HAS BEEN ADVISED OF THE POSSIBILITY OF SUCH DAMAGES AND REGARDLESS OF THE THEORY OF LIABILITY.
- Cap on Liability. EXCEPT FOR LIABILITY ARISING FROM A PARTY’S GROSS NEGLIGENCE, WILLFUL MISCONDUCT, BREACH OF CONFIDENTIALITY, OR INDEMNIFICATION OBLIGATIONS UNDER THIS AGREEMENT, THE TOTAL AGGREGATE LIABILITY OF EITHER PARTY UNDER THIS AGREEMENT SHALL NOT EXCEED THE AMOUNTS PAID OR PAYABLE BY CUSTOMER TO AUTNHIVE UNDER THE APPLICABLE ORDER FORM OR SOW IN THE TWELVE (12) MONTHS IMMEDIATELY PRECEDING THE EVENT GIVING RISE TO THE CLAIM.
12. TERM AND TERMINATION
This Agreement shall remain in effect unless terminated in accordance with the provisions set forth below.
- Term. This Agreement shall commence on the Effective Date and shall remain in effect until terminated in accordance with this Section or as otherwise set forth in an applicable Order Form.
- Termination for Convenience. Either Party may terminate this Agreement or any Order Form upon thirty (30) days’ prior written notice to the other Party.
-
Termination for Cause. Either Party may terminate this Agreement or any Order Form immediately upon written notice if the other Party:
- (a) Commits a material breach of this Agreement and fails to cure such breach within thirty (30) days after receiving written notice, or within an approved extension period not exceeding sixty (60) days from the original notice date, provided diligent efforts to cure continue in good faith;
- (b) Becomes insolvent or is subject to bankruptcy, receivership, liquidation, or assignment for the benefit of creditors;
- (c) Violates any applicable law, regulation, or governmental order, including data privacy, export control, or sanctions laws;
- (d) Engages in conduct that could subject Autnhive to legal liability or regulatory penalties; or
- (e) Assigns or attempts to assign this Agreement without Autnhive’s prior written consent.
-
Effect of Termination. Upon expiration or termination of this Agreement for any reason:
- (a) All rights granted to Customer under this Agreement, including access to and use of the Platform, shall immediately terminate;
- (b) Each Party shall promptly return or destroy the other Party’s Confidential Information in accordance with the Confidentiality provisions of this Agreement; and
- (c) All payment obligations accrued as of the date of termination shall become immediately due and payable.
- Early Termination Consequences for Committed Terms. If this Agreement or an applicable Order Form includes a fixed subscription term or annual purchase commitment, and such Agreement or Order Form is terminated by Customer for convenience or by Autnhive pursuant to Sections 12(c) or 12(d), Customer shall remain liable for all fees that would have become due for the remainder of the committed term. Any pricing discounts or overage waivers granted based on the commitment may be retroactively withdrawn, and Autnhive reserves the right to invoice Customer at standard rates.
13. SURVIVAL
The rights and obligations of the Parties under Sections pertaining to Confidentiality, Intellectual Property, Indemnification, Limitation of Liability, and any other provisions which by their nature should survive, shall survive termination or expiration of this Agreement.
14. TERM AND TERMINATION
- Term. The term of this Agreement begins on the Effective Date and continues until terminated in accordance with its terms.
- Termination Rights. Either Party may terminate this Agreement with thirty (30) days’ written notice or immediately upon a material breach by the other Party.
- Post-Termination Obligations. Upon termination, all rights to access and use the Platform shall cease, and all Confidential Information must be returned or securely deleted.
- Immediate Termination Events. Insolvency or assignment without required written consent shall entitle Autnhive to immediately terminate this Agreement.
15. MISCELLANEOUS
- Governing Law. This Agreement shall be governed by and construed in accordance with the laws of the Province of Ontario, Canada, without regard to conflict of laws principles.
- Assignment. Neither Party may assign or transfer this Agreement, in whole or in part, without the prior written consent of the other Party, except to an affiliate or in connection with a merger, acquisition, or sale of all or substantially all of the assigning Party’s assets.
- Audit Rights. Autnhive may, no more than once per calendar year and upon ten (10) business days’ prior written notice, audit Customer’s use of the Autnhive Platform solely to verify compliance with this Agreement, including licensing scope, usage limitations, and financial obligations.
- Audit Procedures. Any audit shall be conducted during regular business hours and in a manner that does not unreasonably disrupt Customer’s normal operations. If the audit reveals unauthorized usage, material non-compliance, or an underpayment exceeding the applicable tolerance threshold or five percent (5%) of fees owed during the audited period, Customer shall promptly pay all outstanding amounts and reimburse Autnhive for the reasonable cost of the audit.
- Non-Solicitation. During the term of this Agreement and for twelve (12) months thereafter, Customer shall not directly or indirectly solicit or hire any employee or contractor of Autnhive who was materially involved in providing the Services without Autnhive’s prior written consent.
- Ethical Use. Customer shall not engage in any conduct, business practice, or marketing activity that could reasonably be expected to harm Autnhive’s reputation or violate applicable laws, regulations, or recognized ethical standards.
- Export Compliance. Each Party agrees to comply with all applicable export control laws and regulations, including those of Canada, the United States, and any other relevant jurisdictions.
- Force Majeure. Neither Party shall be liable for any failure or delay in performance due to causes beyond its reasonable control, including acts of God, war, terrorism, labor disputes, pandemics, or governmental restrictions.
- Independent Parties. The Parties are independent contractors. Neither Party nor their personnel shall be deemed agents, employees, partners, or joint venturers of the other Party, nor shall either Party have authority to bind the other. Autnhive shall remain solely responsible for hiring and managing personnel necessary to perform the Services.
- Government Use. If the Autnhive Platform is licensed for use by any government agency, it is provided as “Commercial Computer Software,” and its use, duplication, or disclosure shall be subject to applicable commercial software restrictions under law.
- Entire Agreement. This Agreement, together with all Order Forms, Schedules, and Statements of Work incorporated by reference, constitutes the entire agreement between the Parties and supersedes all prior or contemporaneous understandings, proposals, and agreements, whether written or oral, relating to its subject matter.
IN WITNESS WHEREOF, the Parties have caused this Agreement to be executed by their duly authorized representatives.
16. Contact
Data controller: Autnhive Inc., Toronto, Ontario, Canada.
Privacy enquiries: legal@autnhive.com
This Terms of Service Agreement (“Agreement”) constitutes a binding legal contract between you (“You” or “User”) and Autnhive, Inc. (“Autnhive,” “Company,” “we,” or “us”), governing your access to and use of the website located at [www.autnhive.com] and any affiliated websites or services (collectively, the “Site”).
BY ACCESSING OR USING THE SITE, YOU ACKNOWLEDGE THAT YOU HAVE READ, UNDERSTOOD, AND AGREED TO BE BOUND BY THESE TERMS AND THE PRIVACY POLICY. IF YOU DO NOT AGREE, YOU MUST NOT ACCESS OR USE THE SITE.
1. License and Restrictions on Use
Autnhive grants You a limited, non-exclusive, non-transferable, and revocable license to access and use the Site solely for lawful, personal, and non-commercial purposes, subject to these Terms. You shall not:
- a. Reproduce, modify, distribute, or publicly display the Site or its content for commercial purposes without Autnhive’s prior written consent;
- b. Use data mining, scraping, robots, or similar data gathering methods;
- c. Frame or mirror any part of the Site or circumvent any security or access restrictions;
- d. Upload or transmit malicious code, viruses, or engage in activity that interferes with the Site’s operation;
- e. Use the Site in violation of any applicable law or regulation.
2. Use of Site Materials
All materials and content made available on or through the Site, including text, images, graphics, sound, video, software, and documentation (“Materials”), are owned by or licensed to Autnhive or its third-party providers and are protected by intellectual property laws. You shall not:
- a. Reproduce, republish, upload, post, transmit, or distribute any Materials without Autnhive’s prior written permission;
- b. Use Materials for commercial or derivative purposes unless expressly permitted in writing;
- c. Rely on Materials for accuracy or fitness for any specific purpose. Materials may be inaccurate, outdated, or incomplete and are provided “AS IS.”
3. Account Responsibilities
If you create an account on the Site, you agree to:
- a. Maintain the confidentiality of your username and password;
- b. Accept responsibility for all activity under your account;
- c. Notify Autnhive immediately of any unauthorized use or security breach;
- d. Autnhive reserves the right to suspend or terminate accounts at its sole discretion.
4. Purchases and Transactions
All purchases of Autnhive’s products or services are governed by additional terms that will be presented at the time of transaction. Unless stated otherwise:
- a. All purchases are final and provided “AS IS” without warranties;
- b. Autnhive disclaims all liability for errors, delivery issues, pricing changes, or product availability;
- c. You agree to be bound by any additional terms applicable to promotions, discounts, or product offerings.
5. Third-Party Links and Content
The Site may include links to third-party websites for your convenience. Autnhive does not control, endorse, or assume any responsibility for third-party content, availability, or actions. Use of such websites is at your own risk. You are solely responsible for taking appropriate precautions to protect yourself from malware, phishing, or other harmful content.
6. Electronic Communications
By using the Site or communicating electronically with Autnhive, you consent to receive communications electronically, including notices, agreements, disclosures, and other communications that satisfy legal requirements for written communication.
7. Government Use
Any software or Materials provided through the Site for Government use are provided with restricted rights. Use, duplication, or disclosure is subject to applicable regulations under DFARS 227.7202-3 or FAR 52.227-19.
8. User Submissions
Unless otherwise agreed in writing, any comments, feedback, data, or other submissions provided by you to Autnhive (“Submissions”) shall be considered non-confidential and become the property of Autnhive. You agree to:
- a. Assign to Autnhive all rights, title, and interest in any Submissions;
- b. Warrant that Submissions are lawful and do not infringe any third-party rights;
- c. Authorize Autnhive to use, display, modify, and distribute Submissions without restriction or compensation.
9. Disclaimer of Warranties
THE SITE AND ALL MATERIALS ARE PROVIDED ON AN “AS IS” AND “AS AVAILABLE” BASIS. AUTNHIVE EXPRESSLY DISCLAIMS ALL WARRANTIES, EXPRESS OR IMPLIED, INCLUDING, WITHOUT LIMITATION, WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE, NON-INFRINGEMENT, AND ACCURACY. AUTNHIVE DOES NOT WARRANT THAT:
- a. THE SITE OR MATERIALS WILL BE ERROR-FREE OR UNINTERRUPTED;
- b. DEFECTS WILL BE CORRECTED;
- c. ANY CONTENT IS ACCURATE, CURRENT, OR RELIABLE;
- d. SOME JURISDICTIONS MAY NOT ALLOW THE EXCLUSION OF CERTAIN WARRANTIES. IN SUCH CASES, AUTNHIVE’S LIABILITY IS LIMITED TO THE MAXIMUM EXTENT PERMITTED BY LAW.
10. Limitation of Liability
TO THE MAXIMUM EXTENT PERMITTED BY LAW, IN NO EVENT SHALL AUTNHIVE BE LIABLE FOR ANY INDIRECT, INCIDENTAL, CONSEQUENTIAL, SPECIAL, EXEMPLARY, OR PUNITIVE DAMAGES WHATSOEVER, INCLUDING BUT NOT LIMITED TO DAMAGES FOR LOST PROFITS, LOSS OF DATA, BUSINESS INTERRUPTION, OR OTHER ECONOMIC LOSS, ARISING OUT OF OR IN CONNECTION WITH YOUR USE OF THE SITE OR RELIANCE ON MATERIALS, EVEN IF ADVISED OF THE POSSIBILITY OF SUCH DAMAGES. YOUR SOLE AND EXCLUSIVE REMEDY IS TO DISCONTINUE USING THE SITE.
11. Indemnification
You agree to indemnify, defend, and hold harmless Autnhive, its affiliates, officers, directors, employees, agents, licensors, service providers, successors, and assigns from and against all claims, damages, liabilities, losses, costs, and expenses (including attorneys’ fees) arising from or related to:
- a. Your access to or use of the Site;
- b. Your reliance on any Site content;
- c. Your violation of these Terms or any applicable law;
- d. Any Submission or content you provide;
- e. Your infringement of any intellectual property, privacy, or other rights of a third party;
- f. This indemnification obligation survives termination of this Agreement.
12. Force Majeure
Autnhive shall not be held liable for any failure or delay in performance caused by events beyond its reasonable control, including but not limited to acts of God, war, cyberattacks, labor disputes, supply chain disruption, pandemics, or internet outages.
13. Arbitration; Waiver of Class Actions
All disputes arising out of or relating to these Terms shall be resolved through binding arbitration in accordance with the rules of the Canadian Arbitration Association. You agree to resolve disputes on an individual basis and waive any right to participate in class actions or jury trials. Venue for any arbitration shall be Oakville, Ontario.
14. Export Compliance
You agree to comply fully with all U.S. and Canadian export control laws and regulations. You shall not export or re-export any Materials or software obtained from the Site to any country or entity prohibited by applicable law, including embargoed nations or sanctioned individuals.
15. Modifications to Terms
Autnhive reserves the right to modify these Terms at any time by posting updated terms on the Site. Your continued use of the Site after such changes constitutes your acceptance of the revised Terms.
16. Governing Law and Jurisdiction
These Terms shall be governed by and construed in accordance with the laws of the Province of Ontario and applicable federal laws of Canada, without regard to conflict of laws principles. You consent to the exclusive jurisdiction and venue of Courts located in Halton Region, Ontario.
17. Entire Agreement; Severability
These Terms constitute the entire agreement between you and Autnhive concerning the subject matter herein. If any provision is found unenforceable, the remaining provisions shall remain in full force and effect. Failure to enforce any provision shall not constitute a waiver of that right.
18. Intellectual Property Notices
The Site and all Materials are protected by copyright, trademark, and other intellectual property laws. Autnhive’s name, logos, and related marks are trademarks of Autnhive, Inc. You may not use such marks without prior written permission. Other product and company names may be trademarks of their respective owners.
19. Copyright Infringement (DMCA Notice)
If you believe your work has been used in a way that constitutes copyright infringement, please contact our Copyright Agent with the following:
- a. Your physical or electronic signature;
- b. Identification of the copyrighted work;
- c. Description of the infringing material;
- d. Your contact details;
- e. A statement of good faith belief the use is unauthorized;
- f. A statement made under penalty of perjury of accuracy and authority.
20. Contact
For questions regarding these Terms or to request permissions, contact: legal@autnhive.com
Data Processing Agreement (DPA) Standard Terms. This is our standard DPA for GDPR and PIPEDA compliance. A signed, countersigned DPA is available on request. Contact: info@autnhive.com
1. Scope and Roles
This DPA applies where Autnhive processes personal data on your behalf as part of the SAMI service. You are the data controller; Autnhive is the data processor. Where Autnhive processes data for its own purposes (e.g., account management), Autnhive is an independent controller.
2. Subject Matter
Autnhive processes personal data only as necessary to provide the SAMI service: security assessment findings, remediation tracking, compliance evidence generation. The categories of data subjects are your employees, contractors, and system users whose activity is monitored by SAMI.
3. Processing Instructions
Autnhive processes personal data only on documented instructions from you. The service agreement constitutes your initial instructions. You may provide further written instructions at any time. Autnhive will notify you if any instruction appears to violate applicable data protection law.
4. Confidentiality
Autnhive personnel with access to personal data are bound by confidentiality obligations. Access is restricted to personnel whose role requires it. Background checks and security training required for all personnel with data access.
5. Sub-processors
Autnhive's current sub-processors: Oracle Cloud Infrastructure (Canada/EU hosting), SendGrid (email delivery). We provide 30 days advance notice of sub-processor changes. You may object to new sub-processors within 14 days. All sub-processors are bound by equivalent data protection obligations.
6. Security Measures
Autnhive implements Article 32 GDPR technical and organizational measures: encryption in transit (TLS 1.3) and at rest (AES-256), access controls and MFA, regular penetration testing, ISO 27001 and SOC 2 Type II certification, incident response procedures with 72-hour breach notification capability.
7. Data Subject Rights
Autnhive will assist you in fulfilling data subject rights requests within 5 business days of your request. Autnhive will not respond directly to data subjects without your authorisation except where legally required.
8. Data Breach Notification
Autnhive will notify you of a personal data breach within 48 hours of becoming aware. Notification will include the nature of the breach, categories and approximate number of individuals affected, likely consequences, and measures taken or proposed. This supports your 72-hour GDPR notification obligation.
9. Data Transfers
Data is processed in Canada (adequacy decision) and EU-based Oracle Cloud regions. No transfers to countries without adequate protection without appropriate safeguards (SCCs or equivalent).
10. Return and Deletion
On termination of the service, Autnhive will provide a data export within 30 days and delete all personal data within 60 days of export confirmation, unless legal retention obligations apply. Zero Telemetry deployments have no Autnhive-side data to return.
11. Audits
You may request audit evidence (SOC 2 report, ISO 27001 certificate, penetration test summary) once per year. On-site audits available with 30 days notice and reasonable cost reimbursement.
12. BAA (HIPAA)
A HIPAA Business Associate Agreement is available for covered entities. The BAA covers SAMI's processing of protected health information (PHI) in clinical AI deployments. SAMI's tokenization architecture processes tokens, not PHI but the BAA covers the full service scope regardless.
To request a signed DPA or BAA: info@autnhive.com
This Privacy Policy explains how Autnhive Corporation (“Autnhive,” “we,” “us,” or “our”) collects, uses, discloses, and protects personal data when you visit our website, create an account, use our Services, or otherwise interact with us. It is designed to meet the requirements of the EU General Data Protection Regulation (Regulation (EU) 2016/679) and the UK GDPR (together, “GDPR”), and the California Consumer Privacy Act as amended by the California Privacy Rights Act (Cal. Civ. Code § 1798.100 et seq.) (“CCPA”).
1. Introduction
Autnhive Corporation (“Autnhive,” “we,” “us,” or “our”) provides AI security and compliance products, including SAMI, together with our corporate website and related online services (collectively, the “Services”). This Privacy Policy explains how we collect, use, disclose, and protect personal data when you visit our website, create an account, use our Services, or otherwise interact with us.
This Policy is designed to meet the requirements of the EU General Data Protection Regulation (Regulation (EU) 2016/679) and the UK GDPR (together, “GDPR”), and the California Consumer Privacy Act as amended by the California Privacy Rights Act (Cal. Civ. Code § 1798.100 et seq.) (“CCPA”). Where this Policy grants rights or protections beyond what a particular law requires, we intend those protections to apply to all visitors, regardless of location, unless stated otherwise.
2. Scope
This Policy applies to personal data processed through our public website and marketing activities. It does not govern personal data that Autnhive processes on behalf of customers as a data processor/service provider within the Autnhive platforms; that processing is governed by the applicable Data Processing Agreement (DPA) executed with each customer.
3. Who We Are
For the purposes of GDPR, Autnhive Corporation is the data controller of personal data collected through this website. For the purposes of CCPA, Autnhive is a “business” as defined in Cal. Civ. Code § 1798.140.
- Data Protection Officer: info@autnhive.com
- Registered Address: 2275 Upper Middle Rd E, Oakville, ON L6H 0C3, Canada.
4. Categories of Personal Data We Collect
We collect personal data directly from you, automatically through our use of the website, and from third parties. The categories below are consistent with the CCPA categories in Cal. Civ. Code § 1798.140(v).
- Identifiers: Name, work email, company name, phone number, IP address, account username.
- Commercial information: Products/services considered, subscription.
- Internet/network activity: Browsing behaviour on our site, pages visited, referring URL, clickstream data, device and browser type, cookie identifiers.
- Geolocation data: Approximate location inferred from IP address.
- Professional/employment information: Employer, job function, industry, seniority level (collected via forms, demo requests, or LinkedIn lead-gen integrations).
- Inferences: Interests and preferences inferred from engagement with content, for marketing personalization.
- Audio/electronic records: Recordings of sales calls or webinars where you have been notified and, where required, consented.
We do not knowingly collect sensitive personal data (as defined under GDPR Art. 9 or CCPA § 1798.140(ae)) through the website. Please do not submit sensitive personal data through contact forms, support tickets, or chat unless specifically requested.
5. Use of Artificial Intelligence
Some of our products use artificial intelligence to analyze security data and generate recommendations. Unless otherwise agreed with our customers, data submitted through customer environments is processed solely to provide the requested services and is not used to train publicly available AI models.
6. How We Collect Personal Data
- Directly from you: When you fill out a contact us or Book PoV form, register for an account, subscribe to a newsletter, apply for a job, or correspond with our sales or support teams.
- Automatically: Through cookies, pixels, server logs, and similar tracking technologies when you browse the website.
- From third parties: Business partners, resellers, marketing platforms (e.g., LinkedIn Campaign Manager, Google Ads), data enrichment providers, and publicly available sources.
7. Purposes of Processing and GDPR Legal Bases
Under GDPR, we rely on the following legal bases (Art. 6(1)) for each purpose of processing:
| Purpose | Legal Basis |
|---|---|
| Operating and securing the website; fraud and abuse prevention | Legitimate interests (Art. 6(1)(f)) |
| Responding to inquiries, providing demos, account provisioning | Performance of a contract / pre-contractual steps (Art. 6(1)(b)) |
| Sending marketing communications | Consent (Art. 6(1)(a)), or legitimate interests for existing B2B customers where permitted by local law, with an opt-out on every communication |
| Analytics and site personalization (non-essential cookies) | Consent (Art. 6(1)(a)), obtained via cookie banner |
| Complying with legal, tax, and regulatory obligations | Legal obligation (Art. 6(1)(c)) |
| Establishing, exercising, or defending legal claims | Legitimate interests (Art. 6(1)(f)) |
You may withdraw consent at any time where processing is based on consent, without affecting the lawfulness of processing carried out before withdrawal. To withdraw consent to marketing, use the unsubscribe link in any email or contact us using the details in Section 12.
8. How We Share Personal Data
We do not sell personal data in the traditional sense of exchanging it for money.
We disclose personal data to the following categories of recipients, each bound by contractual confidentiality and data protection obligations:
- Service providers and processors: Cloud hosting, CRM, email delivery, customer support, and analytics vendors acting on our instructions.
- Professional advisors: Legal, accounting, and audit firms, where necessary.
- Corporate transactions: An acquirer or successor in the event of a merger, acquisition, financing, or sale of assets.
- Regulators and authorities: Where required by law, court order, or to protect Autnhive's rights, property, or safety, or that of others.
- With your direction or consent: For example, where you ask us to share information with a named business partner.
Sub-processors
Autnhive engages a limited set of sub-processors to operate the website and marketing stack (for example, cloud infrastructure, email delivery, and analytics providers). An up-to-date list of website sub-processors is available on request from the Data Protection Officer and is reviewed at least annually.
Third-Party Websites and Links
Our website may contain links to third-party sites, including integrations, partner pages, or content embedded from platforms such as LinkedIn or YouTube. This Policy does not apply to those third parties, and we encourage you to review their privacy policies before providing personal data to them.
International Data Transfers
Autnhive may transfer personal data outside the European Economic Area, the UK, or your home jurisdiction to countries that may not have equivalent data protection laws, including for hosting and support functions. Where we do so, we rely on recognized transfer mechanisms, including the European Commission's Standard Contractual Clauses, the UK International Data Transfer Addendum, or adequacy decisions, as applicable. A copy of the relevant safeguard can be requested from the Data Protection Officer.
9. Cookies and Tracking Technologies
We use cookies, web beacons, and similar technologies for the following purposes:
- Strictly necessary: Session management, load balancing, security cannot be disabled and do not require consent.
- Functional: Remembering preferences such as language or region.
- Analytics: Understanding site usage to improve content and performance (e.g., aggregated traffic analytics).
- Advertising/marketing: Measuring campaign effectiveness and delivering relevant ads across platforms; may involve sharing identifiers with ad-tech partners.
On your first visit, a cookie banner allows you to accept or reject non-essential cookies and to manage preferences by category, consistent with GDPR consent requirements. You may also control cookies through your browser settings. Because rejecting certain cookies may affect site functionality, essential cookies cannot be disabled through the banner.
For more information about the cookies we use and how to manage your preferences, please see our Cookie Policy.
10. Your California Privacy Rights (CCPA/CPRA)
If you are a California resident, you have the following rights, subject to certain exceptions:
- Right to know/access: The categories and specific pieces of personal information we have collected, the sources, the purposes, and the categories of third parties with whom it is disclosed.
- Right to delete: Request deletion of personal information we have collected from you, subject to legal exceptions.
- Right to correct: Request correction of inaccurate personal information.
- Right to opt out of sale/sharing: Opt out of the “sale” or “sharing” (as CCPA defines those terms, including for cross-context behavioral advertising) of your personal information.
- Right to limit use of sensitive personal information: Where applicable.
- Right to non-discrimination: We will not discriminate against you for exercising any CCPA right.
To exercise these rights, submit a request through the contact details. We will verify your identity before processing a request and will respond within the timeframes required by the CCPA (generally 45 days, extendable once by an additional 45 days with notice).
You may designate an authorized agent to submit a request on your behalf, subject to verification. We do not sell or share the personal information of consumers we know to be under 16 years of age without affirmative authorization.
11. Your GDPR Rights
If you are located in the EEA or UK, you have the following rights under GDPR, subject to certain exceptions:
- Right of access (Art. 15) : Obtain confirmation of and access to your personal data.
- Right to rectification (Art. 16) : Correct inaccurate or incomplete data.
- Right to erasure (Art. 17) : Request deletion in certain circumstances.
- Right to restrict processing (Art. 18).
- Right to data portability (Art. 20) : Receive your data in a structured, machine-readable format.
- Right to object (Art. 21) : Including to processing for direct marketing at any time.
- Rights related to automated decision-making and profiling (Art. 22), where applicable.
- Right to withdraw consent at any time, without affecting prior lawful processing.
- Right to lodge a complaint with a supervisory authority : In the EU, your local Data Protection Authority; in the UK, the Information Commissioner's Office (ICO).
To exercise any of these rights, contact the Data Protection Officer using the details in Section 15. We will respond within one month, extendable by two further months for complex requests, in accordance with Art. 12 GDPR.
12. Rights for Other U.S. State Residents
If you are a resident of Virginia, Colorado, Connecticut, Utah, or another U.S. state with a comprehensive privacy law, you may have rights similar to those described in Section 9, including the right to access, correct, delete, and port your personal data, and to opt out of targeted advertising, the sale of personal data, or profiling in furtherance of decisions that produce legal or similarly significant effects. You may exercise these rights using the contact details in Section 13. If we deny a request, some state laws give you the right to appeal; instructions will be provided in our response.
13. Data Breach Notification
In the event of a personal data breach that poses a risk to your rights and freedoms, Autnhive will notify affected individuals and relevant regulators without undue delay, and in line with applicable legal timelines including the 72-hour notification requirement to supervisory authorities under GDPR Art. 33, where applicable.
14. Data Retention and Security
We retain personal data only for as long as necessary to fulfil the purposes for which it was collected, including to satisfy legal, accounting, or reporting requirements. Website form submissions and marketing contact data are generally retained for the duration of the business relationship plus 7 years thereafter, unless a longer period is required by law or you request deletion sooner.
We implement technical and organizational security measures appropriate to the risk, consistent with our ISO 27001, GDPR, CCPA aligned information security and privacy management system, including encryption, access controls, monitoring, and other appropriate administrative, technical, and organizational safeguards. No method of transmission or storage is completely secure, and we cannot guarantee absolute security.
15. Children's Privacy
Our website and Services are directed at business professionals and are not intended for individuals under the age of 16. We do not knowingly collect personal data from children. If we become aware that we have inadvertently collected data from a child, we will take steps to delete it.
16. Changes to This Policy
You should review this Privacy Policy on a routine basis as Autnhive reserves the right to change this Privacy Policy, or any portion thereof, an updated version of our Privacy Policy will be posted to our website.
17. Contact Us
For any questions about this Policy, or to exercise your privacy rights, please contact:
Data Protection Officer
2275 Upper Middle Rd E, Oakville
ON L6H 0C3, Canada.
info@autnhive.com
Version: 1.1
Date: 30 Jul 2026
Last updated: April 11, 2026. This Cookie Policy explains how Autnhive uses cookies and similar tracking technologies on autnhive.com. You can manage cookie preferences at any time using your browser settings.
1. What Are Cookies
Cookies are small text files stored in your browser when you visit a website. They allow the site to recognise your device and remember preferences. We also use local storage and session storage for functional purposes.
2. Cookies We Use
Essential Cookies (always active)
- Session management: maintain your login state and preferences during a session. Deleted on browser close.
- Security: CSRF protection tokens, rate-limiting identifiers. Required for the service to function securely.
- Cookie consent: remember your cookie preference choices.
Analytics Cookies (consent required)
- Usage analytics: anonymised page views, time on page, navigation paths to understand how the site is used and improve it. No personal identifiers stored.
- We use server-side analytics that do not set third-party cookies where possible.
What We Do NOT Use
- No advertising or retargeting cookies
- No social media tracking pixels
- No cross-site tracking
- No fingerprinting or behavioural profiling
3. Managing Cookies
You can block or delete cookies through your browser settings. Essential cookies cannot be disabled without affecting core site functionality. For analytics cookies, use your browser's "Do Not Track" setting or contact us to opt out.
4. Contact
Cookie or tracking enquiries: info@autnhive.com
Last updated: April 11, 2026. Autnhive's security programme is built to the same standard we hold our customers to. We publish this policy so you can independently assess our security posture before trusting us with your environment.
1. Security Certifications
- ISO 27001:2022 certified
- SOC 2 Type II attested
- GDPR compliant
- HIPPA compliant
- CCPA compliant
2. Infrastructure Security
- Cloud: Oracle Cloud Infrastructure, certified data centres (Canada, EU)
- Encryption: TLS 1.3 in transit, AES-256 at rest, key management via OCI Vault
- Network: WAF, DDoS protection, private networking between components
- Access: MFA required for all Autnhive personnel, just-in-time access provisioning
3. Application Security
- Security-by-design development practices, OWASP ASVS Level 2 compliance target
- Automated SAST/DAST in CI/CD pipeline for every code change
- Annual external penetration test by independent firm
- Dependency scanning and SBOM maintained for all production software
4. Vulnerability Disclosure
We welcome responsible disclosure of security vulnerabilities. Please report to info@autnhive.com with "Vulnerability Disclosure" in the subject. We commit to: acknowledge within 24 hours, provide a resolution timeline within 5 business days, not pursue legal action against good-faith researchers.
5. Incident Response
- 24/7 security monitoring via SAMI (we use our own platform)
- Incident response team on-call, CSIRT procedures in place
6. Personnel Security
- Background checks for all personnel with system access
- Security awareness training quarterly
- Least-privilege access model, access reviewed quarterly
7. Penetration Test Summary
Annual penetration test conducted by independent security firm. Most recent: Q1 2026. Scope: full platform including AI components, cloud infrastructure, and APIs. All critical and high findings remediated before publication. Executive summary available to customers under NDA.
8. Contact
Security enquiries and vulnerability reports: info@autnhive.com
Get in touch
Talk to the
SAMI team.
Whether you're evaluating AI security options, want to run a proof of value, or have a specific risk question we'll give you a direct, honest answer.

2275 Upper Middle Rd E, Oakville, ON L6H 0C3, Canada.(Headquarters)

41000 Woodward Ave, Bloomfield Hills, MI 48304, United States.

CITUS A Block Phase 1 Olympia Tech Park, Chennai, Tamil Nadu, 600032, India.
Try it out
Try & Simulate
SAMI Assessments.
Validate and initiate request for multiple assessments. Including External surface assessment, Mobile app. Try out AI security features
Validate & Try
About Autnhive
We built SAMI because
AI risk had no answer.
Autnhive was founded on a simple belief: organizations should be able to adopt AI faster without losing control of security, privacy, or compliance.
Devi Narayan
Founder & CEO, Autnhive
A message from our CEO
AI should accelerate human progress without putting people, data, or trust at risk. SAMI exists to make safe, transparent, and controlled AI adoption possible.
AI will become one of the most important forces shaping how organizations operate, compete, serve customers, and make decisions. But AI cannot reach its full potential if organizations are forced to choose between innovation and control.
The future belongs to organizations that can adopt AI quickly, securely, privately, and compliantly. That is why we created SAMI for AI: to accelerate AI adoption by making every AI interaction safer, more private, and compliant by design.
SAMI gives organizations the control layer they need to discover AI use, protect sensitive data, detect live attacks, manage AI and cyber exposure, enforce privacy and compliance rules, and prove what happened when AI systems are used. We are building technology that helps AI move from experimentation to trusted, enterprise-scale adoption.
But Autnhive is not only a technology company. It is a company built around people and trust.
For our customers, we are building a platform that helps them move faster without creating unnecessary risk. They should not have to choose between AI innovation and security, privacy, or compliance. SAMI is designed to help them adopt AI with confidence.
For our employees, we are building a company where talented people can do meaningful work, solve hard problems, and take pride in creating technology that matters. Our team is the foundation of everything we build.
For our investors, we are building a company with the ambition, discipline, and market opportunity to become a global leader in AI security, privacy, compliance, and continuous threat exposure management.
For our partners, we are building an ecosystem that helps bring safe, secure, and compliant AI adoption to more organizations, industries, and communities.
We believe trusted AI will define the next generation of business. Autnhive exists to make that future possible.
Devi
mission
To create the most consequential security, privacy, and compliance platform for AI,
enabling faster and safer AI adoption for everyone.
Visibility first.
You cannot secure what you cannot see. SAMI shows who is using AI, what models are doing, what data they touch, which agents act, and where exposure exists in real time what are the vulnerabilities in your AI systems have and helping to fix them.
Risk in business terms.
AI risk cannot stay buried in technical scores. SAMI translates exposure into financial, regulatory, and operational impact so security leaders, executives, insurers, and boards can act.
Protection at runtime.
Finding risk is not enough. SAMI helps enforce policies, block unsafe actions, redact or transform sensitive data, stop attacks, and keep AI aligned with security, privacy, and compliance requirements.
Closed, not just found.
The industry often measures security by what gets discovered. We measure it by what gets fixed. SAMI helps teams manage AI risk all the way to closure.
Get in touch
Open roles
Careers at Autnhive
Build the platform that
makes AI risk visible.
We are a small team solving a real problem at the intersection of AI, security, and financial risk quantification. If that is where you want to be working, read on.
All roles
India
Canada
USA
Loading roles...
Why Autnhive
Real problem, real urgency
The AI security gap is not hypothetical. Every week brings a new incident. You will be working on something that matters and is needed now.
Small team, large ownership
Every person owns significant surface area and sees their work in production quickly.
Distributed from day one
Teams across India, Canada, and the US. Remote-first with intentional collaboration.
Do not see a role that fits? We are always interested in people who care about AI security, risk quantification, or developer tooling. Send a note directly
Sample Evidence Receipt
Agent Tool Misuse Blocked
1. Event Summary
Agent requested a high-risk shell command during an active workflow run. Event captured and routed to SAMI Proof Ledger.
2. SAMI Decision
Blocked. Matched policy: restricted tool execution shell commands. Escalation not required.
3. Action / Runtime Evidence
Tool call intercepted before execution. No side effect occurred. Agent run halted at the blocked step.
4. Threat Mapping
Agent tool misuse unauthorized privileged command execution attempt.
5. Compliance Mapping
Mapped to SOC 2 access control evidence and internal AI governance policy.
6. Remediation
No remediation required block was enforced as designed. Logged for review.
7. Cryptographic Evidence
Event fingerprint: a13f...9c2e (sample, redacted)
8. Proof Path
Proof path verified against batch root. Path depth: 4 nodes (sample).
9. Verification Steps
Fingerprint recomputed, hash chain verified, proof path verified, batch root matched, signed checkpoint validated.
10. Export Options
Available as PDF, JSON, or SIEM-ready event object.